
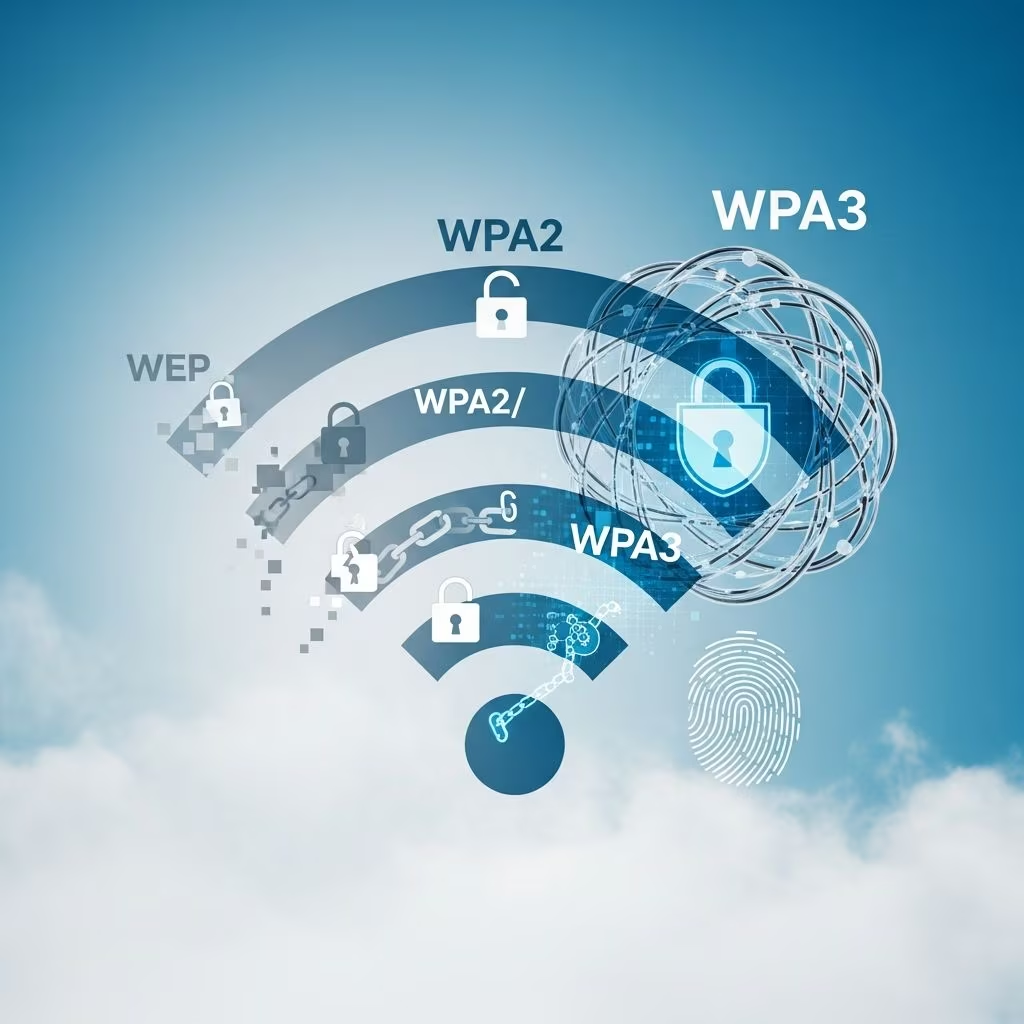
Wireless networks have become the backbone of modern connectivity, powering everything from home internet to enterprise systems. However, with convenience comes risk. Unsecured Wi-Fi can expose sensitive data to eavesdroppers, hackers, and malicious actors. Encryption protocols are the first line of defense, transforming readable data into unreadable code that only authorized users can decode. This comprehensive guide traces the journey from the flawed beginnings of WEP to the cutting-edge protections of WPA3, helping you understand how to safeguard your network effectively.
The Foundations of Wi-Fi Security
Encryption in wireless LANs (WLANs) works by scrambling data packets transmitted over the air. Devices must share cryptographic keys to encrypt and decrypt this information. Early protocols struggled with key management and weak algorithms, leading to widespread vulnerabilities. Today, standards have evolved to incorporate stronger ciphers, better authentication, and resistance to common attacks like brute-force and man-in-the-middle exploits.
Key benefits of robust encryption include:
- Preventing unauthorized access to network traffic.
- Protecting against data interception in public or crowded environments.
- Ensuring compliance with regulations like GDPR and HIPAA.
- Enhancing overall device interoperability across vendors.
Breaking Down WEP: The Original but Obsolete Standard
Wired Equivalent Privacy (WEP) was introduced in 1997 as part of the IEEE 802.11 standard to provide confidentiality equivalent to wired networks. It used the RC4 stream cipher with 40-bit or 104-bit keys, but implementation flaws doomed it from the start.
Problems with WEP included:
- Static keys: Shared across all users, making them easy to discover via packet sniffing.
- Weak initialization vectors (IVs): 24-bit IVs repeated frequently, allowing attackers to collect enough data for statistical attacks.
- No integrity checks: Modified packets could go undetected.
By 2001, tools like Aircrack-ng could crack WEP keys in minutes. The Wi-Fi Alliance deprecated WEP in 2004, yet legacy devices still support it, posing risks if enabled. Organizations should immediately disable WEP and upgrade hardware.
WPA: A Quick Fix with Lingering Issues
Wi-Fi Protected Access (WPA) emerged in 2003 as an interim solution while IEEE developed a full replacement. It replaced WEP’s RC4 with Temporal Key Integrity Protocol (TKIP), which dynamically generates keys per packet and includes a message integrity check (MIC).
While WPA improved security, it wasn’t foolproof:
- Beck-Tews attack: Exploited TKIP weaknesses to inject packets or decrypt small amounts of data.
- Legacy compatibility: Often run in mixed mode with WEP, diluting protections.
- Pre-shared key (PSK) vulnerabilities: Weak passphrases susceptible to offline dictionary attacks.
WPA marked progress but was designed as a stopgap. By 2004, it gave way to its successor amid growing exploits.
WPA2: The Long-Reigning Champion
Ratified as IEEE 802.11i in 2004, WPA2 became the gold standard for over a decade. It introduced Counter Mode Cipher Block Chaining Message Authentication Code Protocol (CCMP) based on Advanced Encryption Standard (AES), a symmetric cipher approved for U.S. government top-secret data.
| Feature | WPA2 Personal (PSK) | WPA2 Enterprise (802.1X) |
|---|---|---|
| Authentication | Pre-shared passphrase | RADIUS server with EAP |
| Encryption | AES-CCMP | AES-CCMP |
| Key Management | 4-way handshake | Dynamic per-user keys |
| Best For | Homes/Small offices | Corporations |
WPA2’s 4-way handshake securely exchanges keys during connection. However, the 2017 KRACK (Key Reinstallation Attack) exposed flaws in this process, allowing session key reuse without full passphrase compromise. Dictionary attacks on PSK remained viable against weak passwords. Despite patches, WPA2’s ubiquity makes it a target.
WPA3: The Modern Fortress
Released by the Wi-Fi Alliance in 2018, WPA3 addresses WPA2’s shortcomings with Simultaneous Authentication of Equals (SAE), replacing PSK with a dragonfly handshake resistant to offline attacks. It mandates 192-bit cryptographic strength in enterprise mode and introduces protections for open networks.
Standout WPA3 features:
- Perfect Forward Secrecy (PFS): Each session uses unique keys; compromising one doesn’t affect others.
- Opportunistic Wireless Encryption (OWE): Encrypts open networks without authentication.
- Wi-Fi Easy Connect: QR-code onboarding for IoT devices.
- Enhanced defenses: Against KRACK, downgrade attacks, and side-channel leaks.
Adoption lags due to hardware requirements, but WPA3/WPA2 transitional modes ease migration. As of 2026, most new routers support it fully.
Comparing Protocols: A Side-by-Side Analysis
| Protocol | Cipher | Key Size | Vulnerabilities | Status |
|---|---|---|---|---|
| WEP | RC4 | 40/104-bit | IV reuse, no integrity | Deprecated |
| WPA | TKIP | 128-bit | Beck-Tews, dictionary | Deprecated |
| WPA2 | AES-CCMP | 128/192/256-bit | KRACK, PSK attacks | Legacy |
| WPA3 | AES-GCMP | 128/192-bit | Few; emerging threats | Current |
Real-World Vulnerabilities and Attack Vectors
Attackers exploit weak encryption via:
- Packet sniffing: Capturing unencrypted or weakly encrypted traffic.
- Deauthentication floods: Forcing reconnects to capture handshakes.
- Evil twin APs: Rogue hotspots mimicking legitimate ones.
- Fragility in mixed modes: Forcing devices to fallback to weaker protocols.
Mitigate with strong passphrases (20+ characters, mixed case/symbols), regular firmware updates, and WPA3-only modes where possible.
Implementing Secure Wireless Networks
Follow these steps for bulletproof Wi-Fi:
- Assess hardware: Ensure all devices support WPA3; replace WEP/WPA relics.
- Choose mode wisely: WPA3 Personal for homes; Enterprise for businesses.
- Hide SSID: Reduces visibility, though not foolproof.
- Enable MAC filtering and guest networks.
- Monitor with tools: Wireshark for traffic analysis, WIPS for intrusion detection.
For enterprises, integrate with NAC systems and conduct annual pentests.
Future Directions in Wi-Fi Encryption
Wi-Fi 7 (802.11be) builds on WPA3 with multi-link operations and 4096-QAM, demanding even stronger security. Quantum-resistant algorithms loom on the horizon to counter future computing threats. Expect WPA4 by 2030, focusing on AI-driven anomaly detection and zero-trust models.
Frequently Asked Questions (FAQs)
Is WPA2 still safe in 2026?
With patches and strong passphrases, yes for now—but migrate to WPA3 promptly.
Can I use WPA3 on older devices?
No; requires compatible hardware. Use WPA2/WPA3 mixed mode as a bridge.
How long should my Wi-Fi password be?
At least 20 characters with uppercase, lowercase, numbers, and symbols.
What’s the difference between WPA3-Personal and Enterprise?
Personal uses a single passphrase; Enterprise uses per-user certificates via RADIUS.
Should I disable older protocols?
Absolutely—set to WPA3-only to prevent downgrade attacks.
References
- IEEE Standard for Information Technology—Telecommunications and Information Exchange Between Systems Local and Metropolitan Area Networks—Specific Requirements – Part 11: Wireless LAN Medium Access Control (MAC) and Physical Layer (PHY) Specifications Amendment 6: Enhanced Open Protocol for Authentication — IEEE. 2018-06-25. https://standards.ieee.org/ieee/802.11/6212/
- Wi-Fi CERTIFIED WPA3™ Specification, Version 1.0 — Wi-Fi Alliance. 2018-04-24. https://www.wi-fi.org/file/wi-fi-certified-wpa3
- Advanced Encryption Standard (AES) — National Institute of Standards and Technology (NIST). 2001-11-26 (FIPS 197, remains authoritative). https://nvlpubs.nist.gov/nistpubs/FIPS/NIST.FIPS.197.pdf
- KRACK Attacks: Breaking WPA2 — Mathy Vanhoef (Academic paper). 2017-10-16. https://papers.mathyvanhoef.com/usenixsecurity2017.pdf
- Wi-Fi Alliance Security Overview — Wi-Fi Alliance. 2023-09-12. https://www.wi-fi.org/security