
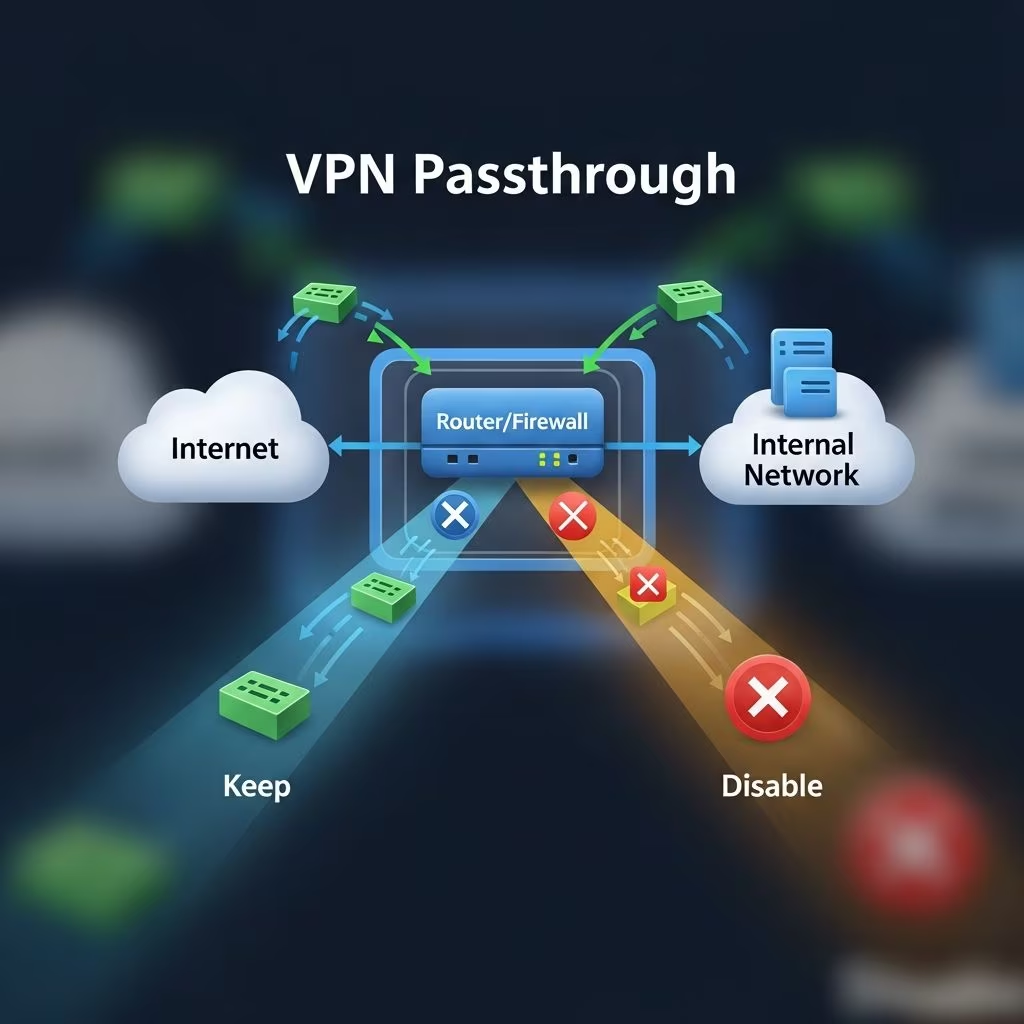
VPN passthrough is a common router feature that many users overlook, yet it plays a pivotal role in how virtual private networks function within home and small office environments. At its core, this capability allows VPN traffic to traverse network address translation (NAT) firewalls without interruption. Routers equipped with NAT typically rewrite packet headers to manage multiple devices sharing a single public IP address. However, certain VPN protocols struggle with this process, leading to connection failures. VPN passthrough addresses this by implementing protocol-specific rules that preserve the integrity of VPN packets, ensuring they reach their destination intact.
In today’s connected world, where remote work and secure data access are norms, understanding this feature is essential. Disabling it can fortify your network defenses, but it might disrupt legitimate VPN usage. This article delves into the intricacies of VPN passthrough, provides actionable guidance on toggling it off, and evaluates the trade-offs involved. Whether you’re a network administrator tightening security or a home user troubleshooting connectivity, these insights will empower informed decisions.
Understanding the Fundamentals of VPN Passthrough
To grasp why VPN passthrough exists, consider the evolution of networking. Traditional VPNs like Point-to-Point Tunneling Protocol (PPTP), Layer 2 Tunneling Protocol (L2TP), and Internet Protocol Security (IPsec) were designed before widespread NAT adoption. These protocols embed authentication and encryption details in packet headers that NAT alters, causing mismatches and dropped connections.
VPN passthrough mitigates this through specialized handling:
- Protocol Detection: The router identifies VPN-related packets based on signatures or ports.
- State Tracking: It maintains session states to differentiate VPN traffic from standard internet flows.
- NAT Exemption: Specific protocols bypass full NAT rewriting, allowing end-to-end communication.
For IPsec, which is prevalent in enterprise settings, passthrough handles UDP ports 500 (IKE for key exchange) and 4500 (NAT-T for traversal). L2TP uses UDP 1701, while PPTP relies on GRE protocol 47 alongside TCP 1723. Without passthrough, firewalls treat these as suspicious, blocking them outright.
Modern routers from brands like Cisco, Netgear, and TP-Link include this feature by default, often under ‘Advanced’ or ‘Security’ menus. It’s particularly vital in SOHO setups where the gateway isn’t the VPN endpoint but merely a conduit.
Step-by-Step Guide: Disabling VPN Passthrough on Common Routers
Disabling VPN passthrough varies by manufacturer, but the process generally involves accessing the web interface. Always back up your configuration first to revert changes easily. Here’s how to do it on popular models:
Netgear Routers
- Log in to the router at
192.168.1.1using admin credentials. - Navigate to Advanced > Advanced Setup > VPN Service.
- Locate passthrough toggles for IPsec, PPTP, and L2TP.
- Set each to Disable and click Apply.
- Reboot the device to enforce changes.
TP-Link Routers
- Access the interface via
tplinkwifi.net. - Go to Advanced > NAT Forwarding > VPN Passthrough.
- Uncheck boxes for PPTP, L2TP/IPsec, and IPsec passthrough.
- Save and allow 1-2 minutes for propagation.
Cisco/Linksys Routers
- Enter the admin panel at
192.168.1.1. - Select Security > VPN Passthrough.
- Disable options individually and hit Save Settings.
Pro Tip: After disabling, test internal devices’ internet access and attempt a VPN connection to verify blocking. Use tools like Wireshark for packet inspection if issues arise.
| Router Brand | Menu Path | Key Options to Disable |
|---|---|---|
| Netgear | Advanced > VPN Service | IPsec, PPTP, L2TP |
| TP-Link | Advanced > VPN Passthrough | All passthrough types |
| Cisco/Linksys | Security > VPN Passthrough | Per-protocol toggles |
| Asus | WAN > NAT Passthrough | IPsec, PPTP |
Advantages of Turning Off VPN Passthrough
Security is the primary driver for disabling this feature. Open ports for VPN protocols represent potential entry points for exploits. By closing them:
- Reduced Attack Surface: Blocks unauthorized scans targeting UDP 500/4500, common in automated attacks.
- Firewall Integrity: Restores strict stateful inspection, dropping unsolicited inbound traffic.
- Compliance Alignment: Aids adherence to standards like NIST SP 800-41 for boundary protection.
- Performance Boost: Eliminates overhead from protocol detection and state tracking.
In high-security environments, such as those handling sensitive data, this measure prevents lateral movement by threat actors leveraging VPN tunnels.
Potential Drawbacks and When to Reconsider
While security benefits are clear, disabling passthrough isn’t universally advisable. Key downsides include:
- VPN Connectivity Loss: Devices behind the router can’t establish tunnels using legacy protocols.
- Remote Work Disruption: Employees relying on corporate IPsec VPNs face outages.
- Legacy System Incompatibility:
Older software or institutional networks still dependent on PPTP/L2TP.
Quantitatively, a 2023 Cisco Annual Cybersecurity Report notes that 20% of breaches involved VPN misconfigurations, underscoring the double-edged nature of these features. Weigh your usage: if no internal VPN needs exist, disable confidently.
Alternatives to Traditional VPN Passthrough
For those needing VPN without passthrough vulnerabilities, consider modern solutions:
- WireGuard/OpenVPN: These protocols use UDP/TCP ports (e.g., 1194) that NAT handles natively, bypassing passthrough.
- Zero Trust Network Access (ZTNA): Cloud-based, agentless access eliminates port dependencies.
- SD-WAN with Built-in VPN: Enterprise-grade overlays manage traffic securely.
Transitioning reduces reliance on outdated mechanisms. For instance, ExpressVPN’s Lightway protocol exemplifies passthrough-free efficiency.
Best Practices for Secure Router Management
Beyond passthrough, holistic security involves:
- Regular firmware updates to patch known vulnerabilities.
- Strong, unique admin passwords with 2FA where possible.
- Disable UPnP and WPS to prevent unauthorized port openings.
- Segment networks using VLANs for IoT vs. critical devices.
- Monitor logs for anomalous VPN attempts.
Implement intrusion detection via tools like Snort for proactive threat hunting.
Common Myths and Misconceptions Debunked
Myth 1: Disabling passthrough breaks all VPNs. Reality: Only legacy ones; modern protocols thrive.
Myth 2: It’s always enabled and risky. Reality: Defaults vary; audit your setup.
Myth 3: No performance impact. Reality: It adds minor CPU load on busy networks.
Frequently Asked Questions (FAQ)
What happens if I disable VPN passthrough?
Your router will block protocols needing it, preventing VPN setups from internal devices while boosting security.
Is IPsec passthrough safe to disable?
Yes, if your VPN uses alternatives like OpenVPN. Test thoroughly post-change.
Why do modern VPNs not require passthrough?
They employ NAT-friendly designs, encapsulating traffic in standard UDP/TCP without header conflicts.
Can disabling it improve internet speed?
Marginally, by reducing processing overhead, though gains are typically under 5%.
How do I know if passthrough is active?
Check router status pages or attempt a legacy VPN connection; failures indicate it’s off or unneeded.
References
- Cisco Annual Cybersecurity Report — Cisco Systems. 2023-06-28. https://www.cisco.com/c/en/us/products/security/security-reports.html
- NIST Special Publication 800-41 Revision 1: Guidelines on Firewalls and Firewall Policy — National Institute of Standards and Technology. 2020-01-31. https://nvlpubs.nist.gov/nistpubs/SpecialPublications/NIST.SP.800-41r1.pdf
- IPsec Configuration Guide — Cisco. 2024-03-15. https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/sec_conn_ikevpn/configuration/xe-16/sec-ikevpn-xe-16-book/sec-cfg-vpn-ipsec.html
- RFC 3948: UDP Encapsulation of IPsec ESP Packets — Internet Engineering Task Force. 2004-12. https://datatracker.ietf.org/doc/html/rfc3948