
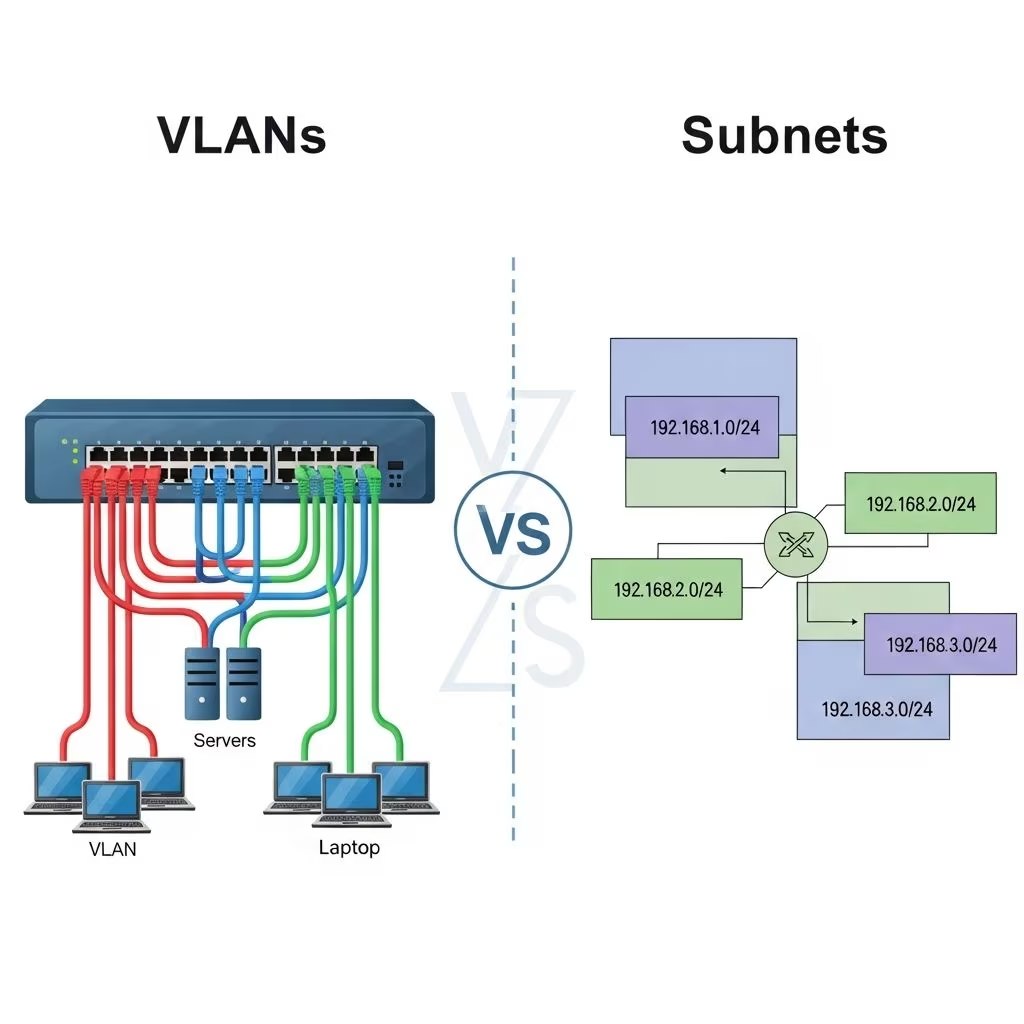
In the realm of network management, dividing large infrastructures into manageable segments is essential for performance, security, and scalability. Two primary techniques dominate this space: Virtual Local Area Networks (VLANs) and IP subnetting. While both aim to isolate traffic and organize devices, they operate at different layers of the OSI model and offer distinct benefits. This article delves into their mechanics, comparisons, and practical applications to help network professionals make informed decisions.
Understanding the Foundations of Network Segmentation
Network segmentation breaks down monolithic networks into smaller, controlled units. This practice minimizes congestion, enhances security by limiting access, and simplifies troubleshooting. Before exploring VLANs and subnets specifically, consider the broader context.
Historically, physical separation—using dedicated switches or wiring—achieved segmentation. However, this approach is costly and inflexible for dynamic environments like offices, data centers, or campuses. Modern solutions leverage logical divisions, allowing a single physical infrastructure to host multiple isolated groups.
- Benefits of Segmentation: Reduced broadcast domains, better bandwidth allocation, and policy enforcement.
- Challenges: Ensuring inter-segment communication without compromising isolation.
With this foundation, VLANs and subnets emerge as complementary yet distinct tools.
What Are VLANs and How Do They Function?
A VLAN creates virtual networks over physical hardware, primarily through switch configurations. Defined by the IEEE 802.1Q standard, VLANs insert a tag into Ethernet frames, identifying them to a specific virtual group. This tag, a 12-bit identifier (VID), supports up to 4094 unique VLANs.
Devices in the same VLAN communicate as if on a dedicated switch, regardless of physical connections. Ports on managed switches are assigned to VLANs: access ports for end devices and trunk ports for inter-switch links carrying multiple VLAN traffic.
| VLAN Type | Description | Use Case |
|---|---|---|
| Access VLAN | Untagged traffic for endpoints | Workstations, printers |
| Trunk VLAN | Tagged traffic across switches | Backbone connections |
| Native VLAN | Untagged on trunks | Default management traffic |
VLANs excel in environments requiring flexible grouping, such as departmental separations in enterprises.
Demystifying IP Subnets
IP subnetting partitions networks using IP addresses and subnet masks. At OSI Layer 3, it divides a large address space (e.g., 10.0.0.0/8) into smaller ranges (e.g., 10.1.0.0/16, 10.2.0.0/16). Routers forward traffic between subnets based on these addresses.
Subnetting optimizes IP utilization, especially with IPv4 scarcity. Classless Inter-Domain Routing (CIDR) notation like /24 defines subnet size, controlling host count per segment.
- Key Features: Hierarchical addressing, broadcast domain limitation via routers.
- Limitations: Relies on Layer 3 routing, potentially introducing latency.
For example, a /24 subnet supports 254 hosts, ideal for small teams, while larger masks suit expansive networks.
Core Differences: Layer 2 vs Layer 3 Realms
The fundamental divergence lies in operational layers. VLANs function at Data Link (Layer 2), using MAC addresses and switch logic. Subnets reside at Network (Layer 3), leveraging IP addresses and routing tables.
| Aspect | VLAN | Subnet |
|---|---|---|
| OSI Layer | Layer 2 | Layer 3 |
| Identification | VLAN ID (1-4094) | IP Address + Mask |
| Configuration | Switch ports | Device IP settings |
| Scope | Broadcast domain | IP network segment |
| Inter-Communication | L3 device required | Router/switch |
Even on the same switch without VLANs, different-subnet devices share a broadcast domain, exposing traffic. VLANs enforce isolation at the frame level.
Why Choose VLANs? Unmatched Security Advantages
Security is a compelling reason to prefer VLANs. By segmenting at Layer 2, switches drop frames not destined for the local VLAN, preventing eavesdropping. Subnet-only setups allow promiscuous sniffing on shared backplanes.
Consider a corporate scenario: Finance on VLAN 10, HR on VLAN 20. Without VLANs, a compromised HR device could sniff finance broadcasts. VLANs block this inherently.
Additionally, VLANs support private VLANs (PVLANs), isolating ports within a VLAN for host-level security.
VLANs provide "highway lanes" analogy: each VLAN is a dedicated path, minimizing collision risks.
Performance Gains with VLANs
Broadcast storms plague flat networks. VLANs shrink broadcast domains, confining storms to segments. Subnets reduce them too but require routing overhead.
In high-traffic setups, VLANs offload Layer 2 switching, faster than Layer 3 routing. Modern switches with VLAN support achieve wire-speed performance.
- Bandwidth Efficiency: Dedicated collision domains per VLAN.
- Scalability: Add segments without new hardware.
Practical Implementation Strategies
Deploying VLANs starts with assessment: map logical groups (e.g., VoIP VLAN 100, Data VLAN 200). Configure switches via CLI or GUI:
vlan 100name VOIPinterface range gi0/1-10switchport mode accessswitchport access vlan 100Pair with subnets: VLAN 100 gets 192.168.100.0/24. Use DHCP scopes per VLAN. For inter-VLAN routing, employ Layer 3 switches or routers with subinterfaces.
Best practices include:
- Reserve VLAN 1 for management.
- Enable trunk port security (e.g., allowed VLAN lists).
- Monitor with SNMP tools.
Combining VLANs and Subnets for Optimal Networks
One-to-one mapping—each VLAN to a subnet—is standard. This hybrid leverages Layer 2 isolation and Layer 3 routing. Firewalls at Layer 3 boundaries enforce policies.
In home labs or enterprises, firewalls like pfSense link VLANs to subnets, controlling traffic flows. This setup supports zero-trust models.
Common Pitfalls and Troubleshooting
Misconfigurations cause issues:
- VLAN Mismatch: Trunk ports not allowing required VLANs.
- Native VLAN Discrepancy: Leads to dropped traffic.
- Spanning Tree: Per-VLAN STP (PVST) prevents loops.
Use show vlan brief and show interfaces trunk for diagnostics.
Future-Proofing with VLANs in SDN Era
Software-Defined Networking (SDN) builds on VLANs, enabling dynamic segmentation via controllers like Cisco ACI. VLANs remain foundational for overlay networks (VXLAN).
Frequently Asked Questions
Can VLANs span multiple switches?
Yes, via 802.1Q trunks, allowing seamless extension.
Do subnets require VLANs?
No, but without VLANs, Layer 2 security is compromised.
What’s the max VLANs per switch?
Typically 1000+, depending on hardware.
How do VLANs impact wireless?
SSIDs map to VLANs for guest isolation.
Are VLANs IPv6 compatible?
Fully, as they operate below IP layers.
References
- IEEE Standard for Local and Metropolitan Area Networks — Bridge and Virtual Bridged Local Area Networks — IEEE. 2014 (authoritative standard). https://standards.ieee.org/ieee/802.1Q/5964/
- Difference Between VLAN and Subnet — GeeksforGeeks. 2023-10-15. https://www.geeksforgeeks.org/computer-networks/difference-between-vlan-and-subnet/
- The Difference Between VLANs and Subnets — Biamp Systems. 2015-09-10 (relevant for core concepts). https://www.biamp.com/company/blog/details/biamp-blog/2015/09/10/the-difference-between-vlans-and-subnets
- VLANs versus IP subnets: Why use a VLAN over IP subnetting? — TechTarget. 2023. https://www.techtarget.com/searchnetworking/answer/VLANs-versus-IP-subnets-Why-use-a-VLAN-over-IP-subnetting