
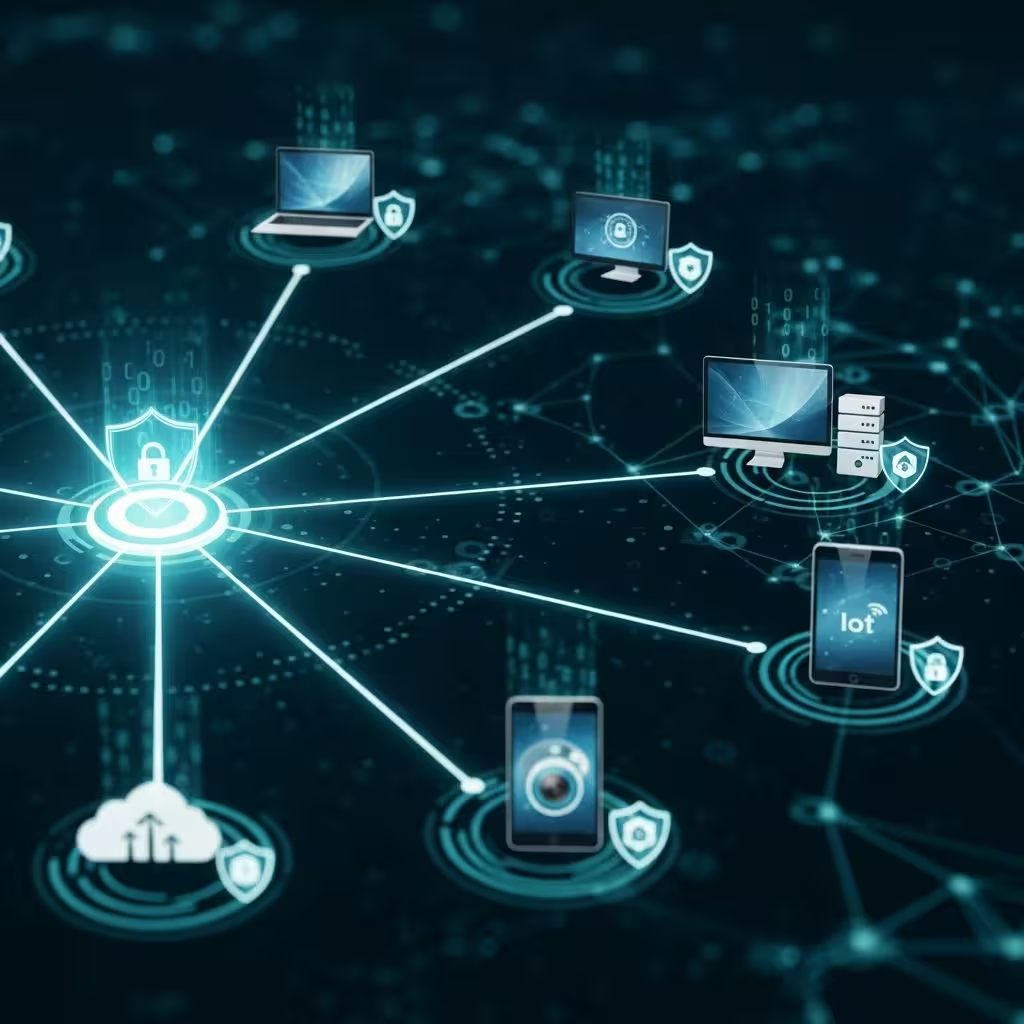
In today’s digitally connected workplace, organizations operate across an increasingly fragmented technology landscape. Employees work from home, coffee shops, and corporate offices using various devices—laptops, smartphones, tablets, and specialized hardware. Each of these devices represents a potential vulnerability in the corporate network architecture. This article explores the concept of endpoints in cybersecurity, their significance as attack vectors, and the comprehensive strategies organizations employ to safeguard them against sophisticated threats.
Defining Endpoints in a Security Context
An endpoint, in cybersecurity terminology, refers to any device that connects to an organization’s network infrastructure and accesses corporate resources or data. These connection points serve as gateways between the external world and an organization’s internal systems. Unlike the traditional perimeter-based security model where all devices resided within a physical office, modern endpoints exist everywhere employees work—creating a fundamentally different security challenge.
Common endpoint categories include:
- Desktop computers and workstations
- Laptop and portable computing devices
- Smartphones and tablets running iOS, Android, or other operating systems
- Servers that process and store organizational data
- Internet of Things (IoT) devices and specialized hardware
- Medical devices in healthcare organizations
- Point-of-sale terminals in retail environments
Each device type presents unique security considerations. A laptop operating system differs significantly from mobile device architecture, requiring tailored protection strategies. This diversity in endpoint technology landscape means security professionals must implement solutions capable of addressing multiple platforms simultaneously.
Why Endpoints Have Become Primary Attack Targets
Cybercriminals increasingly focus their efforts on endpoint devices rather than attempting direct attacks against enterprise infrastructure. This strategic shift reflects a fundamental change in threat landscape dynamics. Research from major cybersecurity firms indicates that endpoints serve as the initial entry point in a significant majority of security incidents affecting organizations worldwide.
The reasons endpoints attract malicious actors are straightforward. First, endpoint devices often have less sophisticated security measures compared to centralized data centers with dedicated security teams. Second, compromised endpoints provide attackers with legitimate credentials and network access, enabling them to move laterally throughout the organization. Third, endpoint users frequently lack sufficient cybersecurity training, making them susceptible to social engineering attacks and deceptive phishing campaigns.
Consider a practical example: an employee receives an email appearing to come from their IT department requesting password verification. Upon clicking the embedded link, the employee unknowingly downloads malware. That single device—one endpoint—becomes a launching point for accessing sensitive company information, intellectual property, and customer data.
Understanding the Attack Surface Expansion
The traditional corporate network operated within defined physical boundaries. All employees worked in offices with consistent security monitoring and control. Today’s distributed workforce has expanded the attack surface dramatically. Remote employees accessing corporate systems from home networks, traveling professionals using airport WiFi, and employees using personal devices on corporate networks all introduce potential vulnerabilities.
Cloud adoption has further complicated endpoint security. Applications and data increasingly reside in cloud environments rather than on-premises servers. This means endpoints must securely communicate with cloud services, authenticate access requests, and protect data in transit. Organizations can no longer assume that network traffic stays within their physical facilities.
The expansion of acceptable device types has also increased complexity. Bring-Your-Own-Device (BYOD) programs allow employees to use personal smartphones and tablets for work. While this offers flexibility and productivity benefits, it introduces devices outside the organization’s direct control into the security perimeter. These personal devices may have outdated operating systems, lack security patches, and run unauthorized applications.
Core Components of Endpoint Protection Strategies
Comprehensive endpoint security extends beyond basic antivirus software. Modern protective approaches integrate multiple complementary technologies and practices working in concert.
Prevention and Detection Capabilities
Organizations implement layered prevention mechanisms to stop threats before they compromise endpoints. These include:
- Next-Generation Antivirus (NGAV): Moving beyond signature-based detection of known threats, NGAV employs behavioral analytics and machine learning to identify suspicious patterns and activities, including zero-day exploits previously unseen in the wild.
- Firewall Protection: Host-based firewalls establish rules governing network traffic flowing to and from individual endpoints, preventing unauthorized connections and limiting lateral movement.
- Intrusion Prevention Systems: These monitor network traffic for known attack patterns and block malicious communications before they reach the endpoint.
- Data Loss Prevention (DLP): DLP technologies identify and block transmission of sensitive information, preventing accidental or intentional data exfiltration.
Detection capabilities operate continuously, monitoring endpoint behavior and analyzing patterns for anomalies. Machine learning algorithms learn what constitutes normal activity for specific users and systems, then alert security teams when deviations occur.
Encryption and Access Control
Encryption protects data both at rest and in transit. Disk encryption ensures that if a device is lost or stolen, the data stored on it remains inaccessible without proper authentication credentials. Encryption in transit protects data as it travels across networks to cloud services and corporate systems.
Access control mechanisms verify that only authorized users can access specific resources and data. Multi-factor authentication adds layers of verification beyond simple passwords, requiring additional proof of identity before granting access to sensitive systems.
Patch Management and Vulnerability Scanning
Software vulnerabilities represent one of the primary attack vectors exploited by threat actors. Operating systems, applications, and drivers require continuous updates addressing newly discovered security flaws. Automated patch management systems ensure that security updates deploy across the entire endpoint fleet without requiring manual intervention on individual devices.
Vulnerability scanning identifies unpatched systems, outdated software versions, and misconfigurations that create security exposures. Regular scans establish a baseline of organizational security posture and highlight areas requiring immediate remediation.
Centralized Management and Visibility
Organizations with hundreds or thousands of endpoints require centralized management platforms providing comprehensive visibility into device status, security configurations, and threat incidents. These platforms enable administrators to:
- Deploy security policies consistently across all endpoints
- Monitor policy compliance and identify non-compliant devices
- Receive real-time alerts when threats are detected
- Investigate security incidents across multiple devices simultaneously
- Generate reports for compliance and audit purposes
Advanced Response Capabilities
When threats successfully penetrate prevention mechanisms, rapid response becomes critical. Endpoint Detection and Response (EDR) platforms enable security teams to investigate active threats, determine scope of compromise, and implement containment measures.
EDR solutions collect detailed telemetry from endpoints including process execution history, file modification events, network connections, and user activities. This comprehensive data enables forensic investigation to understand how an attack occurred, what systems were affected, and what data may have been accessed.
Automated response capabilities can immediately disconnect compromised endpoints from the network, terminate malicious processes, quarantine suspicious files, and block network connections to known malicious destinations. These automated actions contain damage while security teams conduct thorough investigation and remediation.
Implementing Zero Trust Architecture at the Endpoint
Traditional security models trusted devices once they connected to the corporate network. Zero Trust architecture rejects this assumption, requiring continuous verification of device security posture regardless of whether the endpoint is on-premises or remote.
Zero Trust implementation at the endpoint layer involves:
- Continuous verification of device health before granting network access
- Assessment of patch levels and security configuration status
- Verification of encryption status and enabled security features
- Isolation of non-compliant devices until remediation occurs
- Real-time monitoring of user and device behavior for anomalies
- Limiting lateral movement even after initial compromise
This approach transforms endpoint security from a static point-in-time assessment to a dynamic, continuous evaluation ensuring that only healthy devices with appropriate security controls maintain network access.
Addressing Specific Endpoint Categories
Different endpoint types require specialized protection strategies reflecting their unique characteristics and use cases.
Mobile Devices in Enterprise Environments
Smartphones and tablets operate on different operating systems and architectures than traditional computers. Mobile device management (MDM) solutions establish security policies for mobile endpoints, including:
- Enforcing passcode requirements and biometric authentication
- Enabling remote device wipe capabilities in case of loss or theft
- Restricting installation of unauthorized applications
- Monitoring compliance with security policies
- Isolating corporate data from personal data on shared devices
Remote Workers and Hybrid Environments
Employees working remotely or in hybrid arrangements connect from personal networks lacking sophisticated security controls. Organizations address this by:
- Requiring VPN connections for all remote access
- Implementing multi-factor authentication for remote system access
- Deploying endpoint security agents on remote devices
- Monitoring remote endpoint behavior for suspicious activities
- Ensuring home network security requirements align with organizational standards
Internet of Things and Specialized Devices
IoT devices and specialized hardware often run proprietary operating systems with minimal security features. Organizations managing these devices implement:
- Network segmentation isolating IoT devices from sensitive systems
- Monitoring for unauthorized firmware modifications
- Restricting network access to known trusted devices
- Regular security audits of device configuration
Endpoint Security in Cloud and Hybrid Infrastructure
As organizations adopt cloud services and hybrid infrastructure, endpoint security strategies must extend to virtual machines and cloud-based workloads. Cloud-based endpoint protection solutions provide:
- Consistent security policy enforcement across on-premises and cloud environments
- Real-time threat intelligence updated without requiring manual administrator intervention
- Automated threat response across heterogeneous infrastructure
- Simplified management through centralized consoles
- Scalability to support growing numbers of endpoints
Measuring Endpoint Security Effectiveness
Organizations must continuously evaluate whether their endpoint security investments effectively reduce risk. Key performance indicators include:
- Mean Time to Detection (MTTD): How quickly the organization identifies security incidents
- Mean Time to Response (MTTR): How rapidly security teams contain and remediate incidents
- Policy Compliance Rate: Percentage of endpoints maintaining required security configurations
- Patch Management Coverage: Percentage of endpoints current with security updates
- False Positive Ratio: Balance between detecting genuine threats and generating noise
Future Considerations for Endpoint Security
The endpoint security landscape continues evolving as threats become more sophisticated and technology landscapes become more complex. Emerging considerations include:
- Artificial intelligence and machine learning enabling more sophisticated threat detection
- Integration of security signals from multiple sources for comprehensive visibility
- Increased focus on insider threat detection and prevention
- Adaptation to new device types and emerging technologies
- Privacy-conscious security approaches balancing protection with employee privacy
References
- What Is Endpoint Security? — Palo Alto Networks. https://www.paloaltonetworks.com/cyberpedia/what-is-endpoint-security
- What Is Endpoint Security? — CrowdStrike. https://www.crowdstrike.com/en-us/cybersecurity-101/endpoint-security/
- What Is Endpoint Security? — Cisco. https://www.cisco.com/site/us/en/learn/topics/security/what-is-endpoint-security.html
- What Is Endpoint Security? How It Works & Its Importance — Trellix. https://www.trellix.com/security-awareness/endpoint/what-is-endpoint-security/
- What Is Endpoint Security? — Sophos. https://www.sophos.com/en-us/cybersecurity-explained/what-is-endpoint-security
- What Is Endpoint Security? — Proofpoint. https://www.proofpoint.com/us/threat-reference/endpoint-security
- What Is Endpoint Security? — IBM. https://www.ibm.com/think/topics/endpoint-security