
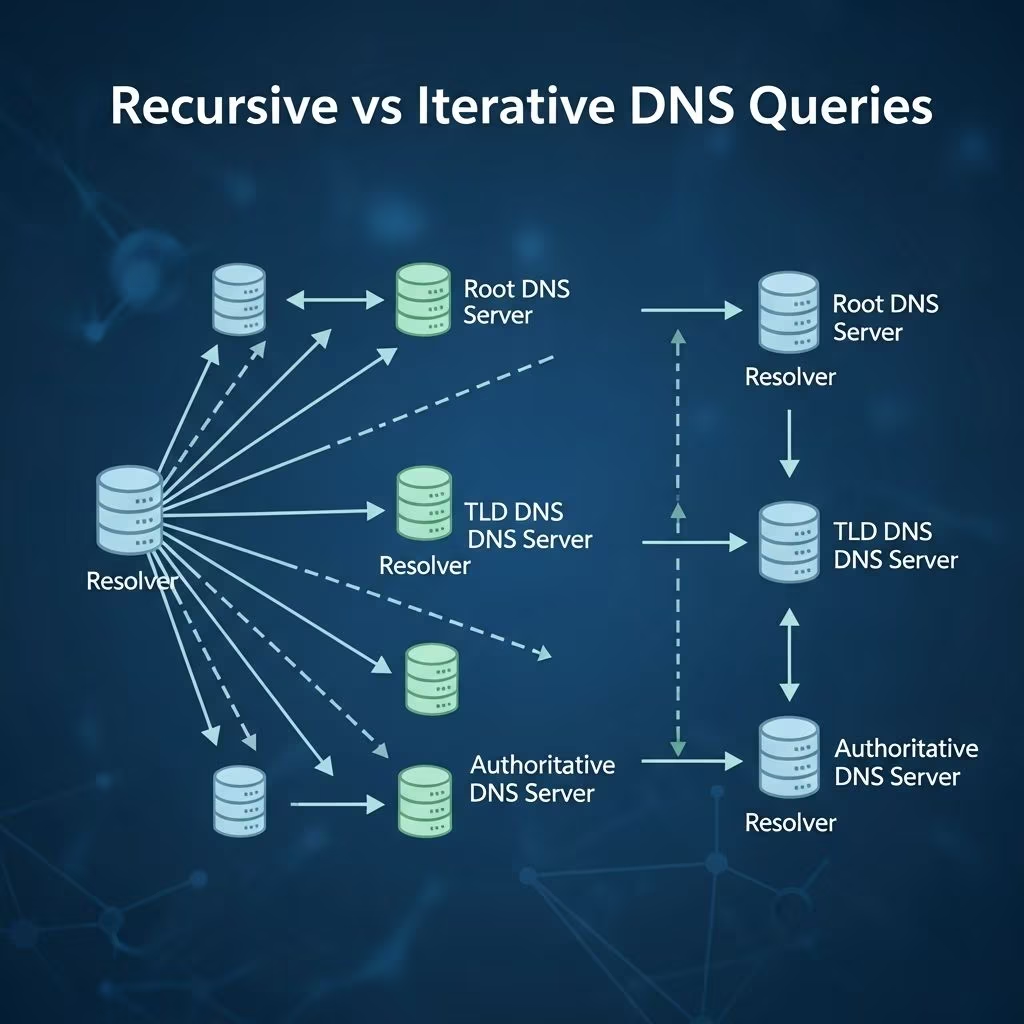
The Domain Name System (DNS) is the invisible force that transforms human-readable domain names like ‘example.com’ into machine-readable IP addresses. At its heart lie two fundamental query types: recursive and iterative. These mechanisms ensure seamless connectivity across the internet’s vast hierarchy of servers. Understanding their distinctions is crucial for network engineers, system administrators, and anyone optimizing digital infrastructure. This article delves into their operations, contrasts, real-world applications, and performance considerations.
The Fundamentals of DNS Resolution
DNS operates as a distributed database, organized in a tree-like structure from root servers down to authoritative name servers for specific domains. When a device needs to resolve a hostname, it initiates a query that travels this hierarchy. Recursive queries delegate the full resolution burden to a single server, while iterative queries involve step-by-step referrals across multiple servers.
Root servers, managed by organizations like Verisign and the Internet Assigned Numbers Authority (IANA), sit at the top. They direct queries to top-level domain (TLD) servers (.com, .org), which then point to authoritative servers holding the actual records. This layered approach prevents any single point of overload, distributing queries efficiently worldwide.
How Recursive DNS Queries Function
A recursive query is like hiring a personal investigator: you provide the case details, and they handle every lead until delivering the final report. Clients—such as your laptop or smartphone—send recursive queries to a designated DNS resolver, often the ISP’s server or public ones like 8.8.8.8 (Google Public DNS).
- Client Submission: The device asks, “What’s the IP for www.example.com?”
- Resolver Check: The resolver first scans its cache for a recent match.
- Full Resolution: If absent, the resolver embarks on its own quest, querying upstream servers until it secures the definitive IP address.
- Response Delivery: The resolver caches the answer (typically for a TTL-defined period) and returns it to the client.
This model shields end-users from complexity, ideal for consumer devices with limited resources. However, it demands robust resolvers capable of managing high volumes without faltering.
Decoding Iterative DNS Queries
Iterative queries resemble a treasure hunt where each clue leads to the next map. Here, the querying entity—usually a resolver—polls servers one by one, accepting partial responses or referrals rather than demanding finality.
- Initial Poll: Resolver queries a root server: “Where can I find www.example.com?”
- Root Referral: Root responds: “Try the .com TLD server at this address.”
- TLD Follow-Up: Resolver queries TLD: “Know www.example.com?” TLD replies: “Check example.com’s authoritative server.”
- Authoritative Answer: Final server provides the IP, completing the chain.
Iterative processes empower resolvers to traverse the DNS tree autonomously, minimizing client involvement post-initial request. They’re the workhorses behind recursive fulfillment.
Core Distinctions: A Side-by-Side Analysis
While both serve name resolution, their philosophies diverge sharply. The table below highlights pivotal contrasts:
| Aspect | Recursive Query | Iterative Query |
|---|---|---|
| Responsibility | Resolver bears full load | Querier follows referrals |
| Response Type | Complete IP or error | Answer, referral, or NXDOMAIN |
| Client Role | Minimal—one query | Potentially multiple if not resolver |
| Typical Path | Client → Resolver | Resolver → Root → TLD → Authoritative |
| Caching Impact | Heavy reliance on resolver cache | Opportunistic across hierarchy |
These differences dictate deployment: recursive for simplicity, iterative for precision in backbone operations.
Real-World Scenarios and Walkthroughs
Imagine browsing ‘www.bank.com’ from home. Your browser triggers a recursive query to your ISP’s resolver. Unbeknownst to you, that resolver unleashes iterative queries:
- Root: Directs to .com TLD.
- TLD: Points to bank.com nameservers.
- Authoritative: Delivers 192.0.2.1.
Resolver caches this, serving future requests instantly. In enterprise settings, internal resolvers might handle recursive queries for intranet sites, using iterative for external ones to avoid leaks.
Contrast with a stub resolver on an IoT device: it sticks to recursive queries for efficiency, never engaging iteratively directly.
Performance Ramifications and Optimization Tactics
Recursive queries excel in user experience—single request, fast perceived speed—but strain resolvers during cache misses, potentially causing latency spikes. Iterative queries distribute load but introduce cumulative delays from multiple round-trips.
Key optimizations:
- Caching Layers: Implement forwarders and negative caching to slash upstream queries.
- Anycast Routing: Route to nearest resolver instance globally.
- DNSSEC Validation: Balance security without recursive overhead.
- Rate Limiting: Prevent abuse on recursive endpoints.
Studies from ICANN highlight how effective caching cuts global query volume by 80-90%.
Advanced Use Cases and Edge Situations
Beyond basics, iterative shines in zone transfers (AXFR/IXFR) and anycast deployments. Recursive powers DNS-over-HTTPS (DoH) and DNS-over-TLS (DoT) for privacy. Hybrid setups, like forwarding resolvers, blend both: recursive to forwarder, iterative beyond.
Troubleshooting tip: Tools like dig +trace simulate iterative paths, revealing hierarchy issues. For recursive, dig @8.8.8.8 example.com tests public resolvers.
Security Implications in Query Handling
DNS amplifications attacks target recursive resolvers, forging queries to overwhelm victims. Mitigation: Disable open recursion, enforce BGP flowspec. Iterative queries, peer-to-peer in nature, resist such exploits but demand referral validation.
Adopting DoH shifts recursive traffic over HTTPS, evading ISP snooping while preserving performance.
Future Evolutions in DNS Query Paradigms
With 5G and edge computing, recursive resolvers migrate to CDNs for sub-millisecond latency. Protocols like SVCB/HTTPS records enhance iterative efficiency. QUIC-based DNS promises to fuse transport and resolution layers.
Frequently Asked Questions (FAQs)
What happens if a recursive resolver fails mid-query?
It times out, returning SERVFAIL to the client, prompting retries or fallbacks.
Can clients perform iterative queries directly?
Yes, via tools like dig, but OS resolvers default to recursive for simplicity.
How does TTL influence recursive vs iterative?
Both honor TTL for caching; iterative benefits from shared caches in hierarchies.
Are there non-recursive queries besides iterative?
Yes, direct authoritative queries when the resolver knows the zone.
Why prefer public recursive resolvers like 1.1.1.1?
They offer speed, privacy, and global anycast without ISP bottlenecks.
References
- DNS Resolver Best Practices — Cloudflare. 2025-03-15. https://developers.cloudflare.com/1.1.1.1/
- Domain Name System (DNS) Technical Reference — IANA/ICANN. 2024-11-01. https://www.iana.org/domains/root/files
- RFC 1034: Domain Names – Concepts and Facilities — IETF (Mockapetris). 1987-11-01 (authoritative standard). https://datatracker.ietf.org/doc/html/rfc1034
- DNS Privacy Considerations — IETF (RFC 7816). 2016-05-01 (foundational, still relevant). https://datatracker.ietf.org/doc/html/rfc7816