
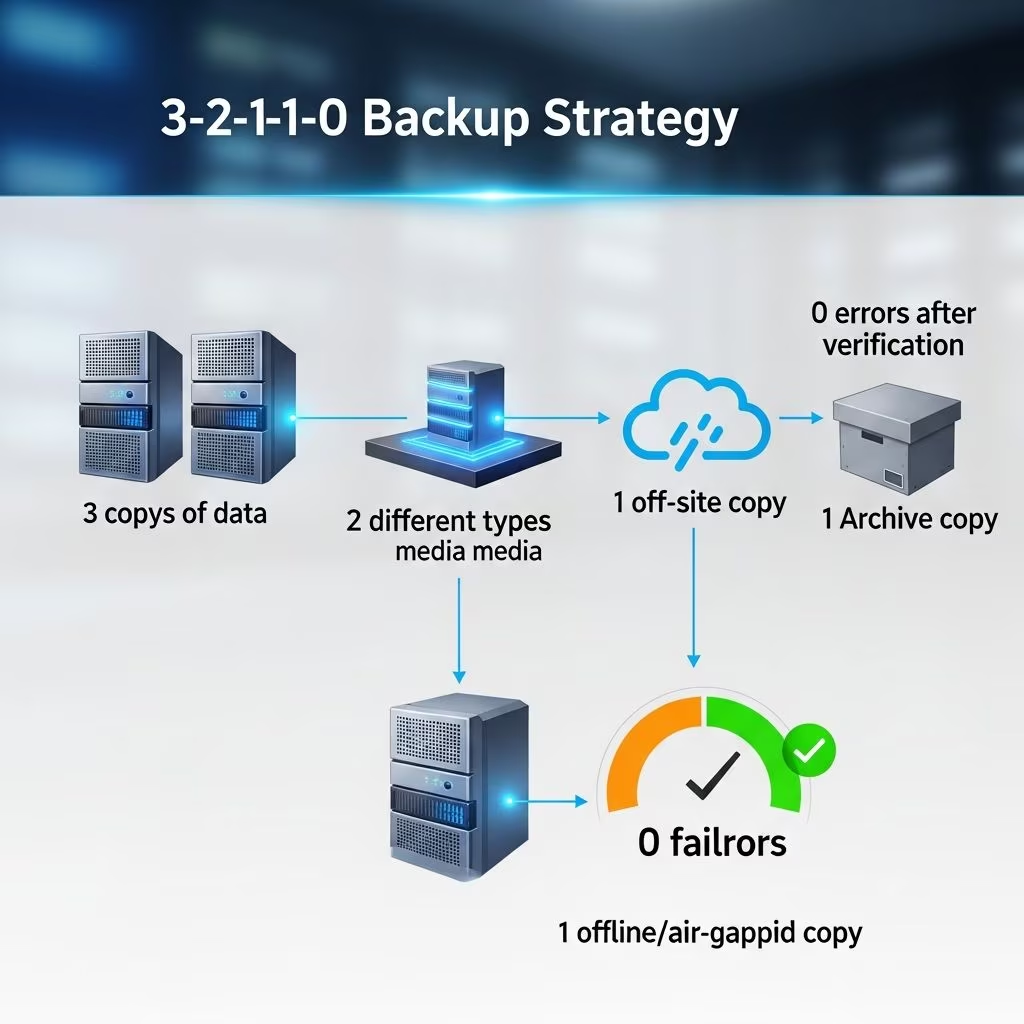
In an era where data is the lifeblood of businesses, losing it to cyber attacks, hardware failures, or natural disasters can spell catastrophe. Traditional backup methods fall short against sophisticated threats like ransomware, which now targets backups themselves. Enter the 3-2-1-1-0 backup strategy—a robust evolution of the classic 3-2-1 rule designed for today’s digital battlefield. This approach ensures multiple layers of redundancy, isolation, and verification, guaranteeing that your data remains recoverable no matter what.
This comprehensive guide breaks down each component of the 3-2-1-1-0 rule, explores its advantages over older methods, and provides actionable steps for implementation. Whether you’re an IT administrator, business owner, or cybersecurity enthusiast, understanding this strategy is essential for safeguarding your organization’s most valuable asset: information.
Understanding the Foundations: From 3-2-1 to 3-2-1-1-0
The original 3-2-1 backup rule emerged decades ago as a simple yet effective guideline: maintain three copies of your data on two different storage media, with one copy stored offsite. It was perfect for an age dominated by physical tapes and local servers, protecting against localized failures like disk crashes or fires.
However, the landscape has shifted dramatically. Cloud adoption, exponential data growth, and rampant ransomware have exposed vulnerabilities in the classic model. Attackers can encrypt or delete cloud-stored backups if they’re connected and mutable. The 3-2-1-1-0 rule builds on its predecessor by adding two critical enhancements: an immutable or air-gapped copy (the extra ‘1’) and a mandate for fully verified, error-free backups (the ‘0’). This makes it a gold standard for modern resilience.
| Rule Component | Description | Benefit |
|---|---|---|
| 3 | Three copies of data (plus original) | Redundancy against single failures |
| 2 | Two different media types | Diversifies risk across technologies |
| 1 | One offsite copy | Protection from site-specific disasters |
| 1 | One immutable/air-gapped copy | Defense against ransomware deletion |
| 0 | Zero recovery errors | Guaranteed restorability through testing |
Breaking Down Each Element of the 3-2-1-1-0 Framework
The ‘3’: Ensuring Multiple Data Copies
At its core, the strategy demands at least three backup copies in addition to your production data. This means if your primary server holds the original, you need backups A, B, and C elsewhere. Why three? A single backup risks corruption or failure during recovery, while two might still falter under simultaneous threats. Three provides statistical assurance—one is likely to survive any incident.
For small businesses, this could mean daily snapshots on local disk, weekly tapes, and monthly cloud archives. Enterprises might scale to petabytes across hybrid environments.
The ‘2’: Diversifying Storage Media
No putting all eggs in one basket. Use at least two media types: say, SSDs for fast local access and magnetic tape or cloud object storage for longevity. Different media have unique failure modes—disks wear out mechanically, tapes degrade slowly but offer air-gapping potential, and cloud services provide geo-redundancy but require encryption.
This diversity thwarts scenarios where a media-specific vulnerability (e.g., a zero-day exploit in HDD firmware) compromises everything.
The First ‘1’: Offsite Protection
Site disasters—floods, earthquakes, or even building fires—necessitate an offsite copy. Cloud providers like AWS S3 or Azure Blob excel here, offering regional replication. Pro tip: Avoid single-provider lock-in by using a secondary cloud for backups, as outages (rare but real) can affect entire regions.
Offsite doesn’t mean inaccessible; use services with low-latency replication for disaster recovery orchestration.
The Second ‘1’: Air-Gapped or Immutable Backups
Ransomware’s favorite trick? Infiltrating network-connected backups. The solution: one copy that’s physically disconnected (air-gapped) or digitally unalterable (immutable). Air-gapping involves tape vaults or USB drives rotated offline. Immutability uses write-once-read-many (WORM) policies, enforced via object locks in clouds or on-premises appliances.
According to Verizon’s 2023 Data Breach Investigations Report, 89% of ransomware targets backups first—making this layer non-negotiable.
The ‘0’: Zero Errors Through Rigorous Testing
Backups are worthless if untested. The ‘0’ mandates regular verification: automated integrity checks, synthetic fulls, and live restore drills. Tools like Veeam SureBackup or custom scripts simulate recoveries in isolated sandboxes, ensuring zero errors before crises hit.
Implement daily checksums, weekly point-in-time restores, and quarterly full drills to build confidence.
Why 3-2-1-1-0 Outshines Traditional Methods
Legacy 3-2-1 works for basic needs but crumbles under modern scrutiny. Without air-gapping, ransomware wipes connected copies. No verification means ‘backup complete’ illusions hide corrupt data. The enhanced rule addresses these with proven defenses.
- Ransomware Resilience: Immutable copies can’t be encrypted or deleted.
- Cost-Effectiveness: Leverages cheap cloud tiers for long-term retention.
- Compliance Alignment: Meets GDPR, HIPAA retention mandates via verified, isolated copies.
- Scalability: Fits SMBs to hyperscalers without vendor lock-in.
Real-world stats underscore urgency: NIST reports average downtime from attacks exceeds 24 days, costing millions.
Implementing 3-2-1-1-0: A Step-by-Step Blueprint
Transitioning isn’t overnight, but methodical planning yields quick wins.
- Assess Needs: Map RPO (recovery point objective, e.g., 1-hour data loss tolerance) and RTO (recovery time, e.g., 4 hours).
- Inventory Assets: Catalog data tiers—critical (daily backups), archival (monthly).
- Select Tools: Choose platforms supporting immutability (e.g., Rubrik, Cohesity) and testing.
- Build Infrastructure: Procure air-gap media; configure cloud WORM buckets.
- Schedule Rotations: Weekly offline swaps; automate verifications.
- Secure Storage: Vaults for tapes; encrypted, geo-diverse clouds.
- Test Relentlessly: Quarterly fire drills; monitor for errors.
- Document & Train: Policies for all staff; audit trails.
For tiered setups:
- Tier 1 (Production): Hourly disk snapshots for RTO <1hr.
- Tier 2 (LT Retention): Weekly cloud archives for compliance.
- Tier 3 (Air-Gapped): Monthly tapes, rotated offsite.
Overcoming Common Challenges
Cost concerns? Tiered storage keeps expenses low—hot data on premium SSD, cold on glacial S3. Complexity? Automation via Ansible or vendor consoles simplifies. Small teams? MSPs offer managed 3-2-1-1-0 services.
Regulatory hurdles? Built-in auditability ensures proof of compliance.
Advanced Variations and Future-Proofing
Beyond basics, consider 4-3-2-1-0 for ultra-critical data or integrate AI-driven anomaly detection. As quantum threats loom, post-quantum encryption bolsters long-term copies. Hybrid multi-cloud setups maximize uptime.
Frequently Asked Questions (FAQs)
What if I can’t afford air-gapped tapes?
Optical media or immutable cloud snapshots suffice; start small with USB rotations.
How often should I test backups?
Daily integrity checks, weekly partial restores, quarterly full simulations.
Does 3-2-1-1-0 work for cloud-only environments?
Yes—use multi-region, immutable buckets across providers.
What’s the cost impact?
Typically 10-20% uplift, offset by averted breach costs (average $4.5M per IBM).
Can open-source tools implement this?
Absolutely: Bacula for backups, ZFS snapshots, restic for immutability.
Conclusion: Secure Your Data Future Today
The 3-2-1-1-0 backup strategy isn’t just best practice—it’s survival imperative in 2026’s threatscape. By embracing three copies, dual media, offsite isolation, air-gapped defense, and flawless verification, organizations fortify against inevitable risks. Start auditing your setup now; resilience compounds over time.
References
- 2023 Data Breach Investigations Report — Verizon. 2023-05-23. https://www.verizon.com/business/resources/reports/dbir/
- Cost of a Data Breach Report 2023 — IBM Security. 2023-07-24. https://www.ibm.com/reports/data-breach
- Digital Identity Guidelines: Authentication and Lifecycle Management — NIST SP 800-63B. 2024-06-04. https://pages.nist.gov/800-63-3/sp800-63b.html
- Backup and Recovery Best Practices — Veeam. 2025-01-15. https://www.veeam.com/blog/321-backup-rule.html
- Cloud Security Guidance — AWS Well-Architected Framework. 2025-03-10. https://docs.aws.amazon.com/wellarchitected/latest/framework/wel-secure.html