
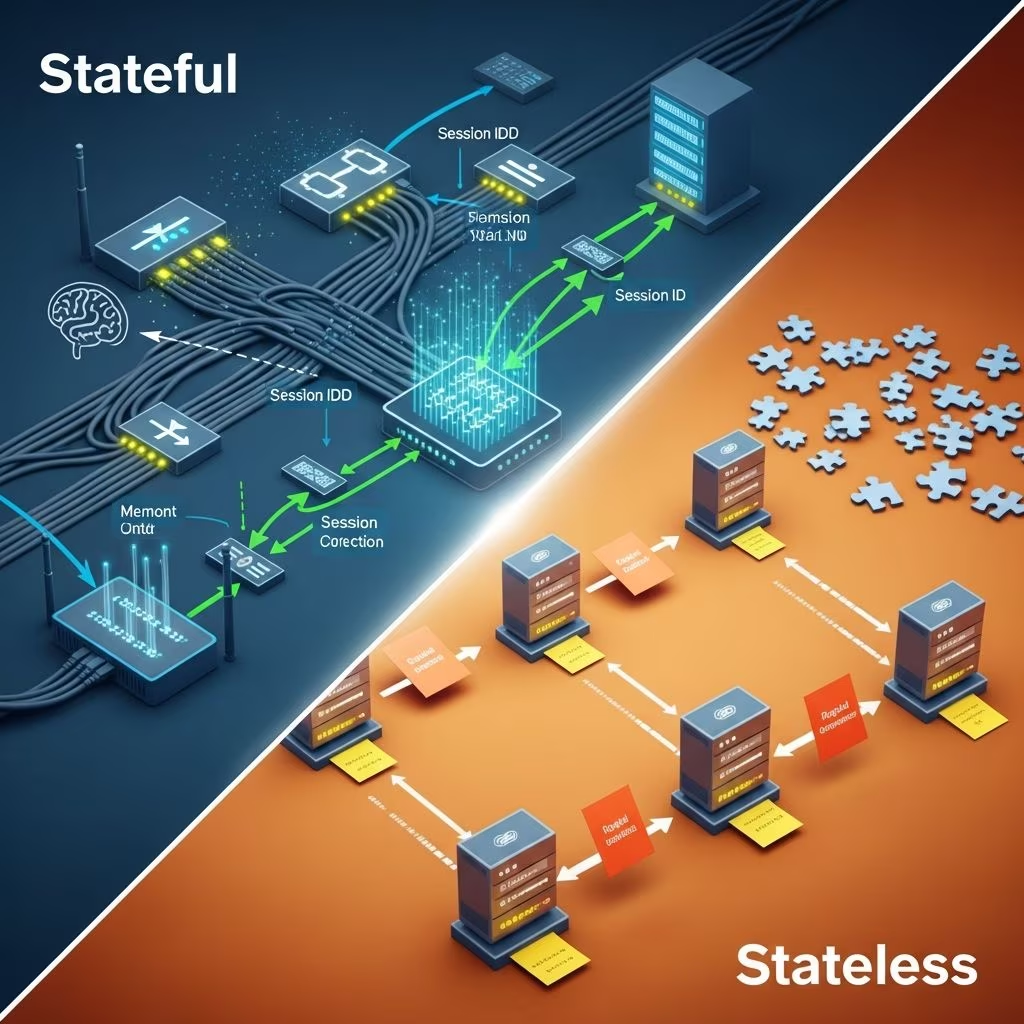
In the realm of computer networking, the distinction between stateful and stateless operations represents a foundational principle that influences everything from security mechanisms to application design. At its essence, this dichotomy revolves around whether a system retains memory of prior interactions or treats each one in isolation. This article delves into the mechanics, advantages, and real-world applications of both approaches, providing network engineers, IT professionals, and developers with actionable insights.
Defining the Fundamentals of State and Statelessness
Stateful networking involves systems that maintain a record—or ‘state’—of ongoing connections or sessions. This memory allows for contextual decision-making based on historical data. Conversely, stateless networking discards all prior information after each transaction, evaluating inputs solely on their standalone merits.
Imagine a stateful system as a vigilant librarian who remembers every book you’ve borrowed and can anticipate your next request based on patterns. A stateless system, however, is like a vending machine: insert coins, select item, receive product—no recollection of previous transactions.
Mechanisms Behind Stateful Network Operations
Stateful systems employ dedicated structures, such as state tables, to track critical details like source/destination addresses, port numbers, sequence numbers, and connection status (e.g., SYN, ACK, FIN). When a new packet arrives, the system cross-references it against this table to validate legitimacy.
- Connection Initiation: A SYN packet starts a new entry in the state table.
- Ongoing Traffic: Matching packets are permitted based on established context.
- Termination: FIN or timeout removes the entry, preventing orphaned states.
This dynamic tracking enables sophisticated behaviors, such as allowing return traffic for outbound requests without explicit inbound rules.
How Stateless Networking Functions
Stateless operations inspect each packet independently using static rulesets. Decisions hinge on header fields like IP addresses, ports, and protocols—no historical context is consulted.
| Aspect | Stateless Inspection |
|---|---|
| Decision Basis | Packet headers only |
| Memory Usage | Minimal (no tables) |
| Speed | High throughput |
| Context Awareness | None |
Traditional Access Control Lists (ACLs) on routers exemplify this: each packet is a fresh evaluation.
Firewalls: The Primary Battlefield of Stateful vs Stateless
Network firewalls epitomize this debate. Early ‘stateless’ firewalls, akin to basic packet filters, offered blunt protection by checking individual packets against rules.
Modern stateful firewalls, operating at OSI Layers 3-4 (and sometimes higher), revolutionized security. They monitor entire connection lifecycles, blocking unsolicited inbound packets while permitting legitimate responses. This ‘implicit allow for established connections’ drastically simplifies rule management.
Stateful inspection, pioneered in the 1990s, marked a paradigm shift from rudimentary filtering to intelligent, context-driven defense.RFC 793 (TCP Specification)
Performance and Resource Trade-offs
Stateless firewalls excel in high-velocity environments, boasting lower latency and CPU overhead. Without state tables, they scale effortlessly across massive traffic volumes—ideal for core routers handling terabits per second.
Stateful firewalls, while resource-intensive, deliver superior security. State table bloat during DDoS attacks poses risks, but hardware acceleration (ASICs, TCAM) mitigates this in enterprise gear.
- Stateless Pros: Speed, simplicity, low resource footprint.
- Stateful Pros: Granular control, reduced attack surface.
Protocols Through a Stateful Lens
Networking protocols themselves embody these traits:
- Stateful Protocols:
- TCP: Three-way handshake establishes state; sequence tracking ensures reliability.
- SCTP: Multi-homing and multi-streaming demand connection awareness.
- Stateless Protocols:
- UDP: Fire-and-forget; no handshake or teardown.
- ICMP: Individual echo requests/replies without session continuity.
HTTP/1.1 introduced persistence (stateful-like connections) but remains fundamentally stateless at the application layer—servers don’t retain client history between requests unless explicitly designed to (e.g., via cookies/sessions).
Beyond Firewalls: Applications and Architectures
The stateful/stateless paradigm extends to application design and cloud-native systems.
Stateless Application Design
RESTful APIs exemplify statelessness: each HTTP request contains all necessary context (auth tokens, user IDs). This enables horizontal scaling—add servers freely without session affinity concerns.
Containers and microservices favor statelessness for orchestration simplicity (Kubernetes deployments roll without data loss).
Stateful Applications
Databases (MySQL, PostgreSQL) and messaging queues (Kafka) maintain state for ACID compliance and ordered processing. Distributed systems use consensus algorithms (Raft, Paxos) to replicate state across nodes.
Security Implications and Best Practices
Stateless firewalls falter against sophisticated threats:
- Fragmented packets bypass rules if reassembled post-inspection.
- No protection against SYN floods without additional mitigations.
Stateful firewalls counter these via:
- Sequence validation preventing hijacking.
- Connection rate limiting.
- Application-layer gateways (ALGs) for FTP, SIP traversal.
Hybrid Recommendation: Deploy stateless at edge (high-speed filtering), stateful internally (deep inspection).
Scalability in Distributed Environments
Cloud architectures prioritize stateless components for elasticity. Stateful services require ‘sticky sessions’ or external state stores (Redis, etcd).
Serverless computing (AWS Lambda) enforces statelessness—functions are ephemeral, scaling to millions instantly.
Use Case Analysis
| Scenario | Recommended Approach | Rationale |
|---|---|---|
| ISP Core Routing | Stateless | Extreme throughput demands |
| Enterprise Perimeter | Stateful | Threat intelligence via context |
| Microservices API | Stateless | Auto-scaling, resilience |
| Database Cluster | Stateful | Transaction integrity |
Future Directions: Next-Gen Stateful Processing
Emerging technologies blur lines:
- eBPF/XDP: Kernel-level stateful packet processing at line rate.
- SmartNICs: Offload state tables to programmable hardware.
- ML-Driven Firewalls: Stateful anomaly detection via behavioral models.
Frequently Asked Questions
Is stateless always faster than stateful?
Generally yes, due to reduced overhead, but modern hardware narrows the gap significantly.
Can stateless firewalls be secure?
With layered defenses (IPS, WAF), yes—but they lack inherent connection awareness.
What’s better for cloud-native apps?
Stateless by default; externalize state to managed services.
Do all TCP connections require stateful firewalls?
No, but stateless handling demands symmetric rules for bidirectional traffic.
Conclusion: Choosing the Right Approach
Neither stateful nor stateless reigns supreme—optimal networks blend both strategically. Stateless components handle scale and speed at boundaries; stateful logic provides depth where context matters. As networks evolve toward zero-trust and automation, understanding this balance becomes paramount for resilient, performant infrastructure.
References
- Transmission Control Protocol Specification — IETF. 1981-09 (authoritative standard). https://datatracker.ietf.org/doc/html/rfc793
- Stateful Inspection Firewalls — Check Point Software (original patent holders). 2023. https://www.checkpoint.com/cyber-hub/network-security/what-is-stateful-inspection/
- Hypertext Transfer Protocol (HTTP/1.1) — IETF. 1999-06 (core web stateless foundation). https://datatracker.ietf.org/doc/html/rfc2616
- Stateful vs Stateless Applications — Red Hat. 2024-03-15. https://www.redhat.com/en/topics/cloud-native-apps/stateful-vs-stateless
- Firewall Fundamentals — Cisco Press. 2022. https://www.cisco.com/c/en/us/support/docs/security/asa-5500-x-series-next-generation-firewalls/113154-stateful-inspection.html