
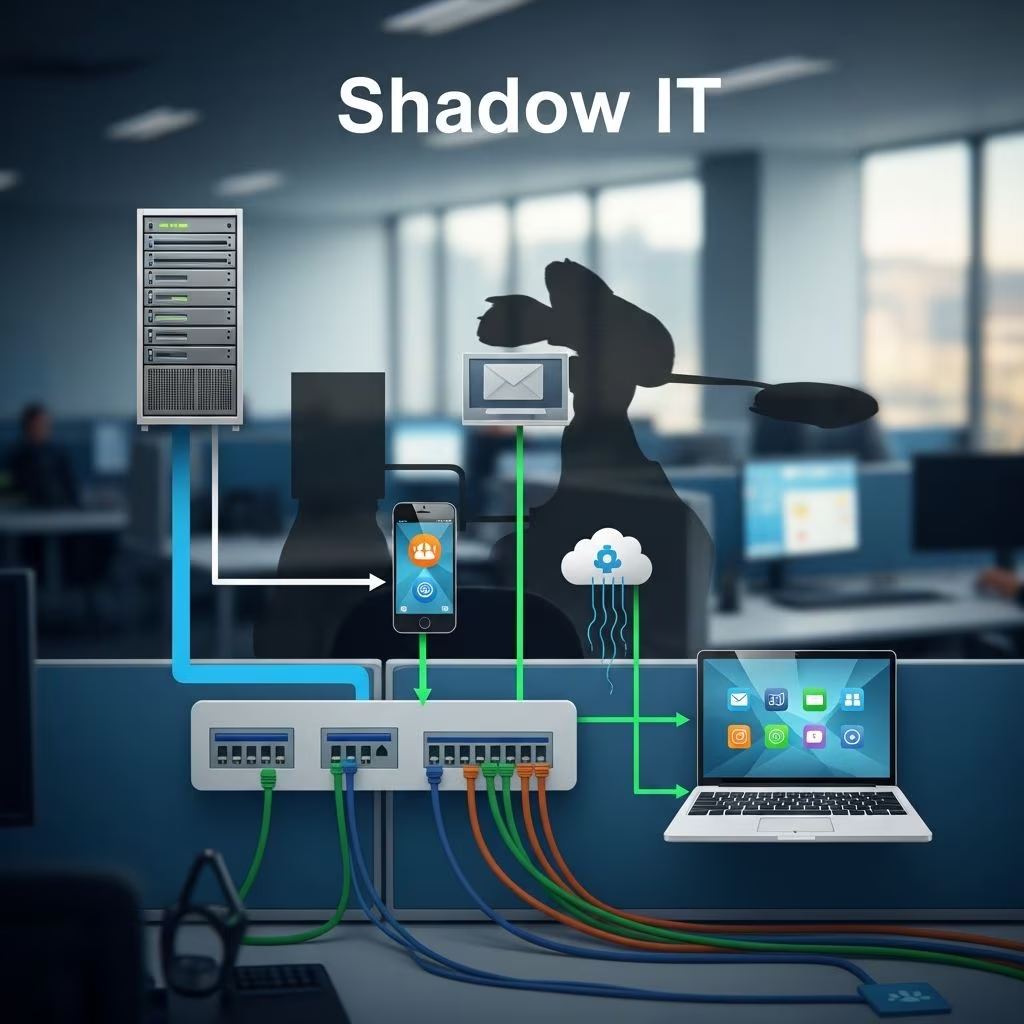
In today’s fast-paced digital landscape, employees often seek tools that boost their productivity without waiting for formal approvals. This practice, known as shadow IT, involves the deployment of software, hardware, or services outside the oversight of an organization’s central IT department. While it can spark innovation, shadow IT introduces substantial risks to data security, regulatory compliance, and operational efficiency.
Organizations across industries grapple with shadow IT as cloud adoption accelerates and remote work becomes standard. According to industry reports, a significant portion of enterprise data now resides in unsanctioned environments, amplifying vulnerabilities. Understanding shadow IT is crucial for IT leaders aiming to balance employee agility with robust security measures.
Defining Shadow IT in Modern Enterprises
At its core, shadow IT encompasses any technology initiative initiated by business units or individuals bypassing IT protocols. This includes everything from personal cloud storage accounts to third-party collaboration apps. Unlike traditional IT, which follows structured procurement and deployment processes, shadow IT thrives in the shadows of corporate governance.
The phenomenon gained prominence with the SaaS revolution, where tools like file-sharing services and project management platforms became accessible with minimal barriers. Employees adopt these solutions to address immediate needs, often perceiving official alternatives as slow or inadequate. However, this autonomy creates visibility gaps that threat actors exploit relentlessly.
Common Forms of Shadow IT
Shadow IT manifests in diverse ways, reflecting the breadth of modern digital tools. Key categories include:
- Cloud-Based SaaS Applications: Tools like unauthorized Dropbox or Slack instances used for file sharing and communication.
- Personal Devices and BYOD: Employees connecting smartphones or laptops to corporate networks without IT vetting.
- Custom Development Projects: Departments building internal apps or databases using low-code platforms.
- Third-Party APIs and Integrations: Connecting approved systems to unapproved services for enhanced functionality.
- Hardware Additions: Unauthorized servers, IoT devices, or peripherals added to the network.
These examples highlight how shadow IT permeates every layer of the tech stack, from endpoints to cloud infrastructure.
Why Employees Embrace Shadow IT
Employee motivations for shadow IT are rooted in practical frustrations. IT departments often face resource constraints, leading to delays in tool provisioning. A survey by Cisco reveals that 35% of workers bypass security protocols to maintain efficiency, underscoring the tension between speed and safety.
Additionally, shadow IT tools frequently offer superior user experiences. Intuitive interfaces and rapid deployment make consumer-grade apps appealing compared to enterprise solutions burdened by compliance features. This “get-it-done” mindset drives adoption, particularly in dynamic sectors like marketing and sales.
Advantages of Shadow IT for Organizations
Despite its risks, shadow IT isn’t entirely negative. It serves as a catalyst for innovation, allowing teams to prototype solutions that IT might overlook. Benefits include:
- Accelerated Productivity: Immediate access to tools reduces workflow bottlenecks.
- Fostering Innovation: Experimental technologies can evolve into approved enterprise assets.
- Cost Savings: Free tiers of SaaS apps minimize upfront expenses.
- Employee Satisfaction: Empowered users report higher morale and engagement.
Forward-thinking IT teams view shadow IT as feedback on gaps in official offerings, using it to refine service catalogs.
The Hidden Dangers of Uncontrolled Shadow IT
While benefits exist, the downsides dominate. Shadow IT expands the attack surface dramatically. Unmonitored apps lack patches, encryption, and access controls, inviting malware, ransomware, and phishing.
| Risk Category | Potential Impact | Example |
|---|---|---|
| Security Breaches | Data theft, malware infection | Unauthorized SaaS exposing credentials |
| Compliance Violations | Fines, legal penalties | GDPR non-compliance via unvetted storage |
| Operational Disruptions | Downtime, integration failures | App sprawl causing data silos |
| Financial Losses | Remediation costs, lost productivity | Breach response averaging $4.5M |
IBM reports that nearly 70% of organizations suffered compromises linked to shadow IT between 2021-2022, emphasizing the urgency of mitigation.
Real-World Consequences and Case Studies
High-profile incidents illustrate shadow IT’s peril. A financial firm faced a massive breach when marketing used an unapproved survey tool, leaking customer data. Remediation costs exceeded millions, alongside reputational damage.
In healthcare, shadow IT often violates HIPAA through personal email for patient records. Such lapses not only risk patient privacy but also invite regulatory scrutiny. These cases demonstrate that ignoring shadow IT equates to playing cybersecurity roulette.
Strategies for Discovering Shadow IT
Visibility is the first step to control. Effective discovery leverages:
- Network Traffic Analysis: Monitoring DNS queries and SaaS domains.
- CASB Solutions: Cloud Access Security Brokers identifying unauthorized access.
- Endpoint Detection: Scanning devices for rogue apps.
- User Behavior Analytics: Flagging anomalous data flows.
Tools from Cisco and CrowdStrike provide comprehensive scanning, revealing up to 50% more shadow IT than manual audits.
Mitigating Shadow IT Without Stifling Innovation
Prohibition alone fails; organizations need balanced approaches:
- Implement Zero Trust Architecture: Verify every access regardless of origin.
- Enable Self-Service Portals: Offer approved alternatives with quick provisioning.
- Conduct Regular Training: Educate on risks and reporting channels.
- Adopt CASB and SWG: Secure Web Gateways enforce policies on unsanctioned apps.
- Foster IT-Business Collaboration: Integrate shadow IT discoveries into roadmaps.
Cloudflare’s Zero Trust model exemplifies this, allowing secure use of any tool while maintaining oversight.
Building a Shadow IT Governance Framework
A robust framework includes policy definition, automated monitoring, and continuous improvement. Start with risk assessments to prioritize high-impact areas like data-heavy departments. Establish clear approval workflows that balance speed with security.
Measure success through metrics like reduced incidents, app consolidation, and employee feedback. Mature programs transform shadow IT from liability to asset.
Future Trends in Shadow IT Management
As AI and edge computing proliferate, shadow IT will evolve. Generative AI tools already emerge as new vectors, demanding adaptive strategies. SASE architectures promise unified visibility across hybrid environments.
Organizations embracing “shadow IT as a service”—where IT curates sandbox environments—will lead. This proactive stance aligns innovation with security in the AI-driven era.
Frequently Asked Questions
What exactly counts as shadow IT?
Any IT resource—software, hardware, or service—used without IT department approval or oversight qualifies as shadow IT.
Is all shadow IT bad?
No, it can drive innovation, but unmanaged instances pose severe risks outweighing benefits.
How can I detect shadow IT in my organization?
Use CASB tools, network monitoring, and employee surveys to uncover hidden applications and services.
What are the best tools to manage shadow IT?
CASB, SWG, Zero Trust platforms, and endpoint management solutions provide comprehensive control.
Can shadow IT ever be beneficial?
Yes, when harnessed properly, it reveals user needs and accelerates adoption of valuable technologies.
References
- What Is Shadow IT? — Cisco. 2024. https://www.cisco.com/site/us/en/learn/topics/security/what-is-shadow-it.html
- What Is Shadow IT? — IBM. 2024-05-01. https://www.ibm.com/think/topics/shadow-it
- What is Shadow IT? Defining Risks & Benefits — CrowdStrike. 2024. https://www.crowdstrike.com/en-us/cybersecurity-101/cloud-security/shadow-it/
- Zero Trust Security — NIST. 2020-08-18. https://nvlpubs.nist.gov/nistpubs/SpecialPublications/NIST.SP.800-207.pdf (Authoritative standard, remains foundational despite age).