
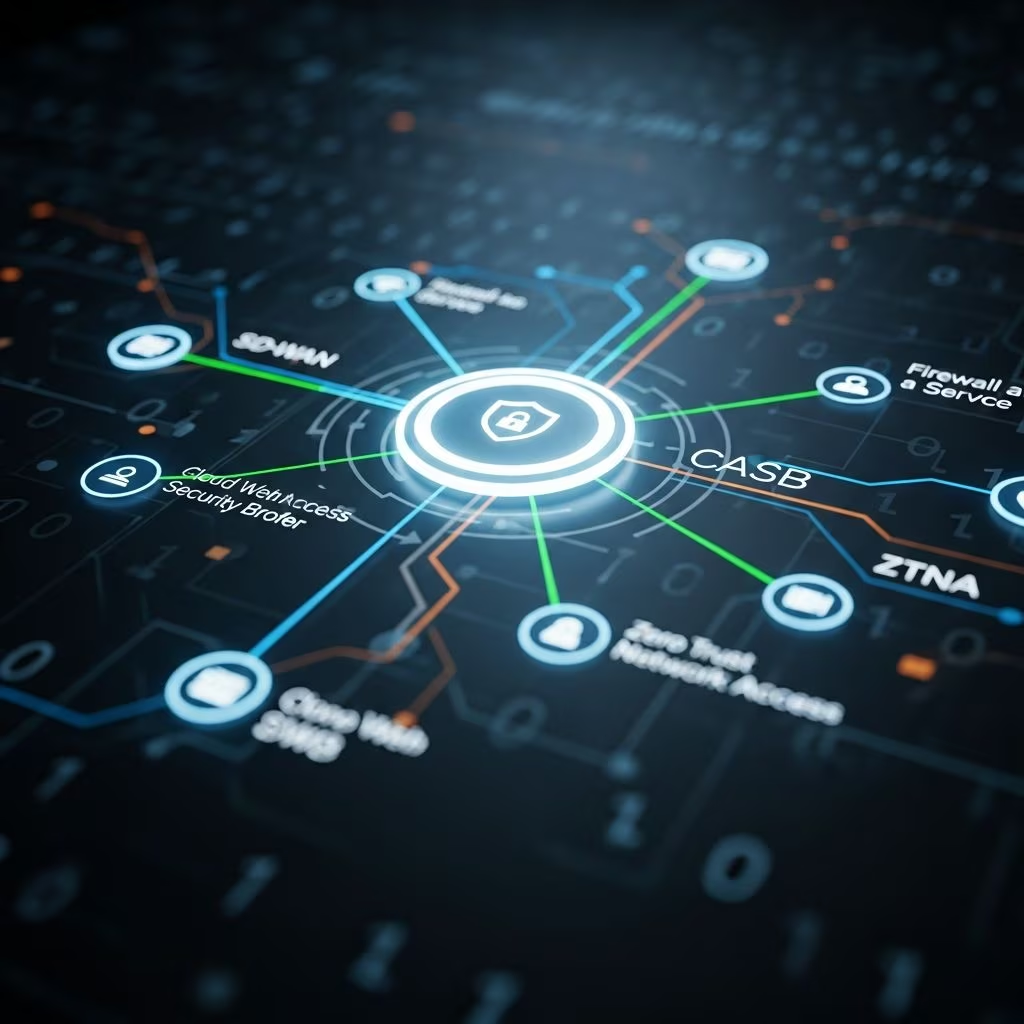
In an era dominated by remote work, cloud applications, and distributed enterprises, traditional networking models are struggling to keep pace. Enter Secure Access Service Edge (SASE), a transformative architecture that merges wide-area networking with comprehensive security services into a single, cloud-delivered platform. Pronounced “sassy,” SASE empowers organizations to deliver consistent performance and protection regardless of user location, device, or application. This approach addresses the limitations of legacy perimeter-based security, which relied on fixed data centers and VPNs, by shifting controls to the cloud edge.
SASE was first conceptualized by Gartner analyst Jason Donne in 2019 as a response to the evolving digital landscape. It combines software-defined wide area networking (SD-WAN) with security functions like firewalls, secure web gateways, and zero-trust access, all orchestrated from global points of presence (PoPs). This convergence simplifies IT operations, reduces costs, and enhances agility for businesses navigating multicloud environments and mobile workforces.
Why SASE Matters in Today’s Digital Landscape
The rise of hybrid work models post-pandemic has exposed the inadequacies of conventional networks. Employees accessing SaaS apps from home, branch offices connecting to multiple clouds, and IoT devices proliferating across edges create complex traffic patterns. Traditional setups route all traffic through central data centers, leading to latency, bottlenecks, and vulnerability to threats.
SASE flips this model by delivering services closer to the user. Networking and security inspect and optimize traffic at the nearest PoP, ensuring low-latency access and real-time threat detection. For enterprises, this means scalable infrastructure that supports digital transformation without the overhead of managing disparate tools.
- Adaptability: Handles fluctuating workloads from remote users and edge computing.
- Cost Efficiency: Consolidates vendors and hardware, lowering OpEx.
- Enhanced Security: Applies policies based on identity, context, and risk, not just IP addresses.
Core Components of a SASE Architecture
A robust SASE platform integrates multiple networking and security capabilities. At its heart is SD-WAN, which intelligently routes traffic over the best available path—whether MPLS, broadband, or 5G—while prioritizing business-critical apps.
Security layers include:
- Secure Web Gateway (SWG): Filters web traffic to block malware, phishing, and unsafe sites.
- Cloud Access Security Broker (CASB): Enforces policies for cloud apps, preventing data leaks and shadow IT.
- Firewall-as-a-Service (FWaaS): Provides next-gen firewall protections like intrusion prevention at the edge.
- Zero Trust Network Access (ZTNA): Grants least-privilege access based on user identity and device posture.
Additional features like Data Loss Prevention (DLP), Secure Email Gateway (SEG), and endpoint protection often round out the stack. These components operate in a unified control plane, enabling centralized management and AI-driven analytics for threat hunting.
| Component | Function | Benefit |
|---|---|---|
| SD-WAN | Dynamic traffic steering | Optimizes performance and reliability |
| SWG | URL filtering and inspection | Blocks web-based threats |
| CASB | Cloud app visibility | Secures SaaS usage |
| ZTNA | Identity-based access | Eliminates VPN vulnerabilities |
| FWaaS | Stateful inspection | Edge firewall protection |
SASE vs. Traditional Networking: A Paradigm Shift
Legacy architectures center security at the headquarters, forcing backhauling that increases latency and costs. SASE decentralizes this to the edge, inspecting traffic locally. Unlike VPNs, which grant broad network access, ZTNA in SASE provides granular, app-specific permissions.
Security Service Edge (SSE) is a related but distinct concept, focusing solely on security services without full networking. Many vendors offer SSE as a SASE subset, allowing phased adoption. Full SASE, however, delivers end-to-end convergence for optimal results.
Key Benefits Driving SASE Adoption
Organizations adopting SASE report significant gains:
- Simplified Operations: Single-pane management replaces siloed tools, reducing vendor sprawl.
- Superior User Experience: Local PoPs minimize latency for VoIP, video, and cloud apps.
- Robust Threat Defense: Cloud-scale AI detects zero-day attacks and automates responses.
- Scalability: Pay-as-you-go model supports growth without hardware refreshes.
- Compliance Support: Built-in DLP and logging aid GDPR, HIPAA adherence.
According to industry analyses, SASE can cut networking costs by 40-60% while boosting security efficacy.
Navigating SASE Deployment Challenges
While promising, SASE implementation requires careful planning. Common hurdles include:
- Legacy Integration: Migrating from on-premises firewalls and VPNs.
- Vendor Selection: Single-vendor vs. multi-vendor (e.g., best-of-breed SSE + SD-WAN).
- Skill Gaps: Teams need training on cloud-native tools.
- Performance Assurance: Ensuring PoP coverage matches global operations.
Start with a proof-of-concept (PoC) for high-traffic branches. Use analytics to baseline current performance and simulate SASE gains.
Step-by-Step Guide to Implementing SASE
Successful rollout follows these phases:
- Assessment: Inventory apps, users, and traffic patterns.
- Strategy Definition: Align with Zero Trust goals and budget.
- Vendor Evaluation: Test platforms for PoP density and feature parity.
- Pilot Deployment: Onboard a user group or site.
- Scale Gradually: Phased migration to minimize risk.
- Optimization: Leverage telemetry for continuous tuning.
Focus on identity-centric policies: verify users via MFA, assess device health, and contextualize risks like location or time.
SASE and Zero Trust: A Natural Synergy
SASE embodies Zero Trust principles—never trust, always verify. It continuously authenticates users, enforces micro-segmentation, and assumes breach. Integrated with IAM systems, SASE prevents lateral movement, a common attack vector.
For multicloud setups, SASE secures east-west traffic between services, extending protection beyond north-south flows.
Market Trends and Vendor Landscape
The SASE market is exploding, projected to exceed $20 billion by 2027. Leaders include Cisco, Zscaler, Palo Alto Networks (Prisma), and Netskope. Emerging players emphasize AI ops and 5G integration.
Trends: Rise of single-vendor SASE for simplicity; SSE for security-first orgs; integration with MEC for ultra-low latency.
Future-Proofing with SASE
As 5G, edge AI, and metaverse apps emerge, SASE’s cloud-native design positions it as foundational. It supports sovereign clouds for data residency and quantum-safe encryption for future threats.
Frequently Asked Questions (FAQs)
What is the difference between SASE and SSE?
SASE includes networking (SD-WAN) plus security; SSE is security-only.
Is SASE suitable for small businesses?
Yes, cloud delivery makes it accessible without heavy upfront costs.
How does SASE improve remote work security?
By securing direct app access without VPNs, reducing attack surfaces.
Can SASE replace my existing firewall?
Often yes, via FWaaS, but hybrid transitions are common.
What are SASE maturity levels?
From basic SSE to full convergence with advanced analytics.
References
- What Is Secure Access Service Edge (SASE)? — Microsoft. 2025-04-15. https://www.microsoft.com/en-us/security/business/security-101/what-is-sase
- What is SASE (Secure Access Service Edge)? — Cisco. 2025-03-20. https://www.cisco.com/site/us/en/learn/topics/security/what-is-secure-access-service-edge-sase.html
- What Is Secure Access Service Edge (SASE)? — IBM. 2025-02-10. https://www.ibm.com/think/topics/sase
- SASE: What is Secure Access Service Edge? — Zscaler. 2025-05-01. https://www.zscaler.com/resources/security-terms-glossary/what-is-sase
- What is SASE? Secure Access Service Edge — Netskope. 2025-01-28. https://www.netskope.com/security-defined/what-is-sase