
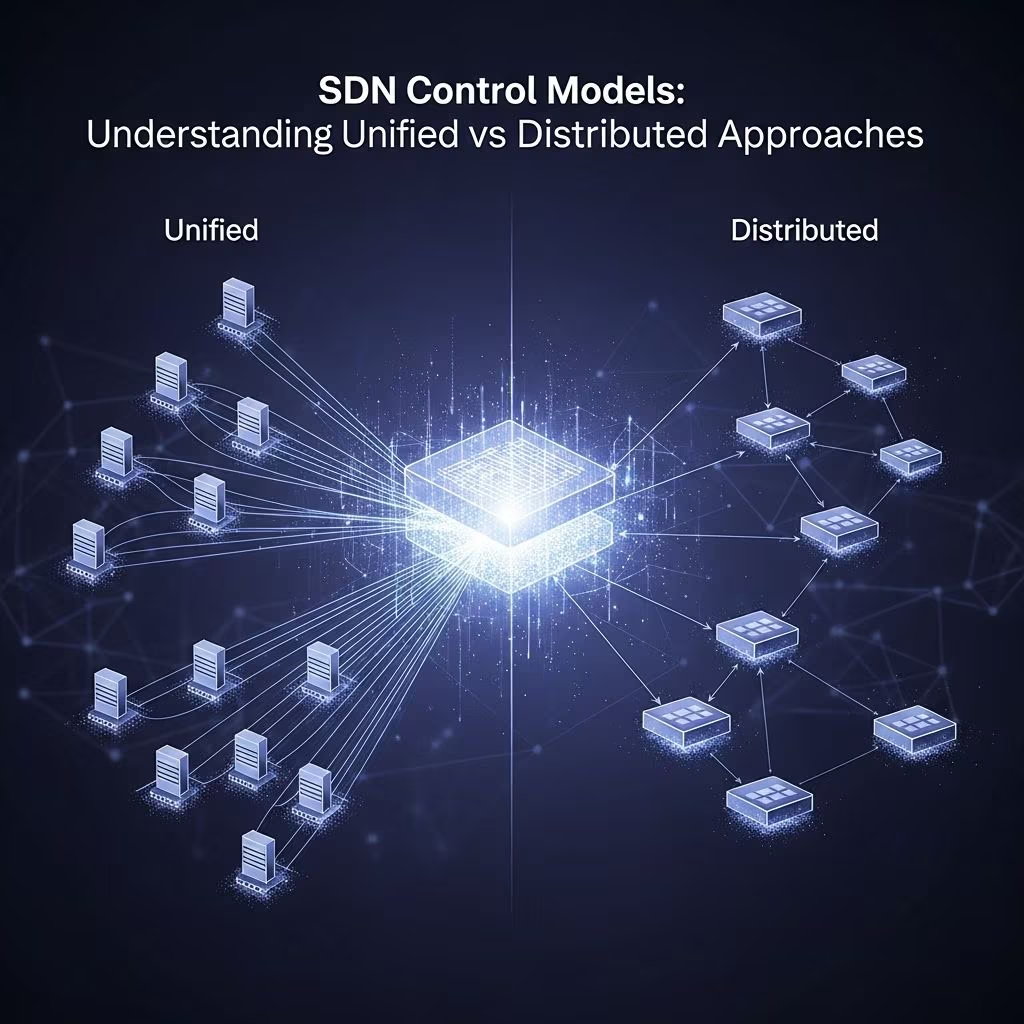
Software-defined networking represents a fundamental shift in how organizations approach network management and operations. Rather than relying on traditional distributed intelligence embedded within individual network devices, SDN consolidates control logic into software-based systems that can orchestrate network behavior across the entire infrastructure. However, not all SDN implementations follow the same architectural blueprint. Organizations deploying or considering SDN solutions face an important decision regarding their control plane design, as this choice has cascading effects on hardware requirements, operational complexity, protocol selection, and long-term scalability prospects.
The Foundation of Modern Network Control Architectures
Before diving into specific architectural models, it’s helpful to understand what makes SDN fundamentally different from legacy networking approaches. Traditional networks embed control logic within individual devices—routers, switches, and firewalls each make independent decisions about traffic forwarding based on routing protocols and local configurations. This distributed approach, while resilient in some respects, creates operational silos and makes it difficult to implement network-wide policies consistently.
SDN separates the control plane (where forwarding decisions occur) from the data plane (where actual traffic moves). This separation enables centralized policy definition while maintaining distributed data forwarding. The architectural question then becomes: where should this control logic reside? Should it be concentrated in a single control entity, or should it be distributed across multiple control points?
Unified Control Plane Architecture: Centralization Benefits and Constraints
A unified SDN architecture consolidates all network control decisions into a centralized controller or controller cluster. In this model, network devices operate as intelligent forwarding engines, receiving instructions from the central authority about how to handle traffic flows.
Protocol Foundation in Unified Models
The primary technology enabling unified SDN architecture is OpenFlow, a standardized protocol that facilitates communication between the controller and network switches. OpenFlow provides a vendor-neutral mechanism for the central controller to reprogram network device forwarding tables in real time. When the controller identifies a new traffic flow or needs to modify routing behavior, it communicates these changes through OpenFlow messages to the appropriate devices.
This protocol-centric approach means that deploying a unified SDN architecture requires careful attention to hardware compatibility. Network devices must explicitly support the OpenFlow standard or similar control protocols. This creates both an advantage and a constraint: organizations can select best-of-breed controllers and switches independently, as long as both support the standard protocol, but they cannot simply retrofit legacy equipment that predates these standards into a unified SDN environment.
Infrastructure and Implementation Considerations
Unified SDN deployments typically involve:
- Controller software platforms that run on dedicated servers or virtual machines
- Network devices equipped with OpenFlow support
- Management interfaces that operators use to define network policies at a high level
- Monitoring systems that provide visibility into network state and performance
The appeal of this approach lies in operational simplicity. Network administrators define policies once at the controller level, and those policies propagate consistently across all switches and routers. There’s no need to log into individual devices or worry about configuration drift. When a network change is required—redirecting traffic for security reasons, implementing quality-of-service policies, or isolating compromised devices—the administrator implements the change at the controller and immediately affects network-wide behavior.
Advantages of Concentrated Control
Unified SDN models offer several compelling benefits for organizations with well-defined requirements and adequate resources:
- Global Policy Enforcement: Network-wide policies can be defined centrally and applied uniformly, reducing inconsistencies and security gaps
- Simplified Management: Operators interact with a single control interface rather than managing dozens or hundreds of individual devices
- Rapid Experimentation: New network behaviors can be tested and deployed quickly through controller modifications
- Clear Visibility: The controller maintains a complete view of network topology and traffic patterns, enabling comprehensive monitoring
Distributed Control Plane Architecture: Resilience Through Decentralization
A distributed SDN approach takes a fundamentally different stance toward control plane architecture. Rather than concentrating all intelligence in a central location, distributed models expose the control capabilities of existing network infrastructure to higher software layers while maintaining multiple points of control across the network.
Protocol Diversity in Distributed Models
Distributed SDN does not depend on OpenFlow or any single control protocol. Instead, it leverages protocols already widely deployed in enterprise networks: Border Gateway Protocol (BGP) for dynamic routing, Multiprotocol Label Switching (MPLS) for traffic engineering, and Generic Routing Encapsulation (GRE) for tunnel creation. These protocols, collectively representing decades of network operational experience, already support sophisticated control capabilities embedded within the network devices themselves.
The distributed approach assumes that modern switches and routers already possess the necessary forwarding intelligence. The goal is not to replace this intelligence but to create software interfaces—specifically northbound application programming interfaces (APIs)—that allow higher-level systems to request network services and adjust forwarding behavior through these existing protocols.
Practical Deployment Scenarios
Distributed SDN works particularly well in environments where:
- Significant network infrastructure already exists and cannot be immediately replaced
- Organizations want to gradually introduce software-defined capabilities without forking-lifting existing equipment
- Network operators possess strong expertise in traditional routing and switching protocols
- Extreme availability and fault tolerance are critical requirements
In a distributed model, cloud management software or orchestration platforms communicate with multiple network nodes through APIs and existing protocols. When an application requires specific network connectivity, it sends a request through the northbound interface, which is then translated into appropriate protocol messages to the relevant network devices. Each device contributes its capabilities to fulfilling the overall request, creating a more organic integration with existing infrastructure.
Advantages of Distributed Control
The decentralized approach addresses limitations that organizations sometimes encounter with unified controllers:
- Fault Tolerance: No single point of failure can disrupt network forwarding behavior; devices continue functioning even if one control point becomes unavailable
- Scalability: Additional control points can be added incrementally as the network grows, avoiding the performance ceiling of a single controller
- Hardware Flexibility: Organizations can work with equipment from multiple vendors without requiring universal OpenFlow support
- Graceful Integration: Existing network infrastructure and operational expertise can be preserved while gradually introducing software-defined capabilities
Information Gathering and State Management
A critical difference between these architectures lies in how they acquire network state information. Unified SDN requires devices to report their status through OpenFlow, which provides detailed flow-level information but demands compatibility with the OpenFlow protocol stack.
Distributed SDN faces a different challenge: it must gather extensive performance and status information across multiple protocol layers, device types, and vendors. This requires robust monitoring infrastructure capable of aggregating data from SNMP monitors, syslog streams, NetFlow exports, and other telemetry sources. The distributed model essentially treats the existing network as a complex system to be observed comprehensively, then surfaces relevant capabilities through APIs that applications can invoke.
Comparative Analysis Framework
| Characteristic | Unified Architecture | Distributed Architecture |
|---|---|---|
| Control Concentration | Single or redundant central controller | Multiple distributed controllers/nodes |
| Primary Protocol | OpenFlow | BGP, MPLS, GRE, existing protocols |
| Hardware Compatibility | Requires OpenFlow support | Works with existing infrastructure |
| Deployment Complexity | Medium (requires new hardware/software) | Lower (leverages existing systems) |
| Fault Tolerance | Medium to High (with redundancy) | High (inherent distribution) |
| Policy Consistency | Excellent (centrally defined) | Good (requires careful coordination) |
| Operational Expertise Required | SDN-specific knowledge | Traditional networking + SDN concepts |
Network Virtualization and Overlay Technologies
Neither purely unified nor distributed approaches operate in isolation. Virtual networking technologies—overlay and tunnel mechanisms that create logical networks atop physical infrastructure—represent a complementary dimension. These overlay technologies function effectively with either control model, creating an additional layer of abstraction that applications and cloud platforms can leverage.
When considering overlay technologies alongside core SDN architecture choices, organizations gain flexibility in how they segment traffic, implement multi-tenancy, and connect geographically dispersed resources. An overlay layer can operate independently of whether the underlying SDN control is centralized or distributed, though the choice of control architecture will influence how effectively the overlay layer can communicate with underlying network capabilities.
Determining the Right Fit for Your Environment
Selecting between unified and distributed SDN architectures requires careful assessment of organizational circumstances:
Choose Unified SDN when: You’re building new network infrastructure from scratch, standardizing on specific vendors, requiring rapid policy changes, or operating data centers with homogeneous equipment. The centralized approach excels in greenfield environments where controller compatibility is not a constraint.
Choose Distributed SDN when: You need to integrate SDN capabilities into existing heterogeneous networks, cannot risk single points of failure, operate multiple independent network domains, or want to preserve existing operational procedures while gradually introducing software-defined capabilities.
Consider Hybrid Approaches: Many organizations find value in deploying unified controllers for specific network segments (such as data center fabric) while maintaining distributed control for wide-area or edge networks. This mixed strategy allows leveraging the strengths of both models in appropriate contexts.
Implementation and Testing Strategy
Regardless of which architectural approach you select, successful deployment demands structured testing and validation. Before committing to production traffic, organizations should establish isolated network segments that mirror their intended architecture, then thoroughly test convergence behavior, failover scenarios, and performance under various load conditions.
The infrastructure supporting your chosen architecture—whether this means deploying controller software, acquiring OpenFlow-compatible devices, or establishing monitoring systems for distributed nodes—must be validated against realistic traffic patterns and failure scenarios. This preparation prevents costly surprises after production deployment.
Conclusion
The choice between unified and distributed SDN control architectures is not a simple binary decision but rather a reflection of organizational circumstances, existing infrastructure, risk tolerance, and operational capabilities. Unified models offer elegant simplicity and consistent policy enforcement for organizations building new environments, while distributed architectures provide pragmatic paths for integrating software-defined capabilities into established networks with minimal disruption. Many mature network organizations find that the most effective approach combines elements of both, strategically applying unified control where appropriate and distributed intelligence where integration and resilience matter most.
References
- Comparative Analysis of Centralized and Distributed SDN Control Plane Architectures — Centre for Education and Advanced IT Research (CEAI). 2024. http://ceai.srait.ro/index.php?journal=ceai&page=article&op=viewFile&path%5B%5D=9164&path%5B%5D=1740
- A Decentralized SDN Architecture for the WAN — ACM Digital Library. 2024. https://dl.acm.org/doi/10.1145/3651890.3672257
- Centralized vs. Decentralized vs. Distributed Systems — GeeksforGeeks. 2024. https://www.geeksforgeeks.org/system-design/comparison-centralized-decentralized-and-distributed-systems/
- Centralized vs. Decentralized vs. Distributed Networks: The History and Future — LiveAction. 2025. https://www.liveaction.com/resources/blog-post/centralized-vs-decentralized-vs-distributed-networks-the-history-future/
- Centralized vs. Distributed Network Management — ZPE Systems. 2025. https://zpesystems.com/centralized-vs-distributed-network-management-zs/