
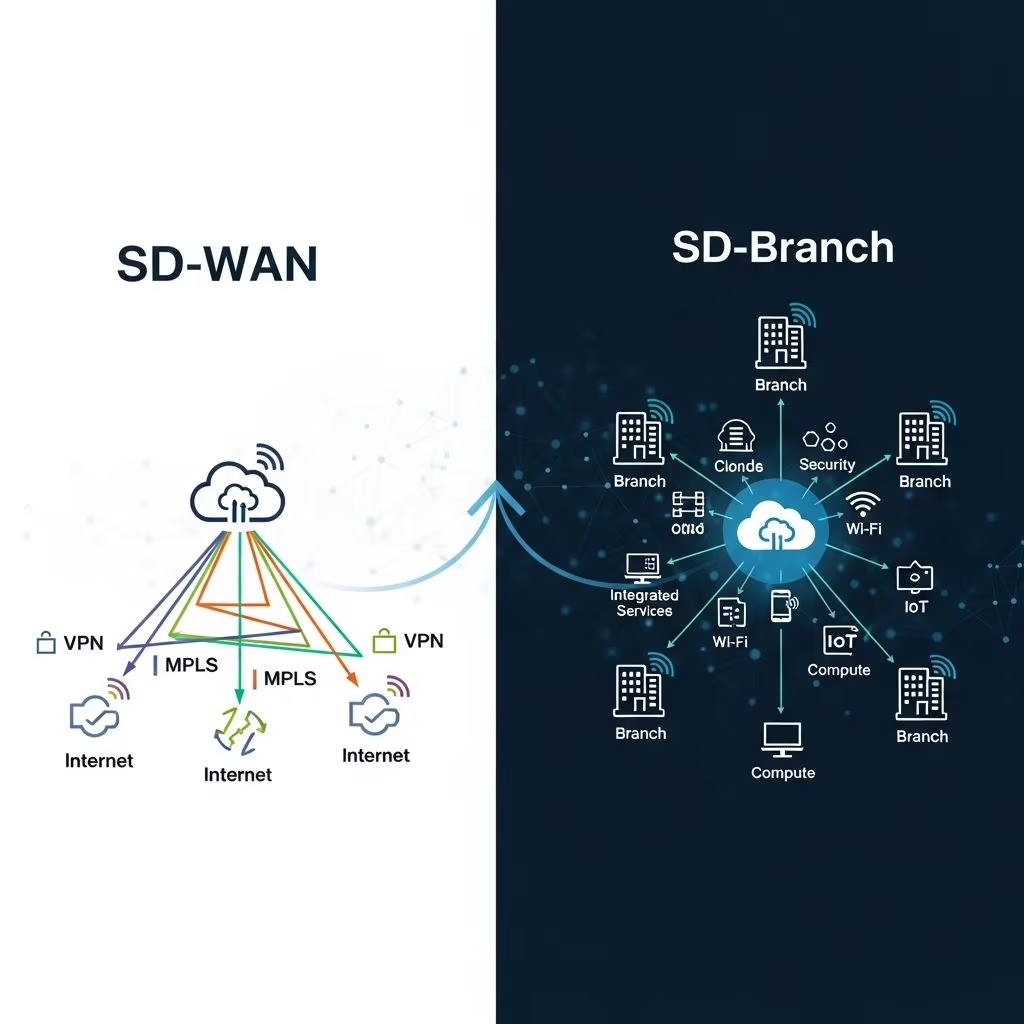
Modern enterprise networks are undergoing a profound transformation, driven by the need for agility, cost efficiency, and robust security across distributed locations. At the heart of this shift lies the progression from Software-Defined Wide Area Network (SD-WAN) to Software-Defined Branch (SD-Branch). While SD-WAN optimized connectivity between sites, SD-Branch expands this intelligence into the local area network (LAN) at branch offices, creating a cohesive ecosystem that integrates routing, switching, wireless access, and security functions.
Foundational Role of SD-WAN in Enterprise Connectivity
SD-WAN emerged as a game-changer for organizations relying on traditional Multiprotocol Label Switching (MPLS) networks. It introduces a software overlay that dynamically selects the best paths for traffic based on real-time conditions, applications, and policies. This approach leverages multiple transport links—such as MPLS, broadband internet, and 4G/5G— to ensure optimal performance without overprovisioning expensive circuits.
Key advantages include application-aware routing, which prioritizes critical business apps like video conferencing or SaaS tools, and centralized management that simplifies policy enforcement across global sites. According to official documentation from leading vendors, SD-WAN reduces operational complexity by abstracting hardware-specific configurations into cloud-based controllers.
Extending Intelligence: The Birth of SD-Branch
SD-Branch takes SD-WAN’s principles and applies them holistically to the entire branch environment. Rather than treating the WAN edge in isolation, it unifies the WAN gateway with LAN switching, Wi-Fi access points, firewalls, and even local services like LTE backup. This convergence happens on a single platform, often a universal customer premises equipment (uCPE) device, managed via a unified dashboard.
The architecture typically features a base SD-WAN appliance augmented with virtual network functions (VNFs) for LAN tasks. For instance, it can orchestrate wired Ethernet switches and wireless access points alongside WAN optimization, all under policy-driven automation. This setup minimizes the sprawl of disparate appliances, which traditionally required separate consoles for routers, firewalls, and access points.
Core Components of an SD-Branch Architecture
- Centralized Orchestration: A cloud or on-premises controller pushes configurations, monitors performance, and applies zero-touch provisioning to new branches.
- Integrated Edge Device: High-performance hardware or virtual appliances hosting SD-WAN, next-generation firewalls (NGFW), secure web gateways (SWG), and LAN controllers.
- Policy Engine: Intent-based policies that define security, QoS, and traffic steering across WAN and LAN boundaries.
- Analytics and Telemetry: Real-time visibility into user experience, bandwidth utilization, and threat detection.
This integrated stack enables branches—retail stores, remote offices, or factory floors—to operate autonomously yet remain under enterprise-wide governance.
Key Benefits Driving SD-Branch Adoption
Organizations adopting SD-Branch report significant gains in efficiency and resilience. Primarily, it slashes the hardware footprint: instead of 5-10 devices per site, a single platform suffices, cutting power, space, and cabling needs. Centralized management further streamlines operations; IT teams can push firmware updates, troubleshoot issues, or scale capacity remotely.
| Aspect | Traditional Branch | SD-Branch |
|---|---|---|
| Device Count | Multiple (router, switch, AP, firewall) | Single uCPE platform |
| Management | Fragmented consoles | Single pane of glass |
| Security | Point solutions | Unified policy enforcement |
| Deployment Time | Weeks | Hours via zero-touch |
| Cost Savings | High CapEx/OpEx | 30-50% reduction |
Security integration stands out: SD-Branch embeds NGFW capabilities at the LAN edge, inspecting traffic from IoT devices or guest Wi-Fi before it hits the WAN. Bandwidth efficiency improves through intelligent steering, ensuring low-latency for VoIP while compressing bulk data transfers.
Navigating Implementation Challenges
Despite its promise, transitioning to SD-Branch isn’t seamless. Legacy investments in branch hardware pose a barrier; enterprises hesitate to rip-and-replace routers or switches still under warranty. Vendors address this via phased migrations: start with SD-WAN overlay on existing gear, then layer in branch functions as hardware refreshes occur.
Another hurdle is skill gaps. IT staff accustomed to CLI-based configs must adapt to policy-driven paradigms. Interoperability between vendors’ ecosystems also demands scrutiny, as not all SD-Branch solutions play nicely with multi-vendor environments. Scalability testing is crucial, especially for chains with hundreds of sites, to validate performance under peak loads.
Vendor Innovations Shaping SD-Branch
Major players like Cisco, Fortinet, Juniper, and Palo Alto Networks lead the charge. Cisco’s SD-Branch leverages ENCS platforms for VNF hosting, enabling flexible service chaining. Fortinet’s Secure SD-Branch extends FortiGate firewalls to LAN edges via FortiSwitch and FortiAP integration, emphasizing unified threat management.
Juniper emphasizes automation in its Mist AI-driven SD-Branch, while Palo Alto highlights convergence with SASE. These solutions evolve rapidly, incorporating 5G slicing and edge computing to support emerging workloads like AR/VR in retail.
SD-Branch’s Path Toward SASE Convergence
SD-Branch represents an interim step in the broader shift to Secure Access Service Edge (SASE). While SD-Branch maintains on-premises elements for latency-sensitive apps, SASE delivers these functions as cloud services: SD-WAN, ZTNA, CASB, and DLP from Points of Presence (PoPs) worldwide. The progression is natural—many SD-Branch platforms now offer hybrid modes, backhauling non-critical traffic to cloud gateways.
This evolution supports cloud-first strategies, where branches connect directly to SaaS without hairpinning to data centers, reducing latency and costs. Gartner predicts that by 2025, 50% of enterprises will adopt SASE, with SD-Branch serving as a bridge for those not ready for full cloud migration.
Real-World Use Cases and Success Metrics
In retail, SD-Branch powers point-of-sale systems with secure, low-latency connectivity and guest Wi-Fi segmentation. Manufacturing sites benefit from IoT orchestration, where sensors feed into edge analytics before WAN transmission. Financial services leverage it for PCI-compliant branches with embedded encryption.
Case studies show 40-60% OpEx reductions, 99.99% uptime via redundant paths, and faster breach detection through integrated logging.
Future Outlook: AI and Edge in SD-Branch
Looking ahead, AI/ML integration will predict failures, auto-tune policies, and detect anomalies proactively. Edge computing will offload AI inference to branches, supporting autonomous operations. 5G and private networks will further blur WAN/LAN boundaries, making SD-Branch indispensable.
Frequently Asked Questions (FAQs)
What is the main difference between SD-WAN and SD-Branch?
SD-WAN focuses on WAN optimization and path selection, while SD-Branch extends this to LAN switching, Wi-Fi, and security for full branch unification.
Is SD-Branch suitable for small businesses?
Yes, its simplified management scales from single sites to enterprises, with cloud options minimizing upfront costs.
How does SD-Branch improve security?
It applies consistent policies across LAN/WAN, embeds NGFW at the edge, and enables micro-segmentation for IoT and users.
Can SD-Branch coexist with legacy equipment?
Absolutely—phased overlays allow gradual integration without immediate forklift upgrades.
What role does SD-Branch play in SASE adoption?
It provides on-premises foundations that hybridize with cloud SASE services for flexible, future-proof networks.
References
- What Is SD-Branch? | Architecture & Modern Role — Palo Alto Networks. 2023. https://www.paloaltonetworks.com/cyberpedia/sd-branch
- SD-WAN / SD-Branch Deployment Guide — Fortinet. 2022-10-01. https://docs.fortinet.com/document/fortigate/7.0.0/sd-wan-sd-branch-deployment-guide/643203/introduction
- Software-Defined Branch Whitepaper — Cisco. 2021. https://www.cisco.com/c/dam/en/us/solutions/collateral/enterprise-networks/sd-branch/sd-branch-whitepaper.pdf
- What is SD-Branch? — HPE. 2024. https://www.hpe.com/us/en/what-is/sd-branch.html
- What Is SD-Branch? — Juniper Networks. 2023. https://blogs.juniper.net/en-us/ask-juniper/what-is-sd-branch