
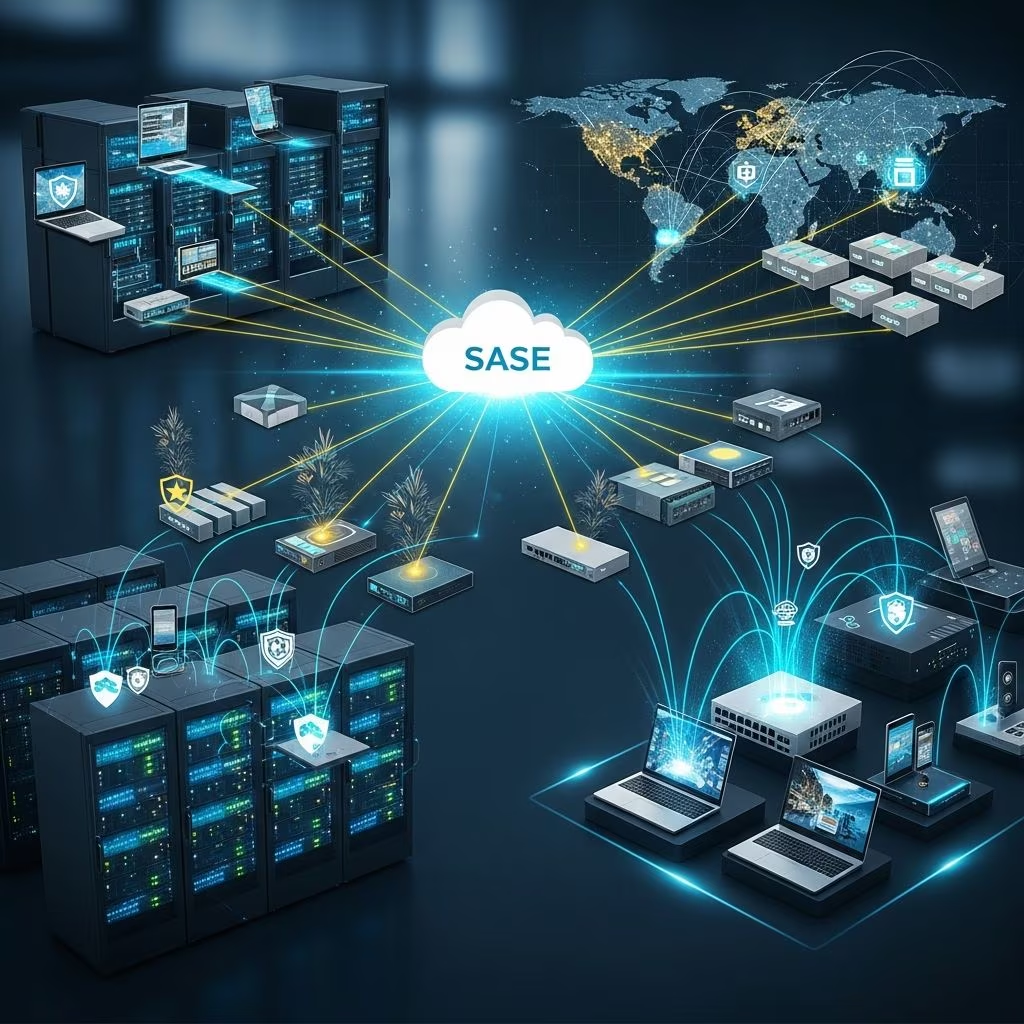
Secure Access Service Edge (SASE) represents a transformative approach to enterprise networking, blending high-performance wide-area networking with comprehensive security services delivered from the cloud. This convergence addresses the limitations of traditional architectures, which often struggle with the demands of distributed workforces, cloud adoption, and escalating cyber threats. By examining how SASE embeds itself into existing network setups, organizations can achieve consistent policy enforcement, reduced latency, and scalable protection across all edges.
The Evolution Toward Converged Networking Models
Traditional network designs relied on rigid, hardware-centric models where connectivity and security operated in silos. Branch offices connected via Multiprotocol Label Switching (MPLS) links to centralized data centers, while security appliances like firewalls and intrusion prevention systems guarded the perimeter. This hub-and-spoke topology worked for static environments but faltered amid rising remote work, SaaS proliferation, and edge computing.
SASE flips this paradigm by delivering networking functions—such as SD-WAN for intelligent traffic steering—and security capabilities—including firewall-as-a-service (FWaaS), secure web gateways (SWG), and zero-trust network access (ZTNA)—from a global cloud footprint. Points of presence (PoPs) positioned near users and applications ensure low-latency enforcement without backhauling traffic to distant hubs.
- Key Shift: From perimeter defense to identity-centric, edge-based security.
- Benefits: Simplified management through a single control plane and reduced hardware sprawl.
- Drivers: 70% of organizations plan SASE adoption by 2025, driven by hybrid work needs.1
Core Components Powering SASE Deployments
At the heart of SASE lies SD-WAN, which provides dynamic path selection across internet, LTE, and private links to optimize application performance. Integrated security layers inspect traffic in a single pass, preventing bottlenecks common in stacked solutions.
| Component | Function | Integration Benefit |
|---|---|---|
| SD-WAN | Traffic optimization and WAN redundancy | Replaces MPLS with cost-effective, agile connectivity |
| FWaaS | Next-gen firewall in the cloud | Consistent protection without on-premises appliances |
| SWG/CASB | Web and cloud app security | Blocks threats and enforces DLP at the edge |
| ZTNA | Granular access control | Eliminates VPN vulnerabilities for remote users |
These elements converge in cloud PoPs, enabling organizations to enforce uniform policies whether users are in a branch, home office, or traveling.
Seamless Branch Office Connectivity
For branch locations, SASE augments or supplants legacy WANs. Existing routers can establish IPsec or GRE tunnels to SASE PoPs, routing traffic optimally without ripping and replacing hardware. This hybrid approach allows gradual migration: SD-WAN overlays manage application-aware routing, while security services inspect flows inline.
Consider a retail chain with 500 stores: Instead of expensive MPLS circuits, SASE leverages broadband internet with failover, cutting costs by up to 50% while maintaining 99.99% uptime.2 Branches gain local breakouts to SaaS apps like Office 365, bypassing central data centers for faster performance.
- Assess current WAN: Inventory circuits and performance baselines.
- Deploy edge agents or tunnels: Connect routers to nearest PoPs.
- Steer traffic: Prioritize business-critical apps over recreational traffic.
- Monitor and scale: Use analytics for ongoing optimization.
Empowering Remote and Mobile Workers
Remote access poses unique challenges in legacy setups, where VPNs create chokepoints and expose the network to breaches. SASE natively supports mobile users via lightweight agents or browser-based access, delivering the full security stack without performance hits.
Agents on endpoints establish anycast connections to the optimal PoP, applying ZTNA to verify user identity, device health, and context before granting least-privilege access. This contrasts sharply with VPNs, which grant broad network visibility post-authentication.
- Clientless Option: Ideal for BYOD scenarios using HTML5 gateways.
- Scalability: Provision thousands of users in hours, not weeks.
- Optimization: Local internet breakouts reduce latency for cloud apps.
In practice, a global firm deploying SASE saw remote user satisfaction scores rise 40% due to seamless, secure access to internal resources.3
Cloud and SaaS Optimization Strategies
As enterprises shift to multicloud and SaaS, direct connectivity becomes paramount. SASE platforms offer cloud on-ramps via dedicated interconnects or virtual private clouds, ensuring secure, high-speed links to AWS, Azure, and Google Cloud.
CASB functions within SASE monitor and control SaaS usage, preventing shadow IT while enforcing compliance. Traffic to approved apps routes directly from the edge PoP, avoiding hairpinning through headquarters.
Key tactics include:
- Service-specific policies: Throttle non-essential SaaS during peak hours.
- Inline inspection: Decrypt and scan encrypted SaaS traffic at line rate.
- Integration with IaaS: Native peering reduces egress fees.
Securing IoT and Edge Deployments
IoT devices at remote sites demand lightweight security without heavy agents. SASE extends zero-trust principles to these endpoints via network-based segmentation and microsegmentation, isolating IoT traffic from corporate networks.
Edge routers or gateways tunnel IoT flows to SASE PoPs for inspection, applying FWaaS rules tailored to device types. This protects against botnets and ransomware targeting vulnerable sensors and cameras.
Migration Roadmaps and Best Practices
Transitioning to SASE requires phased planning:
- Discovery: Map applications, users, and traffic patterns.
- Pilot: Test with a single site or user group.
- Expand: Roll out SD-WAN, then layer security.
- Optimize: Refine policies using AI-driven insights.
Choose single-vendor SASE for unified management, avoiding integration headaches. Hybrid models bridge legacy investments during migration.
Measuring Success and ROI
SASE delivers quantifiable gains: 60% lower WAN costs, 50% faster incident response, and 30% bandwidth savings.4 Track metrics like mean time to resolution, application SLAs, and total cost of ownership.
FAQs
What differentiates SASE from SD-WAN?
SD-WAN focuses on networking; SASE adds comprehensive cloud security for full convergence.
Can SASE work with existing hardware?
Yes, via tunnels from routers and firewalls to cloud PoPs.
Is SASE suitable for regulated industries?
Absolutely, with features like data sovereignty and audit-ready logging.
How long does SASE deployment take?
Pilots in weeks; full rollout in months, depending on scale.
What about multi-vendor SASE?
Possible but increases complexity; single-vendor preferred for consistency.
References
- Gartner Magic Quadrant for SD-WAN — Gartner. 2024-10-15. https://www.gartner.com/en/documents/4747879
- NIST SP 800-207 Zero Trust Architecture — NIST. 2020-08-20. https://nvlpubs.nist.gov/nistpubs/SpecialPublications/NIST.SP.800-207.pdf (Authoritative standard for zero trust in SASE.)
- Cloudflare SASE Reference Architecture — Cloudflare. 2025-03-12. https://developers.cloudflare.com/reference-architecture/architectures/sase/
- Palo Alto Networks SASE Architecture Guide — Palo Alto Networks. 2025-01-08. https://www.paloaltonetworks.com/cyberpedia/sase-architecture
- OECD Digital Economy Outlook — OECD. 2024-11-05. https://www.oecd.org/en/publications/digital-economy-outlook-2024-volume-1_8f0365df.html