
The digital landscape demands robust mechanisms for verifying user identities across diverse platforms. At the heart of this lies SAML, or Security Assertion Markup Language, an open protocol that facilitates secure exchange of authentication and authorization details. This technology underpins modern single sign-on (SSO) solutions, allowing users to authenticate once and access myriad services without repeated logins. In an era where enterprises juggle numerous SaaS applications, SAML emerges as a cornerstone for efficient, secure access management.
Core Principles of SAML Technology
SAML operates on XML-based structures to encapsulate security assertions—formal statements about a subject’s attributes, authentication status, or entitlements. These assertions are digitally signed to prevent tampering, ensuring trustworthiness during transmission. Unlike traditional password-based systems, SAML decouples authentication from individual applications, centralizing it within trusted identity systems.
The protocol’s strength lies in its federated model, where trust relationships span organizational boundaries. This enables scenarios like employees accessing partner portals or customers logging into vendor services using corporate credentials. SAML’s extensibility supports various binding mechanisms, including HTTP redirects and POSTs, adapting to web and non-web environments alike.
Key Players in the SAML Ecosystem
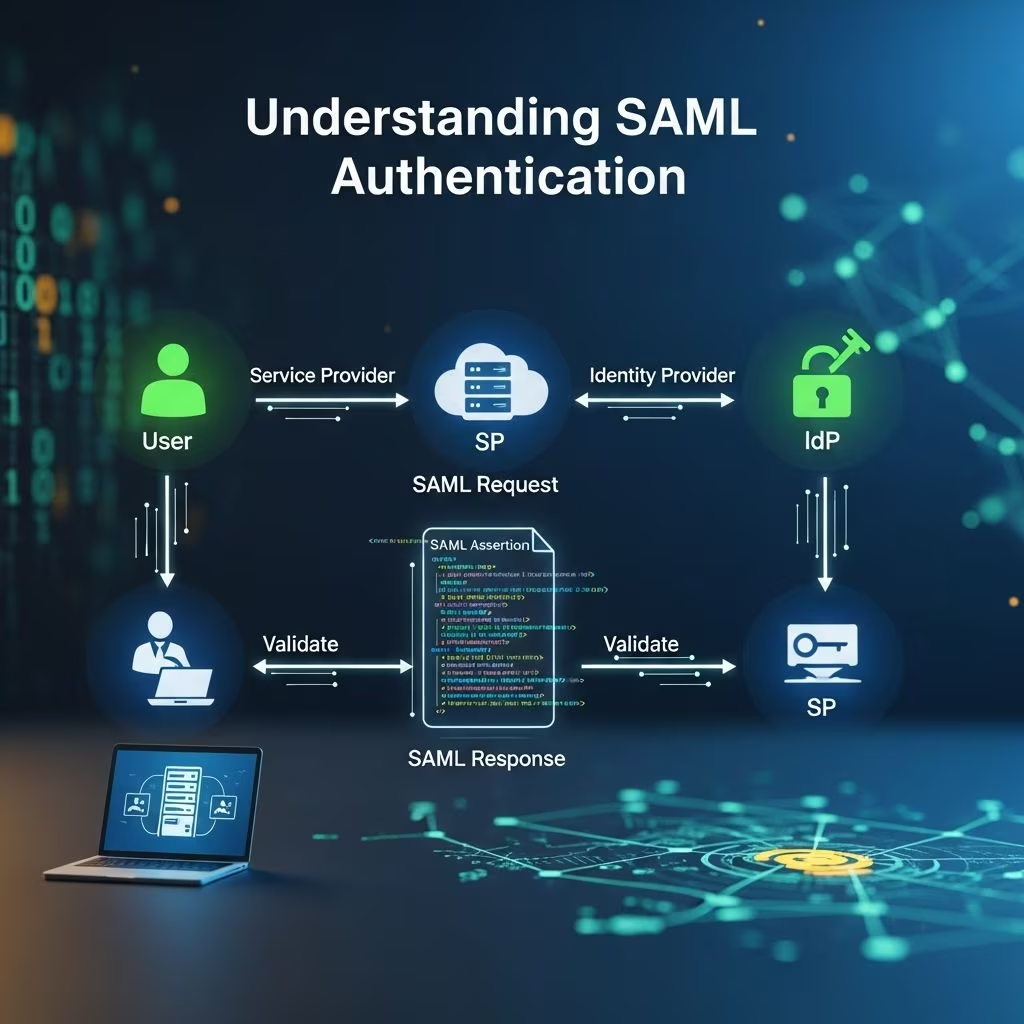
SAML authentication revolves around three primary entities:
- Identity Provider (IdP): The authoritative source that authenticates users. Examples include Okta, Microsoft Entra ID, or Ping Identity. The IdP verifies credentials and issues assertions.
- Service Provider (SP): The application or resource requiring access, such as Salesforce or Google Workspace. SPs rely on IdPs for verification instead of maintaining separate user stores.
- Principal (User): The end-user seeking access, interacting via browsers or clients.
Trust is established through metadata exchanges—XML documents detailing endpoints, certificates, and supported bindings. Organizations configure these to define SAML federations, often using tools like entity descriptors for automated setup.
Evolution and Standards Behind SAML
Developed by the OASIS consortium, SAML traces its roots to 2002 with version 1.0, evolving through 1.1 to the robust SAML 2.0 in 2005. The latest iteration, SAML 2.0, introduced enhancements like enhanced client/proxy (ECP) profiles for mobile and thick-client support, alongside improved internationalized domain names.
SAML 2.0 remains the de facto standard, ratified as an OASIS specification.1 Its backward compatibility and widespread adoption by major vendors ensure longevity, even as newer protocols like OpenID Connect gain traction for specific use cases.
Step-by-Step SAML Authentication Flow
SAML workflows typically follow the Web Browser SSO Profile. Here’s a breakdown:
- Access Request: User navigates to SP-protected resource.
- Redirect to IdP: SP issues AuthnRequest (XML) via browser redirect or POST.
- User Authentication: IdP prompts for credentials if needed (e.g., MFA).
- Assertion Creation: IdP generates SAML Response with assertion, signs it, and sends via browser POST to SP’s Assertion Consumer Service (ACS).
- Validation and Access: SP verifies signature, checks conditions (e.g., audience, validity), extracts attributes, and grants session.
For logout, SAML supports Single Logout (SLO), propagating termination across federations via LogoutRequest/Response messages.
Types of SAML Assertions Explained
Assertions form the payload of SAML messages, categorized into three types:
- Authentication Assertions: Confirm user identity, including authn instant, method (e.g., password, X.509), and session index.
- Attribute Assertions: Convey user attributes like email, roles, or group memberships for authorization.
- Authorization Decision Assertions: State access decisions (permit/deny) with evidence and resource details.
These are packaged in SAML Responses, encrypted optionally for confidentiality. Conditions like NotBefore/NotOnOrAfter timestamps enforce validity windows, mitigating replay attacks.
Benefits Driving SAML Adoption
Organizations embrace SAML for multifaceted advantages:
| Benefit | Description |
|---|---|
| Seamless User Experience | SSO eliminates password fatigue, boosting productivity. |
| Centralized Management | IdPs handle provisioning/deprovisioning, reducing admin overhead. |
| Heightened Security | Eliminates SP-stored passwords; supports MFA and just-in-time provisioning. |
| Compliance Alignment | Facilitates audit trails and attribute-based access control (ABAC). |
Microsoft highlights SAML’s role in unifying identity management, cutting provisioning time significantly.2
Real-World Implementations and Use Cases
SAML shines in enterprise settings. Consider a multinational firm using Microsoft Entra ID as IdP for SSO to Office 365 (SP), AWS, and custom apps. Partners federate via SAML for B2B portals, sharing just necessary attributes.
In education, universities leverage SAML for integrating learning management systems with student information portals. Healthcare providers use it for secure clinician access to electronic records across systems, ensuring HIPAA compliance through encrypted assertions.
Navigating SAML Security Considerations
While robust, SAML demands vigilant configuration:
- Certificate Management: Rotate signing/encryption keys regularly; validate chains.
- Binding Choices: Prefer POST over artifact for direct assertion transmission, reducing oracle risks.
- Clock Skew: Synchronize NTP to avoid validity rejections.
- Entity Validation: Enforce strict audience and issuer checks.
Vulnerabilities like XML Signature Wrapping require patched libraries (e.g., OpenSAML). Adopting profiles like Web SSO with ECP enhances resilience.
SAML vs. Competing Protocols
SAML contrasts with OAuth 2.0 (delegation-focused) and OpenID Connect (JWT-based identity layer atop OAuth). SAML excels in enterprise SSO with rich attributes; OIDC suits APIs and mobile.
| Aspect | SAML | OIDC |
|---|---|---|
| Format | XML | JSON/JWT |
| Primary Use | Web SSO | API Authz |
| Enterprise Fit | High (attributes) | Moderate |
Hybrid deployments often layer protocols for comprehensive coverage.
Implementing SAML in Modern Architectures
Deployment involves IdP/SP configuration, metadata exchange, and testing. Tools like Shibboleth (open-source) or commercial gateways simplify integration. Cloud providers offer managed SAML (e.g., AWS IAM).
For microservices, SAML front-ends via API gateways translate to JWTs internally. Zero-trust models extend SAML with continuous authorization via attribute refresh.
Future Directions for SAML
SAML 2.0’s maturity ensures relevance, with extensions for browserless authn and FIDO integration. Convergence with SCIM for provisioning and emerging standards like OAuth 2.0 Federation hints at hybrid futures.
Frequently Asked Questions
What exactly is SAML used for?
SAML enables SSO by securely passing authentication data from an IdP to SPs, allowing one-time login for multiple services.
Is SAML 2.0 still relevant in 2026?
Yes, SAML 2.0 dominates enterprise SSO, supported by all major IdPs and SPs.
Can SAML handle mobile applications?
Absolutely, via ECP profiles and SAML-enabled SDKs for native apps.
How does SAML improve security?
By centralizing authn, eliminating password storage on SPs, and supporting strong methods like MFA.
What’s the difference between SAML and LDAP?
LDAP is a directory protocol; SAML is for federated web authentication.
References
- Security Assertion Markup Language (SAML) V2.0 — OASIS. 2005-03-15. https://docs.oasis-open.org/security/saml/v2.0/saml-core-2.0-os.pdf
- What Is SAML (Security Assertion Markup Language)? — Microsoft. 2023-10-12. https://www.microsoft.com/en-us/security/business/security-101/what-is-security-assertion-markup-language-saml
- SAML 2.0 Technical Overview — OASIS. 2008-10-06. https://docs.oasis-open.org/security/saml/Post2.0/sstc-saml-tech-overview-2.0-cd-02.html
- Assertions and Protocols for the OASIS Security Assertion Markup Language (SAML) V2.0 — OASIS. 2005-03-15. https://docs.oasis-open.org/security/saml/v2.0/saml-assertions-2.0-os.pdf