
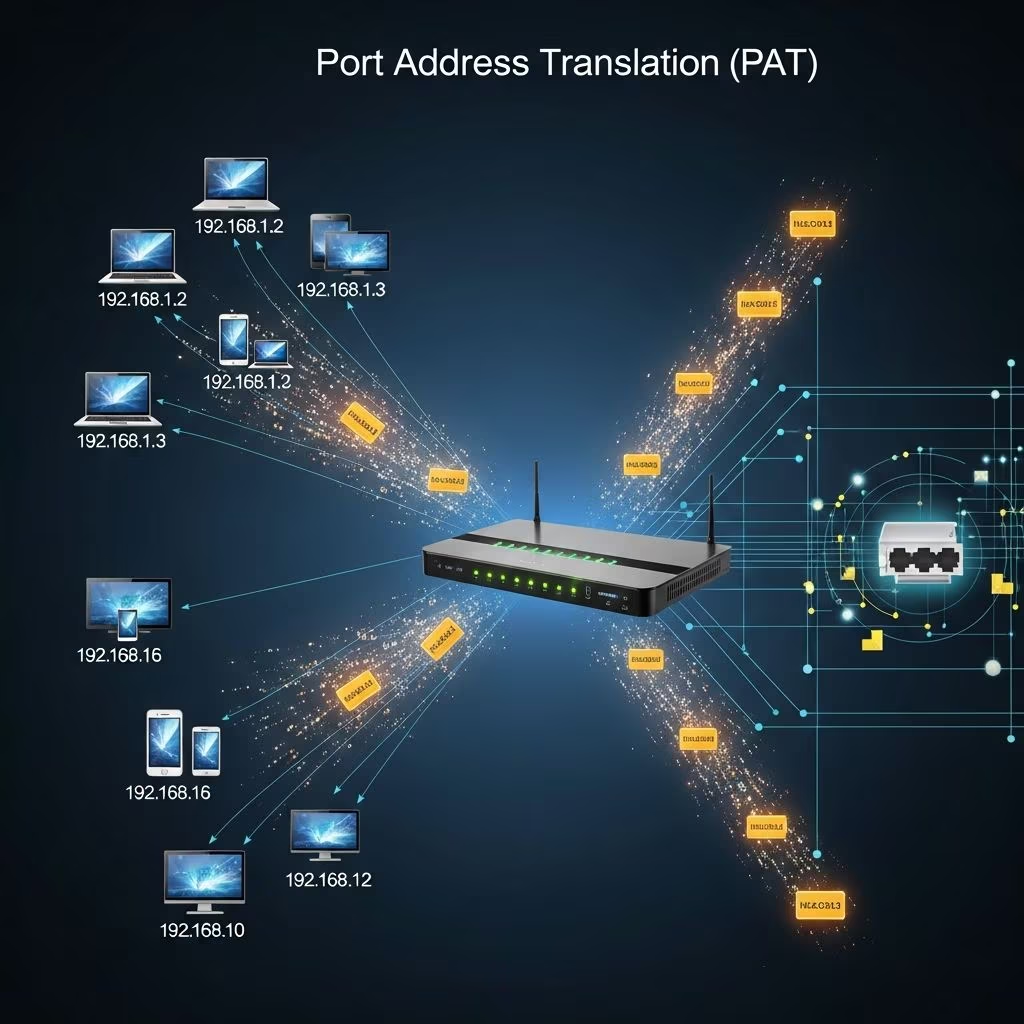
Port Address Translation, commonly known as PAT, stands as a cornerstone in contemporary network architecture. It empowers organizations and households to maximize limited public IP resources while maintaining seamless internet connectivity for numerous devices. By ingeniously combining IP addresses with port numbers, PAT ensures that internal traffic from private networks appears as originating from a solitary public endpoint externally. This mechanism not only addresses the scarcity of IPv4 addresses but also fortifies network defenses by obscuring internal structures from prying eyes.
The Evolution and Necessity of PAT in IP Networking
The internet’s growth has strained the finite pool of IPv4 addresses, prompting innovative solutions like Network Address Translation (NAT). PAT emerged as an advanced variant, often termed NAT overload, allowing a single public IP to service thousands of internal connections. Unlike basic NAT, which requires one-to-one mappings, PAT leverages the vast range of available ports—up to 65,536 per IP—to differentiate sessions.
Historically, as internet adoption surged in the late 1990s, routers began incorporating PAT to enable home users with dynamic IPs to connect multiple PCs. Today, it’s ubiquitous in broadband routers, enterprise firewalls, and cloud gateways, supporting the Internet of Things (IoT) explosion where dozens of smart devices demand outbound access.
Core Principles Behind PAT Functionality
At its heart, PAT operates at the network edge, typically on a router or firewall positioned between private LANs and the public WAN. When an internal device initiates a connection, the PAT device intercepts the packet, rewrites the source IP to its public address, and assigns a unique source port. This creates a bidirectional mapping stored in a dynamic translation table.
For incoming responses, the device consults this table: matching the destination port to the original internal host and port, it reverses the translation. This stateful process ensures sessions remain intact without manual configuration.
- Private IP Conservation: Internal networks use RFC 1918 ranges (e.g., 192.168.0.0/16), invisible externally.
- Port Multiplexing: TCP/UDP ports (1-65535) enable session distinction.
- Dynamic Allocation: Ports are assigned on-demand, released post-timeout (e.g., 24 hours for TCP).
Detailed Workflow of Outbound Traffic Handling
Consider a typical scenario: A laptop (192.168.1.10:50000) pings a remote server. The router receives the packet and performs these steps:
- Source Inspection: Note original source IP/port.
- Translation: Replace source with public IP (203.0.113.1) and ephemeral port (e.g., 60001).
- Table Entry: Log mapping: 192.168.1.10:50000 → 203.0.113.1:60001.
- Forwarding: Send to destination.
Simultaneously, a smartphone (192.168.1.20:50000) connects to the same server. It gets 203.0.113.1:60002, preventing collision. The table now holds multiple entries under one public IP.
| Internal IP:Port | Public IP:Port | Protocol | Timeout |
|---|---|---|---|
| 192.168.1.10:50000 | 203.0.113.1:60001 | TCP | 86400s |
| 192.168.1.20:50000 | 203.0.113.1:60002 | UDP | 300s |
| 192.168.1.30:8080 | 203.0.113.1:60003 | TCP | 3600s |
Managing Inbound Responses with Precision
Reverse translation is equally critical. When the server replies to 203.0.113.1:60001, the router:
- Destination Match: Scans table for matching public port.
- Reverse Map: Swap destination to 192.168.1.10:50000.
- Validate State: Ensure session is active; drop stale packets.
- Deliver: Route internally.
This symmetry maintains end-to-end illusion for applications, though it breaks true peer-to-peer without port forwarding.
Distinguishing PAT from Other NAT Variants
PAT is one tool in the NAT arsenal:
- Static NAT: Fixed one-to-one mapping for servers needing inbound access.
- Dynamic NAT: Pool-based one-to-one, less scalable than PAT.
- Overloaded PAT: Many-to-one (standard PAT), ideal for LANs.
PAT shines in scalability: one IP supports ~65k sessions theoretically, though practical limits hover at 32k-50k due to hardware.
Configuration Essentials on Cisco Routers
Implementing PAT on Cisco IOS involves defining interfaces and access lists. Basic commands:
ip nat inside source list 1 interface GigabitEthernet0/0 overloadaccess-list 1 permit 192.168.1.0 0.0.0.255interface GigabitEthernet0/0 ip nat outsideinterface GigabitEthernet0/1 ip nat insideThe ‘overload’ keyword activates PAT. Verify with show ip nat translations, revealing the port-mapped table.
For enterprises, integrate with ACLs for selective translation and route-maps for policy-based routing.
Security Implications and Best Practices
PAT inherently enhances security by hiding internal IPs, blocking unsolicited inbound unless port-forwarded. However:
- Port Scanning Resistance: External probes see one IP, but open ports risk exploits.
- Application Layer Gateways (ALGs): Needed for FTP, SIP to rewrite embedded IPs/ports.
- DoS Mitigation: Limit concurrent sessions per host.
Combine with firewalls: zone-based policies on Cisco or stateful inspection.
Advantages Driving PAT Adoption
- IP Conservation: Vital amid IPv4 exhaustion; delays IPv6 full transition.
- Cost Savings: Single static IP suffices for entire subnets.
- Simplified Management: No per-device public IPs.
- Flexibility: Supports dynamic ISP IPs seamlessly.
Potential Drawbacks and Mitigation Strategies
No solution is flawless:
- Port Exhaustion: Heavy usage (e.g., torrents) depletes ports; monitor with SNMP.
- Performance Overhead: Translation tables strain CPU; use hardware-accelerated NAT.
- Debugging Challenges: Tools like Wireshark aid, but logs are essential.
- IPv6 Compatibility: Dual-stack with NPTv6.
PAT in Modern Environments: Cloud and Beyond
In AWS, Azure, PAT underlies Network Address Translation Load Balancers. SD-WAN solutions embed PAT for branch offices. With IPv6, PAT remains relevant for hybrid transitions.
Frequently Asked Questions (FAQs)
What is the primary role of PAT?
PAT enables multiple private devices to share one public IP by mapping unique ports to each connection.
Does PAT support both TCP and UDP?
Yes, PAT works with TCP, UDP, and ICMP, using protocol-specific port handling.
How many connections can one PAT IP handle?
Theoretically 65,536, limited practically by device resources.
Is PAT the same as NAT?
PAT is a form of NAT overload, distinguishing it from one-to-one mappings.
Can PAT handle inbound connections?
Only with static port forwarding; pure PAT is outbound-initiated.
References
- RFC 2663 – IP Network Address Translator (NAT) Terminology and Considerations — IETF. 1999-08. https://datatracker.ietf.org/doc/html/rfc2663
- Cisco IOS Network Address Translation Configuration Guide — Cisco Systems. 2024-03-15. https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/ipaddr_nat/configuration/xe-16/nat-xe-16-book/iadnat-addr-consv.html
- Port Address Translation (PAT) configuration — Study CCNA. 2023-11. https://study-ccna.com/port-address-translation-pat-configuration/