
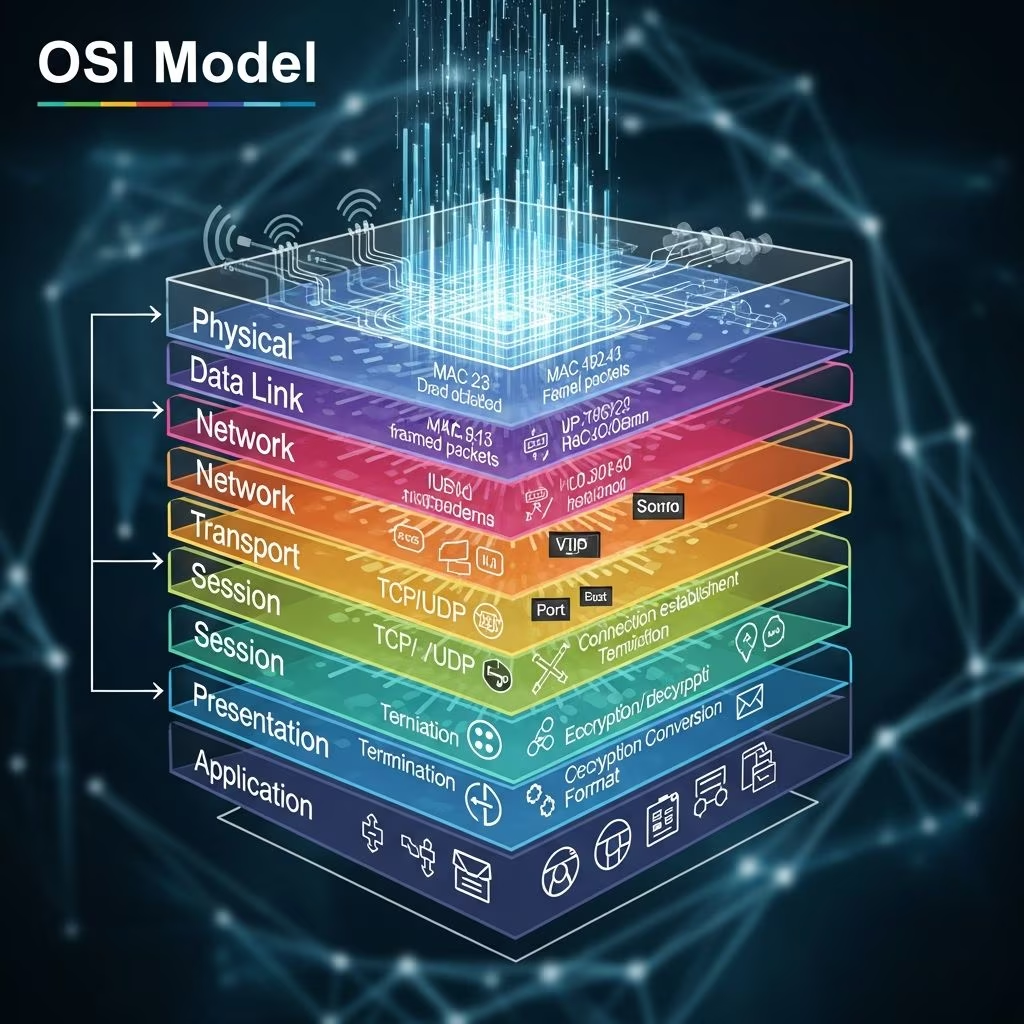
The Open Systems Interconnection (OSI) model serves as a universal blueprint for how devices exchange data across networks. Developed by the International Organization for Standardization (ISO) in the late 1970s, this framework divides complex networking processes into seven distinct layers. Each layer performs specialized tasks, ensuring interoperability between diverse hardware and software systems. Whether you’re troubleshooting connectivity issues or designing secure networks, understanding the OSI model is indispensable.
At its core, the OSI model promotes modularity. Changes in one layer rarely disrupt others, fostering innovation and standardization. For instance, the evolution of wireless technologies primarily impacts lower layers without altering upper-layer applications. This article delves into each layer’s responsibilities, data flow mechanics, practical uses, and its relevance in today’s threat landscape, including distributed denial-of-service (DDoS) defenses.
Historical Development and Core Principles
The OSI model’s origins trace back to efforts by the ISO to create a reference for open networking standards. Published as ISO/IEC 7498-1 in 1984, with updates through 1994, it emerged amid the shift from proprietary networks to interconnected systems. Unlike the simpler TCP/IP model used in the internet, OSI’s seven layers offer granular detail for education, diagnostics, and protocol design.
Key principles include abstraction, where each layer hides complexities from adjacent ones; peer-to-peer communication, enabling direct layer-to-layer dialogue across devices; and encapsulation, where data gains headers (or trailers) as it descends layers. On the receiving end, headers are stripped progressively. This structured approach simplifies everything from email delivery to video streaming.
Today, the model remains relevant despite TCP/IP dominance. Network engineers use it to pinpoint failures—e.g., a Layer 1 issue signals cable problems, while Layer 7 points to application bugs. In cybersecurity, it maps attack vectors: volumetric DDoS floods Layer 3, while sophisticated bots mimic Layer 7 traffic.
Layer 1: Physical Layer Fundamentals
The bottommost layer handles raw bit transmission over physical media like copper cables, fiber optics, or radio waves. It defines electrical, mechanical, and procedural specs: voltage levels, connector types (e.g., RJ-45), and signal timing.
Key functions include:
- Bit synchronization and encoding/decoding.
- Physical topology setup (star, bus, ring).
- Signal modulation for media like Ethernet or Wi-Fi.
Without Layer 1 stability, higher layers fail. Common issues: faulty cables causing bit errors or electromagnetic interference disrupting signals. Protocols aren’t defined here; it’s purely hardware-oriented. Examples include RS-232 serial standards and 10BASE-T Ethernet physical specs.
In practice, tools like cable testers operate at this layer. For security, physical access controls prevent tampering, as attackers could inject malicious signals.
Layer 2: Data Link Layer Operations
Building on physical transmission, Layer 2 ensures error-free data transfer between directly connected nodes. It frames bits into structured packets, adding MAC addresses for local delivery.
Sub-layers: Logical Link Control (LLC) for flow/error control, and Media Access Control (MAC) for addressing and access arbitration. Protocols like Ethernet, PPP, and Wi-Fi (802.11) dominate.
Core tasks:
| Function | Description |
|---|---|
| Framing | Encapsulates data with headers/trailers, including CRC for error detection. |
| Addressing | Uses 48-bit MAC addresses for device identification on local networks. |
| Switching | Bridges and switches forward frames based on MAC tables. |
Layer 2 attacks include MAC flooding (exhausting switch tables) and ARP spoofing. VLANs and port security mitigate these.
Layer 3: Network Layer Routing Essentials
Layer 3 enables inter-network communication via logical addressing (IP addresses) and routing. It breaks data into packets, determining optimal paths across routers.
Protocols: IP (IPv4/IPv6), ICMP, OSPF, BGP. Unlike Layer 2’s hop-by-hop delivery, Layer 3 provides end-to-end routing.
- Path determination using routing tables and algorithms.
- Fragmentation/reassembly for varying MTU sizes.
- Packet forwarding with TTL to prevent loops.
DDoS often targets Layer 3 with floods (e.g., UDP floods overwhelming IP capacity). Firewalls and BGP blackholing counter this. IPv6 adoption enhances addressing but introduces new security considerations like extension headers.
Layer 4: Transport Layer Reliability
This layer ensures complete data delivery between hosts, segmenting upper-layer data and managing reliability. TCP provides connection-oriented, reliable service with sequencing, acknowledgments, and congestion control. UDP offers connectionless, low-overhead transmission for real-time apps like VoIP.
Port numbers identify applications (e.g., 80 for HTTP). Functions include multiplexing/demultiplexing, flow control, and error recovery.
Layer 4 threats: SYN floods exhaust TCP handshakes. Mitigation: SYN cookies and rate limiting.
Layer 5: Session Layer Management
Layer 5 establishes, maintains, and terminates sessions—logical connections between apps. It handles dialog control (simplex, half/full duplex), synchronization (checkpoints for recovery), and token management.
Protocols: NetBIOS, RPC. Example: Resuming a large file transfer after interruption via checkpoints, avoiding full restarts. Session hijacking exploits weak authentication here.
Layer 6: Presentation Layer Translation
Layer 6 translates data formats between network and applications: encryption (SSL/TLS), compression (gzip), and syntax translation (ASCII to EBCDIC). It ensures endianness compatibility and JPEG/MPEG handling.
Security role: Offloads crypto from apps. Attacks target weak implementations, like unencrypted data exposure.
Layer 7: Application Layer Interaction
The top layer interfaces with end-user software (browsers, email clients), providing network services via protocols like HTTP, SMTP, DNS, FTP. It doesn’t include apps themselves but enables their data exchange.
Layer 7 DDoS (e.g., HTTP floods) mimics legitimate traffic, evading basic filters. WAFs inspect payloads here.
Data Encapsulation and Decapsulation Process
Sending: Application data → Presentation (encrypt/compress) → Session (sync) → Transport (segments) → Network (packets) → Data Link (frames) → Physical (bits).
Receiving: Reverse, stripping headers upward.
This PDUs (Protocol Data Units) evolve: data → segment → packet → frame → bit.
OSI vs. TCP/IP: Key Comparisons
OSI’s 7 layers vs. TCP/IP’s 4 (Link, Internet, Transport, Application). OSI is theoretical; TCP/IP practical. Mapping: OSI 5-7 ≈ TCP/IP Application; OSI 3 ≈ Internet; OSI 1-2 ≈ Link.
Practical Applications and Troubleshooting
Use OSI for diagnostics: Ping tests Layer 3; Wireshark captures multi-layer traffic. In cloud, services like AWS VPC align with layers.
Cybersecurity: CDN like Cloudflare protect per layer—DDoS scrubbing at 3/4, WAF at 7.
FAQs
What is the OSI model used for?
It standardizes networking, aids troubleshooting, and informs protocol design.
How do DDoS attacks relate to OSI layers?
Volumetric hit 3/4; app-layer target 7.
Is OSI still relevant?
Yes, for education and granular analysis despite TCP/IP prevalence.
Difference between TCP and IP layers?
TCP (Layer 4) ensures reliability; IP (Layer 3) routes.
References
- Information technology — Open Systems Interconnection — Basic Reference Model: The Basic Model — International Organization for Standardization (ISO). 1994-11-15. https://www.iso.org/standard/20269.html
- OSI Model — National Institute of Standards and Technology (NIST). 2023-08-01. https://nvlpubs.nist.gov/nistpubs/SpecialPublications/NIST.SP.800-53r5.pdf
- RFC 1122: Requirements for Internet Hosts — Communication Layers — Internet Engineering Task Force (IETF). 1989-10-01. https://datatracker.ietf.org/doc/html/rfc1122
- Understanding the OSI Model — Cisco Networking Academy. 2024-02-20. https://www.netacad.com/courses/networking/osi-model
- DDoS Attack Trends — Cloudflare. 2025-01-15. https://www.cloudflare.com/learning/ddos/ddos-attack-trends/