
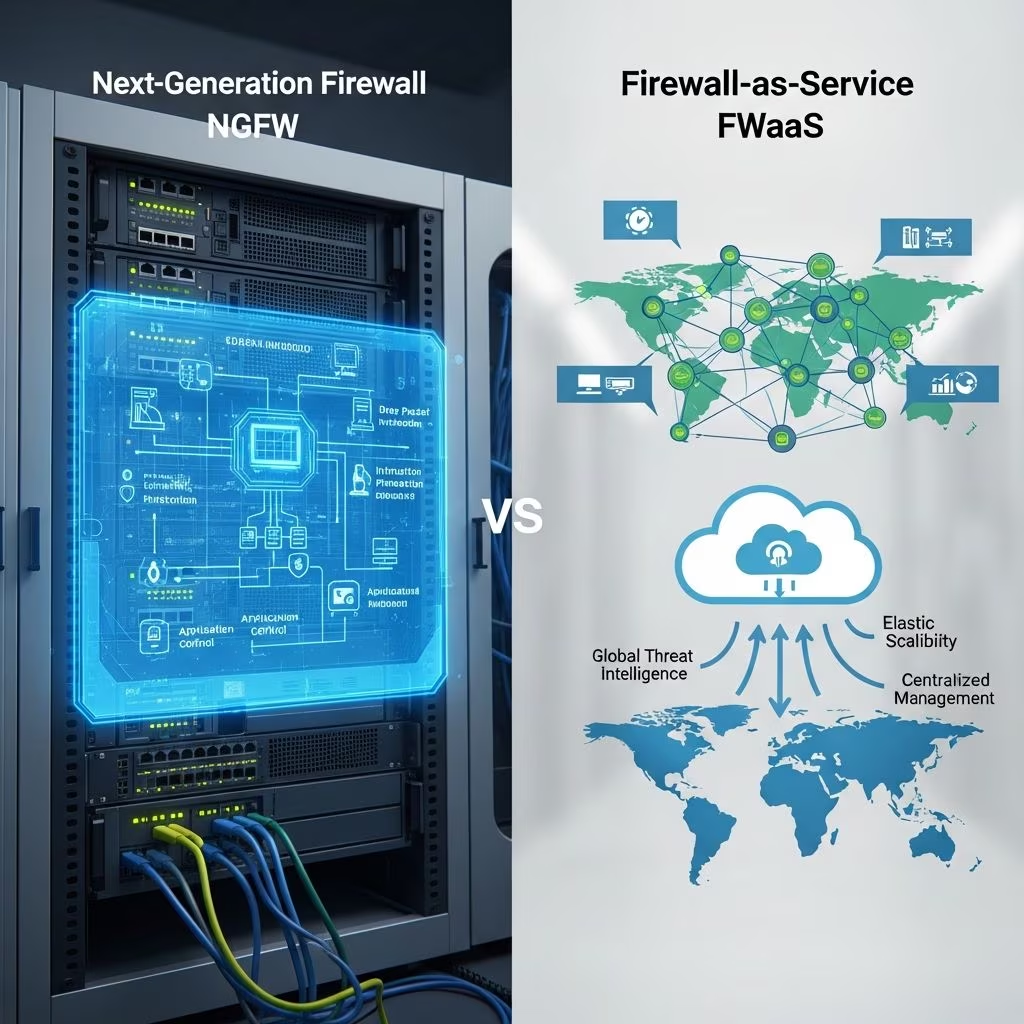
In the evolving landscape of cybersecurity, organizations face critical decisions about firewall technologies. Next-Generation Firewalls (NGFW) and Firewall-as-a-Service (FWaaS) represent two prominent approaches to network protection. While both aim to safeguard digital assets, they differ fundamentally in deployment, operation, and suitability for various environments. This article delves into their distinctions, helping IT leaders make informed choices for robust defense strategies.
Understanding Next-Generation Firewalls
Next-Generation Firewalls build on traditional firewall foundations by incorporating advanced threat detection and prevention mechanisms. Unlike basic firewalls that merely inspect packet headers, NGFWs delve deeper into traffic flows. They employ deep packet inspection (DPI) to analyze application-layer data, identify malicious payloads, and enforce granular policies based on user identity, content, and behavior.
Key capabilities include:
- Application Awareness: Recognizing and controlling over thousands of applications, regardless of port or protocol obfuscation.
- IPS Integration: Inline intrusion prevention systems that block exploits in real-time.
- URL Filtering and Antivirus: Protecting against web-based threats and malware downloads.
- User Identity Mapping: Linking traffic to specific users via integration with directory services like Active Directory.
These features make NGFWs indispensable for environments requiring precise control over complex traffic patterns. According to NIST guidelines on network security, such advanced inspection is vital for defending against sophisticated attacks.1
Exploring Firewall-as-a-Service
Firewall-as-a-Service shifts the firewall paradigm to the cloud, delivering protection as a subscription-based offering. FWaaS providers host the firewall infrastructure in their global data centers, routing customer traffic through these points for inspection and policy enforcement. This model eliminates the need for on-site hardware, leveraging cloud elasticity for seamless scaling.
Core elements of FWaaS encompass:
- Cloud-Native Delivery: Traffic is steered to provider PoPs (Points of Presence) via secure tunnels or DNS redirection.
- Centralized Management: Intuitive dashboards for policy configuration, accessible from anywhere.
- Automatic Updates: Vendors handle signature updates, OS patches, and feature rollouts without customer intervention.
- Global Reach: Low-latency enforcement through anycast networks spanning multiple continents.
FWaaS aligns perfectly with Secure Access Service Edge (SASE) architectures, integrating firewalling with SD-WAN, ZTNA, and CASB for comprehensive edge security.
Deployment Models Compared
The most stark contrast lies in how these solutions are implemented. NGFWs traditionally deploy as physical appliances in data centers or branch offices, requiring rack space, power, and cooling. Virtual NGFW instances can run on hypervisors or public clouds, but customers retain management responsibilities.
| Aspect | NGFW | FWaaS |
|---|---|---|
| Hardware Needs | Physical/virtual appliances on customer premises or IaaS | No hardware; fully cloud-hosted |
| Setup Time | Weeks for procurement, installation, cabling | Hours via API or portal configuration |
| Traffic Routing | In-line or out-of-path at perimeter | Cloud breakout from edge locations |
| High Availability | Customer-managed clustering/failover | Provider-managed geo-redundancy |
FWaaS simplifies deployment for distributed workforces, while NGFWs excel in controlled, localized environments.
Management and Operational Overhead
NGFW management demands skilled personnel for tuning policies, monitoring logs, and troubleshooting hardware issues. Organizations must maintain 24/7 teams or service contracts for uptime. In contrast, FWaaS offloads these burdens to the provider, who employs specialized Security Operations Centers (SOCs).
Benefits of FWaaS management include:
- Reduced staffing needs by up to 70%, per industry benchmarks.
- Consistent policy enforcement across global sites.
- Proactive threat hunting by vendor experts.
For teams lacking deep firewall expertise, FWaaS accelerates time-to-security without extensive training investments.
Scalability and Performance Considerations
Scalability defines another battleground. NGFWs scale vertically by upgrading appliances or horizontally via additional units, incurring costs and complexity. FWaaS scales effortlessly—providers auto-provision resources during spikes, such as DDoS attacks or seasonal traffic surges.
Performance-wise, on-premises NGFWs offer sub-millisecond latency for local traffic but struggle with encrypted flows taxing CPU resources. FWaaS, optimized by global Anycast, maintains consistent performance worldwide, though hairpinning traffic to cloud PoPs can introduce minor delays for certain workloads.
In benchmarks from Gartner, cloud firewalls demonstrate 99.999% uptime and elastic throughput exceeding 100 Gbps per PoP.2
Cost Structures Analyzed
Financial models diverge significantly. NGFWs follow a CapEx model: upfront hardware purchases (often $50K+ per unit), plus recurring OpEx for licenses, support, and electricity. Total cost of ownership (TCO) over five years can exceed initial investments threefold due to maintenance.
FWaaS adopts pure OpEx via predictable subscriptions ($5-20/user/month), factoring in throughput tiers and advanced modules. No forklift upgrades or disposal costs—pay only for consumed capacity. For growing enterprises, FWaaS TCO drops 40-60% versus perpetual NGFW licenses, according to Forrester research.3
When to Deploy NGFW Solutions
Opt for NGFW in these scenarios:
- Legacy On-Premises Dominance: Heavy investments in physical data centers with stable topologies.
- Latency-Sensitive Applications: High-frequency trading, VoIP, or industrial control systems demanding microsecond responses.
- Regulatory Mandates: Data sovereignty laws requiring inspection within national borders (e.g., GDPR, HIPAA).
- Customization Depth: Bespoke policies for proprietary protocols or air-gapped segments.
NGFWs shine where absolute control trumps convenience.
Ideal Use Cases for FWaaS
FWaaS thrives when:
- Cloud Migration Accelerates: Protecting SaaS, IaaS, and PaaS workloads without perimeter rearchitecture.
- Remote/Hybrid Workforce: Securing thousands of distributed users via clientless access.
- Rapid Scaling Demands: Startups or seasonal businesses needing instant capacity.
- SASE Convergence: Integrating firewall with SWG, ZTNA, and DLP for unified security.
Modern enterprises increasingly favor FWaaS for its agility in dynamic ecosystems.
Hybrid Approaches and Future Trends
Pure either/or choices fade; hybrid models prevail. Use NGFWs for core data centers and FWaaS for branches/cloud egress. Emerging trends include AI-driven anomaly detection in both, zero-trust segmentation, and 5G edge computing integration. By 2027, IDC predicts 70% of enterprises will blend on-prem and cloud firewalls.4
Frequently Asked Questions
Can FWaaS replace NGFW entirely?
Not always—FWaaS suits cloud-first setups, but regulated on-prem environments may require NGFW persistence.
Is FWaaS secure for high-throughput needs?
Yes, leading providers deliver terabit-scale capacity with carrier-grade SLAs.
How does latency compare?
NGFW wins locally; FWaaS via optimized global networks minimizes WAN impact.
What about costs for large enterprises?
FWaaS often proves cheaper long-term due to OpEx predictability and no hardware refresh cycles.
Does NGFW work in the cloud?
Virtual NGFWs deploy on AWS, Azure, but customers manage scaling and updates.
References
- Guide to Intrusion Detection and Prevention Systems (IDPS) — NIST Special Publication 800-94. 2007-02 (authoritative standard, remains foundational). https://nvlpubs.nist.gov/nistpubs/Legacy/SP/nistspecialpublication800-94.pdf
- Magic Quadrant for Network Firewalls — Gartner. 2023-10-04. https://www.gartner.com/en/documents/4022346
- The Total Economic Impact of Palo Alto Networks Prisma Access — Forrester. 2024-06-12. https://www.paloaltonetworks.com/resources/research/total-economic-impact-prisma-access
- Worldwide Secure Web Gateway Forecast, 2023–2027 — IDC. 2024-03. https://www.idc.com/getdoc.jsp?containerId=US51347524
- What Is Firewall as a Service? — Palo Alto Networks. 2025-01-15. https://www.paloaltonetworks.com/cyberpedia/what-is-firewall-as-a-service