
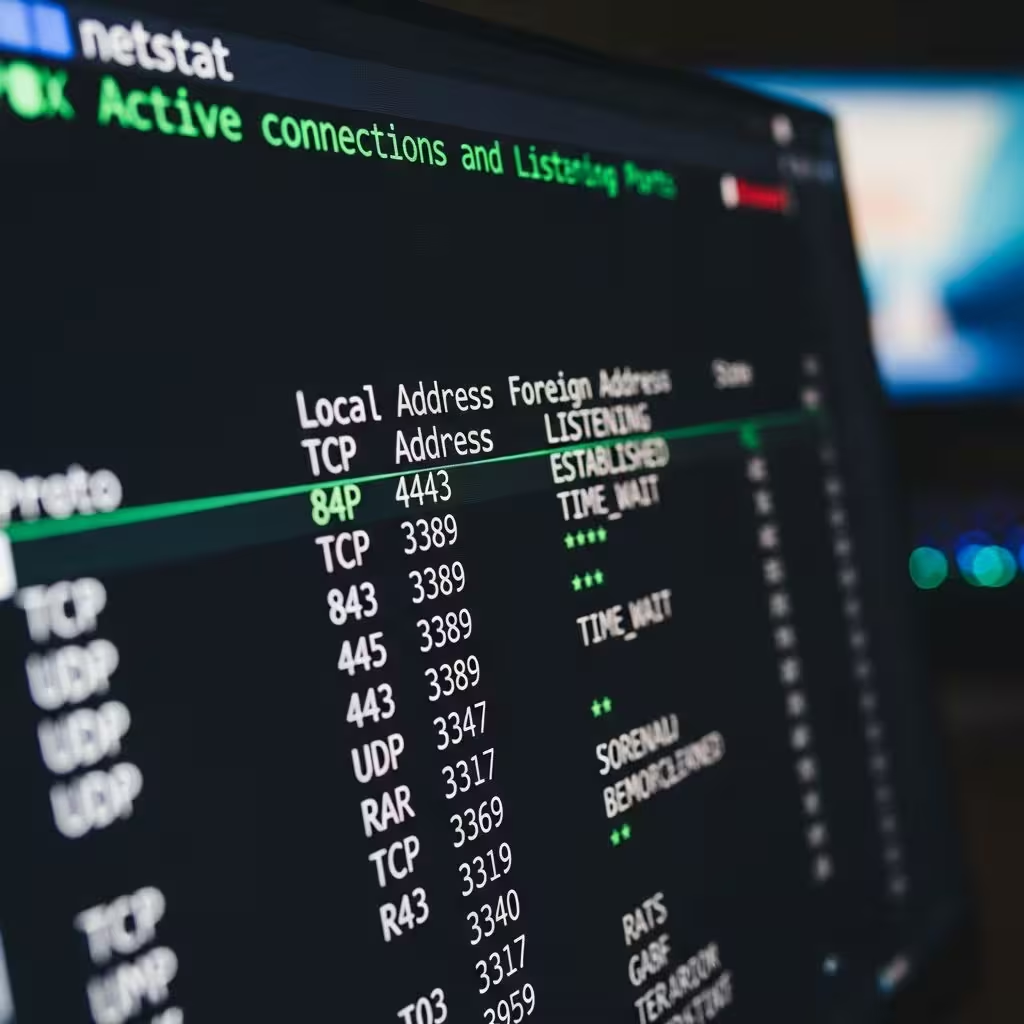
Network administrators and security professionals rely on quick, reliable methods to assess the status of ports on Windows machines. Built-in tools like netstat provide a powerful way to inspect TCP and UDP endpoints without needing third-party software. This approach allows for focused analysis of active connections and listening services, helping to pinpoint potential security risks efficiently.
Understanding Network Ports and Their Role in System Security
Ports serve as virtual endpoints for communication in TCP/IP networks, enabling applications to send and receive data. Windows systems typically manage thousands of possible ports, but only a subset are actively used at any time. TCP ports handle reliable, connection-oriented traffic, while UDP ports support faster, connectionless exchanges. Knowing which ports are open or listening is crucial for maintaining a secure posture, as exposed services can become entry points for unauthorized access.
Regular port inspections help detect unintended exposures, such as services left running unnecessarily or misconfigurations that leave firewalls bypassed. By focusing on actual usage rather than scanning all 65,535 ports, administrators save time and reduce false positives common in broad scans.
Getting Started with Netstat: Core Command Syntax
The netstat utility, short for network statistics, is pre-installed on all modern Windows versions, from Windows 10 to Server 2022. To launch it, open Command Prompt or PowerShell as an administrator for full visibility into system-wide connections.
The basic syntax is straightforward: netstat [options]. Key flags include:
- -a: Displays all connections and listening ports.
- -n: Shows addresses and port numbers numerically, avoiding DNS lookups for speed.
- -p: Filters by protocol (TCP or UDP).
- -b: Reveals executable files associated with connections (requires admin rights).
- -o: Includes process IDs for further investigation.
Combining these, netstat -an generates a concise list of all relevant port activity, making it ideal for initial assessments.
Interpreting Netstat Output: A Step-by-Step Guide
Running netstat -an produces a tabular output with columns for Protocol, Local Address, Foreign Address, and State. Here’s a sample from a typical workstation:
Proto Local Address Foreign Address StateTCP 0.0.0.0:135 0.0.0.0:0 LISTENINGTCP 0.0.0.0:445 0.0.0.0:0 LISTENINGTCP 127.0.0.1:8080 0.0.0.0:0 LISTENINGUDP 0.0.0.0:123 *:* UDP 172.16.1.100:137 *:*Key elements to analyze:
- Proto: TCP for established links, UDP for datagram services.
- Local Address: IP:port combinations, where 0.0.0.0 indicates listening on all interfaces, and 127.0.0.1 limits to loopback.
- Foreign Address: Remote endpoints; 0.0.0.0:0 for listeners.
- State: LISTENING (accepting connections), ESTABLISHED (active session), TIME_WAIT (closing).
Focus on LISTENING ports exposed beyond loopback (not 127.0.0.1), as these are visible externally and warrant scrutiny.
Common Ports to Watch on Windows Systems
Windows defaults expose several standard ports. Here’s a table of frequently seen ones:
| Port | Protocol | Service | Risk Level |
|---|---|---|---|
| 135 | TCP | RPC Endpoint Mapper | High |
| 139/445 | TCP | SMB File Sharing | Medium-High |
| 3389 | TCP | Remote Desktop (RDP) | High if exposed |
| 53 | UDP | DNS | Low-Medium |
| 123 | UDP | NTP Time Sync | Low |
Ports like 135 and 445 have been exploited in major attacks (e.g., EternalBlue for WannaCry), so disabling unnecessary services via Windows Features or firewall rules is recommended.
Advanced Netstat Techniques for Deeper Insights
Enhance your analysis with additional flags. Use netstat -anob to link ports to processes:
TCP 0.0.0.0:8080 0.0.0.0:0 LISTENING [svchost.exe]This reveals if a web server or malware is bound to a port. For ongoing monitoring, pipe output to find: netstat -an | find "LISTENING".
Track changes over time by scripting: Create a batch file to log netstat output periodically and diff against baselines, alerting on new listeners.
Integrating Netstat with Windows Firewall and Defender
Netstat complements Windows Defender Firewall. After identifying open ports, verify rules:
- Run
netsh advfirewall firewall show rule name=allto list rules. - Block unwanted ports:
netsh advfirewall firewall add rule name="Block Port 135" dir=in action=block protocol=TCP localport=135.
For automated security, use PowerShell: Get-NetTCPConnection | Where-Object {$_.State -eq 'Listen'} | Select LocalAddress, LocalPort, OwningProcess. This provides structured data for scripting defenses.
External Validation: Testing Port Exposure
Netstat shows internal status, but external reachability matters most. Use online tools or local scanners:
- List ports from netstat.
- Test via telnet:
telnet your.public.ip port(install telnet if needed). - Employ external services like Gibson Research ShieldsUP for quick probes on listed ports.
Avoid full-range scans; target only netstat-identified ports to confirm firewall efficacy and ISP blocking.
Limitations of Netstat and Modern Alternatives
While versatile, netstat has drawbacks: it misses rootkit-hidden connections and doesn’t scan remotely. For comprehensive needs:
- PowerShell Get-NetTCPConnection: Native, object-oriented replacement.
- Nmap: Cross-platform for remote scanning (official docs at nmap.org).
- CurrPorts: GUI tool for real-time monitoring.
Transition to PowerShell for enterprise environments, as it’s more scriptable and integrated with Active Directory.
Best Practices for Routine Port Auditing
Implement these habits:
- Run netstat weekly on critical servers.
- Baseline clean states post-patching.
- Automate with Task Scheduler:
schtasks /create /tn "PortAudit" /tr "netstat -an > C:\logs\ports.txt" /sc weekly. - Correlate with event logs for anomalies.
Combine with vulnerability scanners like Microsoft Baseline Security Analyzer for holistic checks.
Frequently Asked Questions (FAQs)
What does LISTENING mean in netstat?
It indicates a service waiting for incoming connections on that port.
How do I close an unwanted listening port?
Stop the associated service via services.msc or taskkill /pid <processid>.
Is netstat safe to run on production systems?
Yes, it’s read-only and lightweight, with negligible performance impact.
Can netstat detect malware?
Indirectly, by spotting unexpected listeners; pair with antivirus scans.
Netstat vs. Nmap: When to use each?
Netstat for local introspection; Nmap for remote network mapping.
Conclusion: Empower Your Security Workflow
Mastering netstat transforms routine maintenance into proactive defense. By regularly auditing ports, validating exposures, and automating checks, Windows admins can fortify their networks against common threats. Integrate these techniques into your toolkit for sustained vigilance.
References
- Microsoft Docs: netstat — Microsoft Corporation. 2024-03-15. https://learn.microsoft.com/en-us/windows-server/administration/windows-commands/netstat
- Nmap Network Scanning: Port Scanning Basics — Nmap Project. 2023-11-01. https://nmap.org/book/port-scanning-basics.html
- Windows Firewall with Advanced Security — Microsoft Corporation. 2025-01-20. https://learn.microsoft.com/en-us/windows/security/threat-protection/windows-firewall/windows-firewall-with-advanced-security
- PowerShell: Get-NetTCPConnection — Microsoft Corporation. 2024-06-10. https://learn.microsoft.com/en-us/powershell/module/nettcpip/get-nettcpconnection
- ShieldsUP! Port Testing Service — Gibson Research Corporation. 2023-05-05. https://www.grc.com/x/ne.dll?bh0bkyd2