
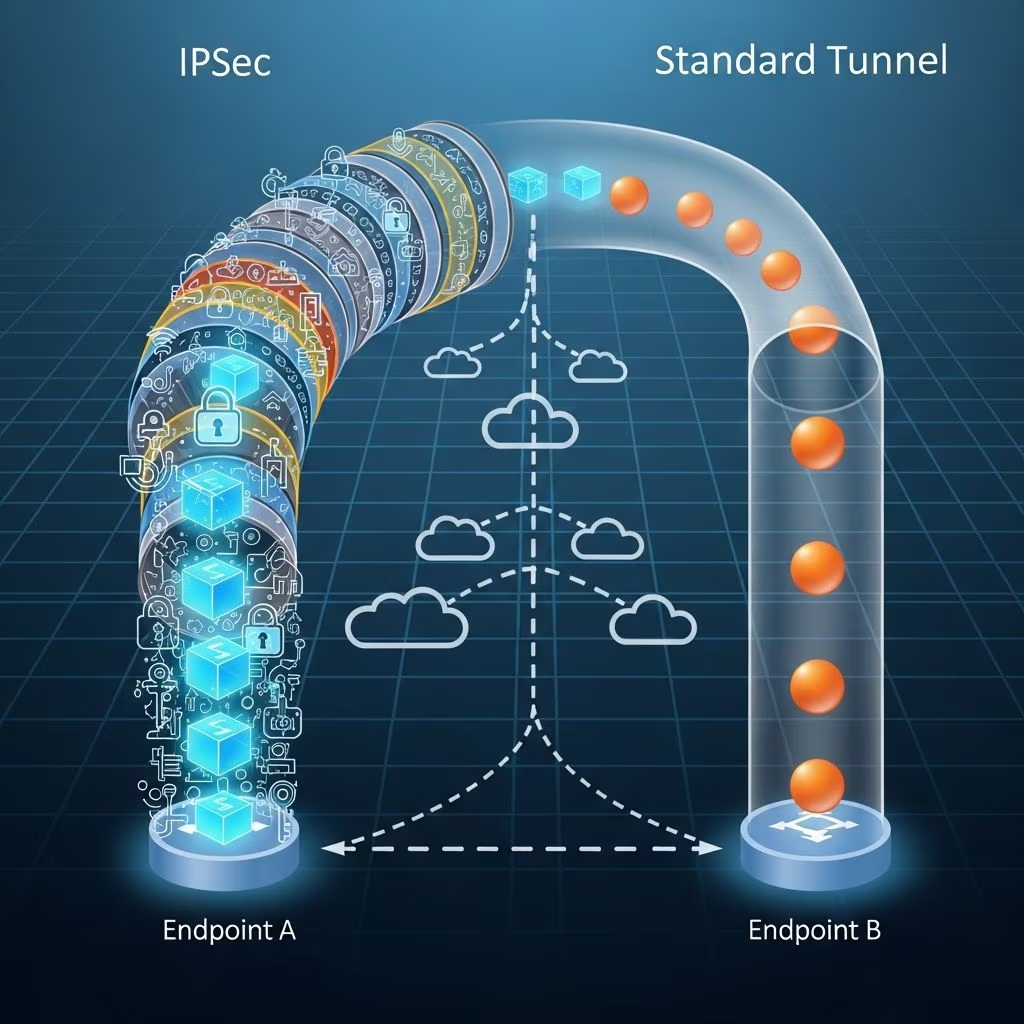
In the realm of modern networking, tunnels serve as vital conduits for routing traffic across disparate networks securely and efficiently. While basic tunnels focus on encapsulation and transport, IPsec tunnels introduce a layer of cryptographic protection that transforms them into robust VPN solutions. This article delves into their distinctions, operational mechanics, performance considerations, and practical implications for bandwidth utilization.
Understanding Network Tunneling Fundamentals
Tunneling is a technique where one network protocol encapsulates another, allowing data packets to traverse untrusted or incompatible networks. Imagine sending a letter inside another envelope: the outer envelope gets the package to the destination, while the inner one ensures the contents reach the final recipient intact.
Standard tunnels, such as those using IP-in-IP or Generic Routing Encapsulation (GRE), prioritize simplicity and transparency. They wrap the original IP packet within a new outer IP header, enabling routers along the path to forward based solely on the exterior details. Upon arrival at the tunnel endpoint, the outer layer is removed, and the inner packet proceeds normally. This method excels in scenarios requiring topology-agnostic transport, like connecting remote branches over the public internet without altering underlying routing.
- Key Benefits of Standard Tunnels: Low processing overhead, broad compatibility, and ease of setup.
- Common Use Cases: Legacy migrations, multicast support via GRE, or basic site-to-site connectivity.
However, these tunnels lack inherent security, exposing inner payloads to interception, tampering, or eavesdropping en route.
IPsec Tunnels: Security-First Encapsulation
IPsec (Internet Protocol Security) elevates tunneling by integrating authentication, integrity checks, and encryption. Defined in RFC 4301 by the IETF, IPsec operates in two primary phases: IKE (Internet Key Exchange) for key negotiation and IPsec protocols (AH for authentication, ESP for encryption and authentication) for data protection.
Unlike plain tunnels, IPsec in tunnel mode fully encapsulates the original IP packet, adding outer headers plus security payloads. This creates a protected channel ideal for VPNs. Transport mode, conversely, secures only the payload and upper layers, leaving original IP headers exposed—less common for site-to-site VPNs.
| Mode | Encryption Scope | Header Protection | Typical Application |
|---|---|---|---|
| Tunnel | Entire original packet | Full (new outer IP) | Site-to-site VPNs |
| Transport | Payload only | Partial (original IP intact) | Host-to-host security |
ESP is the workhorse protocol, combining confidentiality (via AES or similar ciphers) with optional authentication. AH focuses solely on integrity but is rarely used due to NAT traversal issues.
Core Differences: Security, Overhead, and Flexibility
The divergence between IPsec and standard tunnels boils down to protection versus performance trade-offs.
- Security Posture: Standard tunnels offer none; IPsec mandates it through mutual authentication and replay protection.
- Overhead: Basic tunnels add ~20 bytes (IP header); IPsec piles on 40-60+ bytes for ESP headers, IV, trailer, and outer IP.
- Configuration Complexity: Plain tunnels need minimal setup; IPsec demands key management, policy definitions, and cipher suites.
- NAT Handling: Both support it, but IPsec uses UDP encapsulation (NAT-T) for seamless traversal.
In essence, choose standard for speed in trusted environments; opt for IPsec where data sensitivity demands defense-in-depth.
Bandwidth Dynamics in Tunneling Environments
Tunnel bandwidth isn’t fixed—it’s dictated by the underlying link, protocol overhead, hardware capabilities, and management policies. No tunnel inherently “owns” bandwidth; all compete for the physical interface’s capacity.
Without QoS (Quality of Service), tunnels operate on a first-come, first-served basis, leading to contention during bursts. Aggregate throughput caps at the link speed, minus encapsulation penalties.
Overhead Breakdown and Efficiency Metrics
IPsec introduces measurable bandwidth tax. For AES-encrypted ESP in tunnel mode with a 1460-byte TCP payload (common MSS), overhead approximates 9.32%, yielding 91.48% efficiency. Calculations include:
- 20 bytes outer IP header
- 8 bytes ESP header (SPI, sequence)
- 16 bytes IV (AES-GCM)
- 16 bytes trailer (padding, auth data)
- Total addition: ~136 bytes on 1460 payload
Layer this with TCP/IP (4-5% hit) and Ethernet framing (~3%), and a 100 Mbps link delivers ~87-88 Mbps effective throughput under ideal conditions.
Hardware and Crypto Acceleration Impacts
CPU-intensive encryption throttles performance on low-end devices. Older hardware might cap IPsec at 4-10 Mbps; modern firewalls with AES-NI instructions or dedicated ASICs exceed 1 Gbps per tunnel. Oracle Cloud reports typical IPSec tunnels hitting 250+ Mbps, bounded by ISP limits.
Bandwidth Management Strategies for Tunnels
Advanced firewalls (e.g., Palo Alto, Fortinet) offer granular controls decoupled from tunneling method:
- Rate Limiting: Cap tunnels at fixed rates (e.g., 10 Mbps each on a 100 Mbps link).
- Priority Queuing: Assign CoS/DSCP markings for preferential treatment.
- Shaping and Policing: Burstable limits prevent saturation.
- Spare Capacity Allocation: Fair sharing or weighted round-robin.
Consult vendor docs for specifics—features vary widely. For multi-tunnel setups, monitor via SNMP or NetFlow to baseline usage.
Real-World Performance Scenarios
Consider a branch office with 1.5 Mbps T1 uplinks: IPsec overhead plus TCP reduces effective throughput to 1-1.2 Mbps. File transfers scale accordingly—a 50 MB file takes 5-7 minutes at full utilization.
In asymmetric links (e.g., 8/1 Mbps DSL), upstream bottlenecks dictate bidirectional speeds. Cloud VPNs like OCI deliver 250-500 Mbps but falter under internet congestion.
Optimization Best Practices
To maximize tunnel efficiency:
- Tune MTU to 1400-1450 bytes, avoiding fragmentation.
- Enable hardware offload (e.g., QAT, IPsec accelerators).
- Use GCM ciphers over CBC for lower CPU load.
- Implement QoS to prioritize latency-sensitive traffic.
- Monitor and profile with tools like iperf over IPsec.
Regular firmware updates unlock performance gains from protocol refinements.
FAQ: Common Tunneling Queries
Q: Can standard tunnels be secured?
A: Yes, by layering IPsec over GRE (GETVPN), combining multicast support with encryption.
Q: What’s the max IPsec speed on consumer routers?
A: Typically 50-200 Mbps; enterprise gear hits 10 Gbps+.
Q: Does IPsec always slow networks more than GRE?
A: Yes, due to crypto overhead, but optimizations close the gap.
Q: How to test tunnel bandwidth?
A: Use iperf3 with -P for parallel streams: iperf3 -c remote_ip -u -b 0.
Q: NAT breaks IPsec?
A: NAT-T encapsulates in UDP/4500, preserving functionality.
Choosing the Right Tunnel for Your Needs
Standard tunnels suit low-risk, high-volume data flows; IPsec is non-negotiable for compliance (e.g., PCI-DSS, HIPAA). Hybrid approaches, like SD-WAN over IPsec, blend agility with security. As networks evolve toward zero-trust models, IPsec’s role expands, demanding savvy bandwidth stewardship.
This comprehensive view equips network engineers to deploy tunnels that balance security, speed, and scalability effectively.
References
- RFC 4301: Security Architecture for the Internet Protocol — IETF. 2005-12 (authoritative standard). https://datatracker.ietf.org/doc/html/rfc4301
- IPSec Bandwidth Overhead Using AES — Packet Pushers. 2015-06-10 (seminal calc, still relevant for AES mechanics). https://packetpushers.net/blog/ipsec-bandwidth-overhead-using-aes/
- Types of VPN Protocols — Palo Alto Networks. 2024 (current). https://www.paloaltonetworks.com/cyberpedia/types-of-vpn-protocols
- Learn About Network Connectivity — Oracle Documentation. 2024-09 (updated). https://docs.oracle.com/en/solutions/oci-network-deployment/learn-network-connectivity1.html