
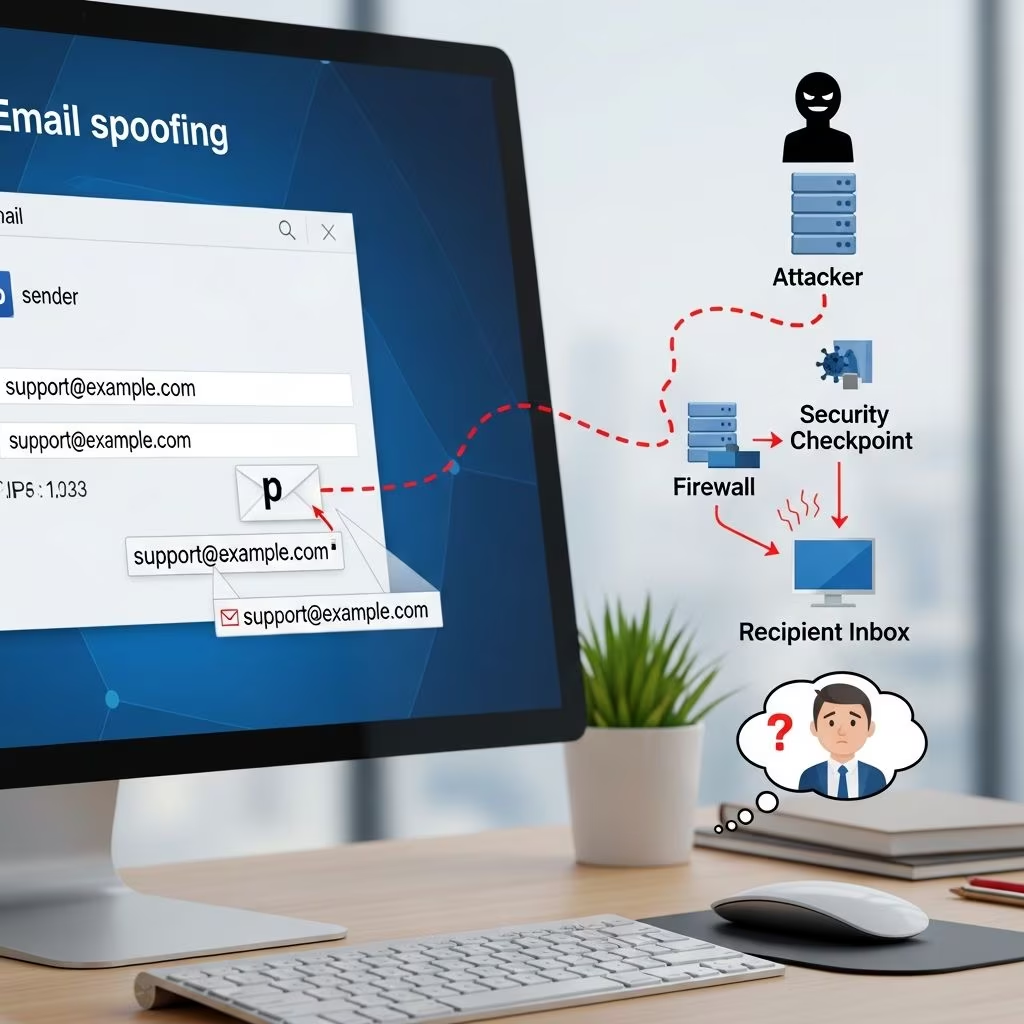
Email remains a cornerstone of modern communication, but its openness makes it a prime target for cybercriminals. One of the most insidious threats is email spoofing, where attackers manipulate message details to masquerade as trustworthy sources. This tactic fuels phishing campaigns, business email compromise, and ransomware distribution, costing organizations billions annually. In this comprehensive guide, we delve into the inner workings of email spoofing, its variants, devastating impacts, and robust countermeasures to fortify your defenses.
The Fundamentals of Email Communication Vulnerabilities
To grasp email spoofing, it’s essential to understand how emails travel across the internet. The Simple Mail Transfer Protocol (SMTP), established decades ago, governs email transmission. SMTP relies on basic sender-recipient exchanges without built-in identity verification, creating a vulnerability attackers exploit.
Every email consists of an envelope and headers. The envelope handles routing, visible only to servers, while headers—displayed to recipients—include fields like ‘From,’ ‘Reply-To,’ and ‘Subject.’ Attackers forge these visible headers to mimic legitimate senders, bypassing casual scrutiny since SMTP doesn’t cross-check them against the envelope.
- Envelope Sender (MAIL FROM): Actual routing address, hidden from users.
- Header From: Forgable display name and address that users see.
- Reply-To: Redirects responses to attacker-controlled inboxes.
This disconnect allows seamless impersonation. For instance, a fraudster could send a message appearing from ‘support@yourbank.com’ while the real origin is a throwaway server.
Common Techniques Employed by Attackers
Spoofers leverage diverse methods to craft convincing fakes. Recognizing these helps in early detection.
Exact Domain Spoofing
Attackers replicate a target’s full domain, such as forging ‘ceo@company.com.’ This relies on SMTP’s lack of authentication, succeeding against unprepared recipients.
Display Name Manipulation
Even with mismatched domains, altering the display name—like showing ‘Your CEO’ from a Gmail address—tricks users who skim inboxes. Visual cues override address checks for hasty readers.
Lookalike Domains and Typosquatting
Subtle domain tweaks evade notice: ‘rnicrosoft.com’ instead of ‘microsoft.com’ using similar characters (e.g., ‘rn’ for ‘m’). Internationalized domains with homoglyphs (visually identical Unicode characters) amplify this.
Reply-To Exploitation
Setting a fraudulent Reply-To ensures responses feed attacker intel, escalating scams.
| Technique | Description | Example |
|---|---|---|
| Exact Spoof | Full domain forgery | ceo@acme.com (fake) |
| Display Name | Name override | ‘Acme CEO’ <fake@gmail.com> |
| Lookalike | Domain mimicry | supp0rt@arnazon.com |
| Reply-To | Response hijack | Reply goes to attacker |
Real-World Consequences and Case Studies
Email spoofing powers high-stakes cybercrimes. In business email compromise (BEC), attackers impersonate executives to authorize fraudulent wire transfers. The FBI reports BEC losses exceeding $2.7 billion in 2022 alone.
Phishing via spoofed emails deploys malware or credential harvesters. A notorious example: the 2016 Uber breach began with a spoofed HR email tricking an employee into granting access.
Individuals face account takeovers, identity theft, and financial ruin. Spoofed ‘bank alerts’ prompt users to fake sites, yielding login details. Malware-laden attachments from ‘trusted colleagues’ compromise devices, enabling ransomware.
- Financial Theft: BEC scams drained $43 billion globally from 2016-2021 (FBI IC3).
- Data Breaches: Spoofing facilitates 90% of breaches (Proofpoint).
- Reputation Damage: Compromised exec emails erode trust.
Spotting Spoofed Emails: User Vigilance Tips
While tech defenses matter, human awareness is crucial. Train yourself with these red flags:
- Unexpected Requests: Urgent demands for funds, info, or clicks from ‘known’ sources.
- Address Mismatches: Hover over sender; verify exact domain.
- Poor Quality: Grammar errors, odd formatting, generic greetings.
- Suspicious Links/Attachments: Hover URLs; avoid unsolicited files.
- Unusual Tone: Pressure, threats, or secrecy from contacts.
Always contact senders via known channels to confirm legitimacy. Use tools like email header analyzers (e.g., MX Toolbox) for deeper inspection.
Technical Defenses: Authentication Protocols
Modern standards plug SMTP gaps. Implement these at domain level:
SPF (Sender Policy Framework)
SPF publishes DNS records listing authorized sending IPs. Receiving servers check if the envelope sender matches, rejecting mismatches. RFC 7208 defines it (2014, authoritative SMTP spec).
DKIM (DomainKeys Identified Mail)
DKIM adds cryptographic signatures to headers/body. Receivers verify via public keys in DNS, ensuring no tampering. RFC 6376 (2011, core standard).
DMARC (Domain-based Message Authentication, Reporting & Conformance)
DMARC builds on SPF/DKIM, dictating actions (quarantine/reject) for failures. It provides reports on spoof attempts. Adopted by Google/Microsoft (2024 mandates).
Implementation Table:
| Protocol | Function | DNS Record Example |
|---|---|---|
| SPF | IP authorization | v=spf1 ip4:192.0.2.0 -all |
| DKIM | Signature | k=rsa;p=PUBLICKEY |
| DMARC | Policy/Reports | v=DMARC1;p=reject;rua=mailto:reports@domain.com |
Advanced Protection Layers
Beyond basics:
- DMARC Alignment: Ensures header/envelope domains match.
- BIMI (Brand Indicators for Message Identification): Displays verified logos in inboxes.
- Anti-Spoofing Gateways: Cloud services like Proofpoint or Mimecast filter anomalies.
- Employee Training: Simulations via KnowBe4 reduce click rates by 50%+.
For enterprises, zero-trust email verifies every message regardless of sender.
Future Trends in Email Security
Regulations like GDPR and emerging U.S. laws mandate DMARC. AI-driven filters analyze behavior patterns, flagging anomalies. Quantum-resistant DKIM variants address encryption threats.
Full SMTP replacement (e.g., DANE) looms, but adoption lags.
Frequently Asked Questions (FAQs)
What is the main difference between email spoofing and phishing?
Spoofing forges sender identity; phishing uses it to steal data/malware.
Can two-factor authentication stop spoofing?
No, but it blocks unauthorized access post-phishing success.
Is email spoofing illegal?
Yes, under CAN-SPAM Act and wire fraud statutes when used maliciously.
How do I check if my domain has SPF?
Use MX Toolbox or dig txt yourdomain.com.
Does Gmail protect against spoofing?
Partially via built-in checks, but custom DMARC enhances it.
References
- Internet Mail Architecture — IETF. 2023-11-15. https://datatracker.ietf.org/doc/html/rfc5321
- Sender Policy Framework (SPF) for Authorizing Use of Domains in Email — IETF. 2014-04-28. https://datatracker.ietf.org/doc/html/rfc7208
- DomainKeys Identified Mail (DKIM) Signatures — IETF. 2011-08-18. https://datatracker.ietf.org/doc/html/rfc6376
- 2023 Internet Crime Report — FBI Internet Crime Complaint Center (IC3). 2024-03-01. https://www.ic3.gov/Media/PDF/AnnualReport/2023_IC3Report.pdf
- What Is Email Spoofing? Definition & Examples — Proofpoint. 2024-05-09. https://www.proofpoint.com/us/threat-reference/email-spoofing