
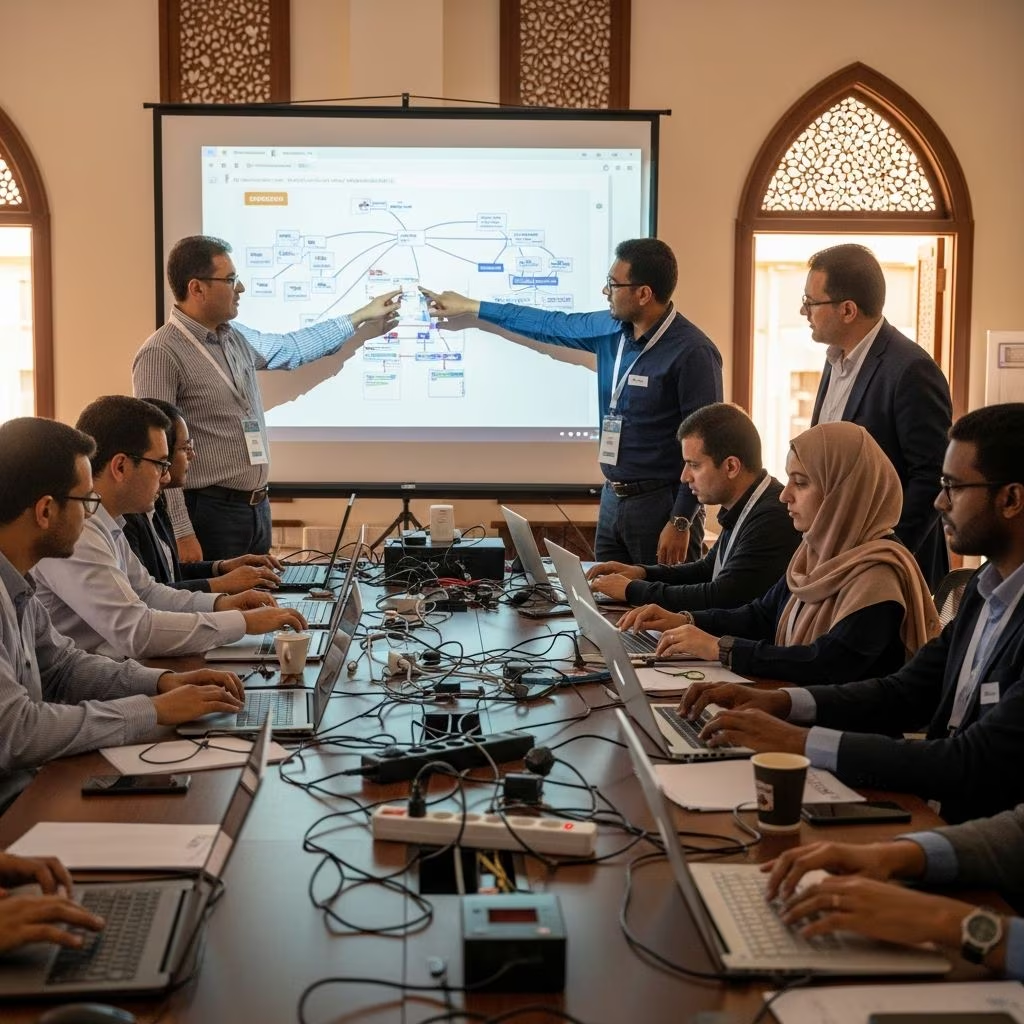
The Domain Name System (DNS) forms the backbone of internet navigation, translating human-readable domain names into machine-readable IP addresses. However, its vulnerability to attacks like cache poisoning has long threatened online trust. In Khartoum, Sudan, a group of dedicated professionals turned theory into practice during an impromptu DNSSEC deployathon, marking a pivotal moment for regional internet security. This event highlighted the power of hands-on learning in advancing DNS Security Extensions (DNSSEC), a protocol that cryptographically signs DNS data to ensure authenticity and integrity.
Understanding the Need for DNSSEC in Emerging Markets
DNSSEC addresses critical flaws in traditional DNS by adding digital signatures to DNS records. Without it, attackers can intercept queries and inject malicious responses, redirecting users to phishing sites or disrupting services. In regions like Africa and the Middle East, where internet growth outpaces security infrastructure, DNSSEC adoption lags despite its proven benefits.
Statistics from authoritative sources underscore the urgency. As of recent reports, only a fraction of top-level domains (TLDs) worldwide have fully deployed DNSSEC validation. In developing nations, challenges include limited technical expertise, resource constraints, and awareness gaps. Yet, successful deployments, such as those by country-code TLDs (ccTLDs), demonstrate feasibility even on modest hardware.
Sudan’s internet ecosystem, characterized by expanding ISP networks and government domains, stood ripe for enhancement. The deployathon responded to this by focusing on practical validation setup, empowering local operators to protect their users from DNS spoofing.
Origins of the Khartoum Initiative
What began as informal discussions among four tech enthusiasts evolved into a full-day marathon of implementation. Motivated by global calls for DNSSEC—echoed by organizations like ICANN and the Internet Society—the group aimed to configure a recursive resolver capable of validating signed zones. Their target: a test domain mimicking real-world Sudanese infrastructure.
Key drivers included rising cyber threats in the region and the simplicity of modern DNSSEC tools. No grand conference was needed; just laptops, a virtual machine, and shared knowledge. This grassroots approach mirrors broader trends in capacity building, where peer-led sessions accelerate adoption faster than lectures alone.
Step-by-Step Journey to DNSSEC Validation
The process unfolded methodically, blending education with execution. Here’s a breakdown of the core phases:
- Environment Setup: Participants provisioned a virtual machine on readily available hardware, installing a stable Linux distribution. This ensured isolation and easy rollback, ideal for experimentation.
- Software Installation: BIND, the de facto DNS server software, was selected for its robust DNSSEC support. Packages were fetched from official repositories, with configurations tuned for security from the outset.
- Key Generation: Critical to DNSSEC, two key pairs were created: the Zone Signing Key (ZSK) for signing individual records and the Key Signing Key (KSK) for chain-of-trust linkage. Tools like
dnssec-keygenstreamlined this, emphasizing rotation schedules to maintain security. - Zone Signing: Resource records for the test zone were digitally signed using
dnssec-signzone. This produced signed zone files ready for authoritative serving. - Resolver Configuration: The recursive resolver was updated with trust anchors, enabling validation. Checks for EDNS(0) support, TCP fallback, and time sync were performed to preempt production pitfalls.
- Testing and Verification: Tools like
dig +dnssecconfirmed signatures, with the resolver successfully validating responses and rejecting tampered ones.
The entire workflow spanned roughly four hours, underscoring DNSSEC’s accessibility. Challenges like initial key mismatches were resolved collaboratively, turning obstacles into teachable moments.
Technical Deep Dive: Keys and Validation Mechanics
DNSSEC’s strength lies in its public-key infrastructure (PKI). The KSK anchors trust via the root zone, while the ZSK handles granular signing. During the deployathon, participants explored delegation signer (DS) records, which link parent and child zones in the chain of trust.
Validation occurs at recursive resolvers: upon receiving a response, the resolver verifies signatures against public keys, traversing up to the trust anchor. Failure—due to tampering or misconfiguration—triggers SERVFAIL, alerting users to potential issues.
| Component | Purpose | Deployathon Role |
|---|---|---|
| ZSK | Signs DNS records | Generated for test zone |
| KSK | Signs ZSK; DS record | Uploaded to parent |
| Trust Anchor | Root validation point | Configured in resolver |
| RRSIG | Signature records | Verified via dig |
This table illustrates the interplay, highlighting why both signing and validation are essential for end-to-end protection.
Overcoming Regional Hurdles
Sudan-specific issues, such as intermittent power and bandwidth, tested resilience. Solutions included offline key generation and battery-backed setups. Broader barriers—like minimal IPv6 support—were noted, with recommendations for incremental upgrades.
ICANN’s regional programs have aided similar efforts, providing checklists for pre-deployment audits. The deployathon aligned with these, proving that even without external funding, motivated teams can succeed.
Broader Implications for African DNS Security
Khartoum’s success ripples outward. It inspired discussions on scaling to national ccTLDs like .sd, potentially shielding government and financial services. Globally, DNSSEC validation rates hover below 20% for resolvers, per deployment trackers, but events like this nudge progress.
Future steps include ISP integration and public awareness campaigns. As threats evolve—think quantum risks to current crypto—DNSSEC’s role as a foundational layer grows undeniable.
Lessons Learned and Best Practices
From the session:
- Start small: Test zones build confidence before production.
- Automate where possible: Tools like NSD or Knot simplify management.
- Monitor actively: Use stats on validation failures to refine.
- Collaborate regionally: Share configs via forums like DNSSEC-Deployment.org.
These practices, drawn from hands-on experience, equip others for swift deployment.
FAQ: DNSSEC Essentials
What is a DNSSEC deployathon?
A intensive, practical workshop focused on deploying DNSSEC signing and validation.
Is DNSSEC hard to implement?
Not with modern tools; a basic setup takes hours for experienced users.
Why validate in Sudan?
To protect local users from DNS hijacking amid growing internet reliance.
What’s next after deployment?
Key rollover, monitoring, and advocacy for TLD signing.
Can anyone host a deployathon?
Yes—minimal resources needed; leverage open-source guides.
Call to Action: Secure Your DNS Today
The Khartoum deployathon proves DNSSEC is within reach. Network operators, start with a VM, follow official docs, and join the global effort. Secure DNS today safeguards tomorrow’s internet.
References
- Two Years of Supporting DNSSEC Deployment in Africa and the Middle East — ICANN. 2022-10-27. https://www.icann.org/en/blogs/details/two-years-of-supporting-dnssec-deployment-in-africa-and-the-middle-east-27-10-2022-en
- Measuring the Practical Impact of DNSSEC Deployment — Lian et al., USENIX Security. 2013. https://cseweb.ucsd.edu/~wlian/papers/lian_dnssec_usenixsec13.pdf (Authoritative despite age due to foundational measurement methodology).
- DNSSEC Deployment Site — Verisign (official DNSSEC forum). Ongoing. https://www.dnssec-deployment.org