
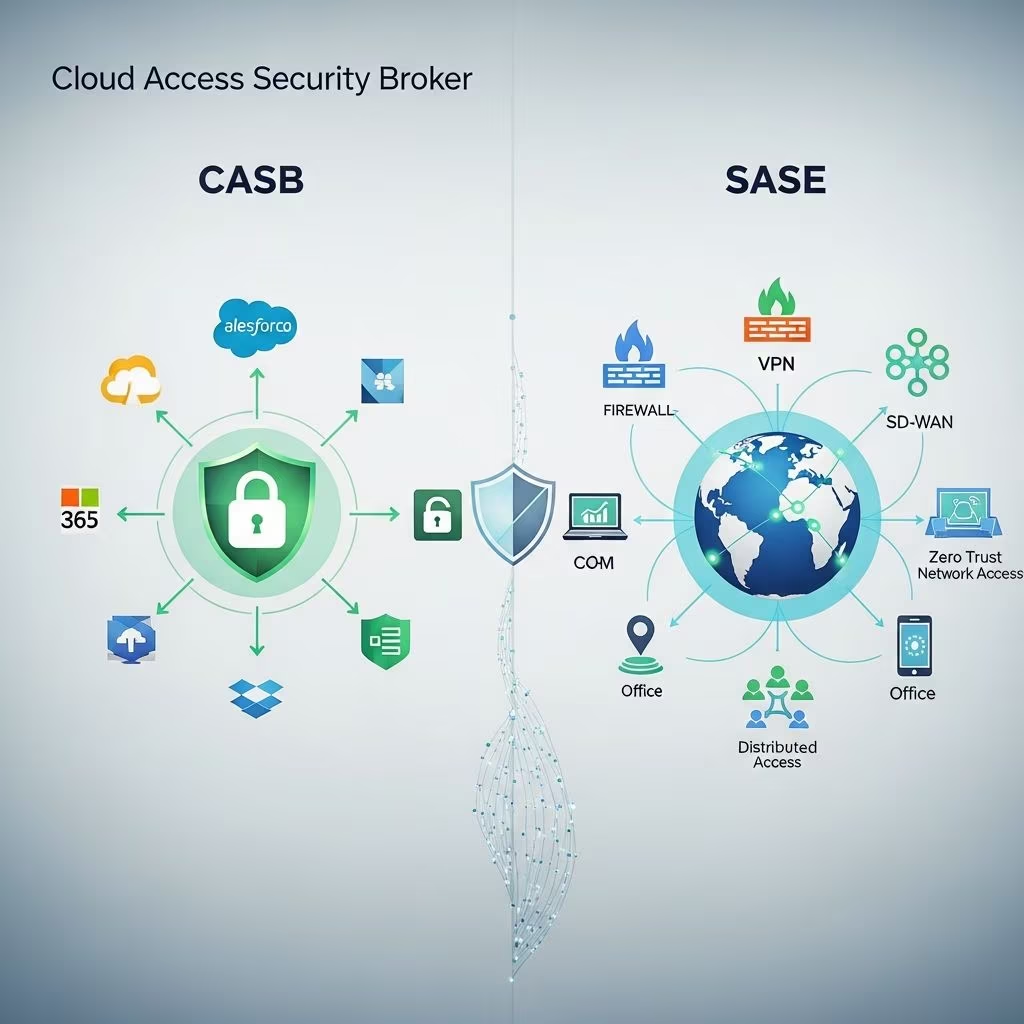
In today’s digital landscape, organizations face mounting challenges in securing cloud resources amid widespread remote work and multi-cloud adoption. Two prominent solutions, Cloud Access Security Broker (CASB) and Secure Access Service Edge (SASE), have emerged to address these issues, but they serve distinct purposes. This article delves into their functionalities, contrasts their approaches, and guides IT leaders on selecting the right tool—or combination—for robust protection.
Understanding Cloud Access Security Broker (CASB)
CASB acts as an intermediary enforcer between users and cloud services, providing critical visibility and control over cloud application usage. Originally designed to tackle the rise of Software-as-a-Service (SaaS) applications, CASB solutions monitor traffic, enforce policies, and mitigate risks associated with unauthorized access or data exfiltration.
At its core, CASB operates through three primary deployment modes: API-based, proxy-based, and agent-based. API integration allows deep scanning of cloud environments like Microsoft 365 or Google Workspace for compliance and anomalies. Proxy methods intercept traffic in real-time for inline inspection, while agents installed on endpoints offer granular control over user activities.
- Visibility: Discovers shadow IT by identifying unsanctioned apps.
- Data Protection: Implements Data Loss Prevention (DLP) to prevent sensitive information leaks.
- Threat Defense: Detects malware and anomalous behaviors in cloud sessions.
- Compliance: Ensures adherence to standards like GDPR or HIPAA through activity logging.
CASB excels in environments heavy on SaaS, where traditional firewalls fall short. According to Gartner’s 2023 Magic Quadrant for Security Service Edge, CASB capabilities remain vital for 85% of enterprises using cloud apps, highlighting its enduring relevance.
Decoding Secure Access Service Edge (SASE)
Coined by Gartner in 2019, SASE represents a converged framework that blends networking and security into a cloud-native delivery model. Rather than relying on data center appliances, SASE delivers services from global points of presence (PoPs), ensuring low-latency access for distributed users.
SASE incorporates multiple stackable services: Secure Web Gateway (SWG) for web filtering, Cloud Access Security Broker (often embedded), Firewall-as-a-Service (FWaaS), and Zero Trust Network Access (ZTNA). This holistic approach shifts security from perimeter-based to identity-centric, verifying every connection regardless of location.
| SASE Component | Function |
|---|---|
| SD-WAN | Optimizes WAN connectivity for branches and remote users. |
| ZTNA | Provides secure, least-privilege access to private apps. |
| SWG & CASB | Filters web traffic and secures cloud apps. |
| FWaaS | Inspects traffic with next-gen firewall rules. |
SASE’s strength lies in its unification, reducing complexity from managing disparate tools. A 2024 Forrester report notes that SASE adopters experience 40% faster incident response due to centralized policy management.
Core Distinctions: CASB Compared to SASE
While both enhance cloud security, CASB focuses narrowly on cloud app governance, whereas SASE encompasses broader network optimization and edge security. CASB is typically a point solution deployable standalone or integrated into larger stacks, but SASE demands a platform-wide commitment for full benefits.
Key differentiators include:
- Scope: CASB targets SaaS/IaaS/PaaS; SASE covers the entire attack surface, including on-premises and internet-bound traffic.
- Delivery Model: CASB supports hybrid agent/proxy/API; SASE is inherently cloud-delivered via PoPs.
- Networking Integration: Absent in CASB; central to SASE with SD-WAN and routing.
- Scalability: CASB scales per app; SASE auto-scales globally.
In essence, CASB is a specialized tool within the SASE ecosystem, often functioning as its cloud security layer. Organizations using CASB alone may need additional solutions for WAN security, leading to integration silos.
Deployment Strategies and Real-World Applications
Implementing CASB involves assessing cloud app inventory and choosing deployment modes. For instance, API connectors suit compliance-heavy setups, while proxies fit dynamic environments. Challenges include potential performance overhead from traffic rerouting and ensuring coverage for unmanaged devices.
SASE deployment, conversely, requires evaluating PoP proximity for latency and migrating from legacy VPNs or MPLS. Vendors like Zscaler or Cato Networks offer turnkey platforms, easing transitions. A common pitfall is underestimating policy convergence, which can take months for complex enterprises.
Case in point: A global retailer deployed CASB to curb shadow IT, reducing unauthorized SaaS by 60% within quarters. Scaling to SASE later unified their remote access, cutting costs by consolidating 15 tools into one.
Advantages and Limitations of Each Approach
CASB Benefits and Drawbacks
Pros:
- Rapid deployment for immediate cloud visibility.
- Cost-effective for SaaS-centric orgs.
- Granular controls like adaptive authentication.
Cons:
- Limited to cloud traffic; ignores network-layer threats.
- Integration complexity with existing security stacks.
- Vendor lock-in risks with app-specific APIs.
SASE Strengths and Challenges
Pros:
- Unified management simplifies operations.
- Superior performance for global teams.
- Future-proofs against evolving threats.
Cons:
- Higher upfront costs and vendor dependency.
- Steep learning curve for policy design.
- Dependency on internet reliability.
When to Choose CASB, SASE, or Both
Opt for CASB if your priority is SaaS governance without overhauling networks—ideal for mid-sized firms with moderate remote work. SASE suits enterprises needing end-to-end security convergence, especially with branch offices or IoT sprawl.
Hybrid strategies prevail: Embed CASB within SASE for comprehensive coverage. Gartner predicts 50% of enterprises will adopt SSE (SASE’s security subset, including CASB) by 2025, signaling a shift toward integrated models.
Future Trends Shaping CASB and SASE Evolution
AI-driven analytics are enhancing both: CASB now predicts insider threats via behavior baselines, while SASE leverages ML for autonomous threat hunting. Convergence with SSE platforms blurs lines further, with CASB as a core module.
Zero Trust principles amplify adoption, as regulations like NIST 800-207 mandate continuous verification. By 2026, IDC forecasts SASE market growth to $15B, driven by 5G and edge computing demands.
Frequently Asked Questions (FAQs)
What exactly does CASB stand for?
Cloud Access Security Broker—a tool mediating access to cloud services for security and compliance.
Is SASE a replacement for CASB?
No, SASE often incorporates CASB functionality alongside networking services for broader protection.
Can CASB work with on-premises apps?
Limited; it’s optimized for cloud but can proxy some hybrid traffic.
How does SASE improve user experience?
By delivering services from nearby PoPs, reducing latency compared to backhauling to data centers.
What are typical costs for CASB vs SASE?
CASB: $5-15/user/month; SASE: $10-30/user/month, scaling with features.
References
- Cloud Access Security Brokers Magic Quadrant — Gartner. 2023-10-01. https://www.gartner.com/en/documents/4022356
- The Forrester Wave™: Security Service Edge Solutions — Forrester. 2024-02-15. https://www.forrester.com/report/The-Forrester-Wave-Security-Service-Edge-Solutions-Q1-2024/RES180015
- Secure Access Service Edge (SASE) Reference Architecture — NIST. 2023-11-20. https://nvlpubs.nist.gov/nistpubs/ir/2023/NIST.IR.8355.pdf
- Worldwide Security Service Edge Forecast — IDC. 2025-01-10. https://www.idc.com/getdoc.jsp?containerId=US51234525