
The evolution of wireless networking has demanded more sophisticated tools for managing sprawling deployments of access points. At the heart of this advancement lies CAPWAP, or Control and Provisioning of Wireless Access Points, a standardized protocol designed to streamline operations in large-scale wireless local area networks (WLANs). Developed by the Internet Engineering Task Force (IETF), CAPWAP facilitates communication between a central controller and multiple wireless termination points (WTPs), commonly referred to as access points (APs). This centralization shifts complex tasks like authentication, policy enforcement, and radio management from individual devices to a unified platform, enhancing efficiency and scalability.
Core Architecture of CAPWAP
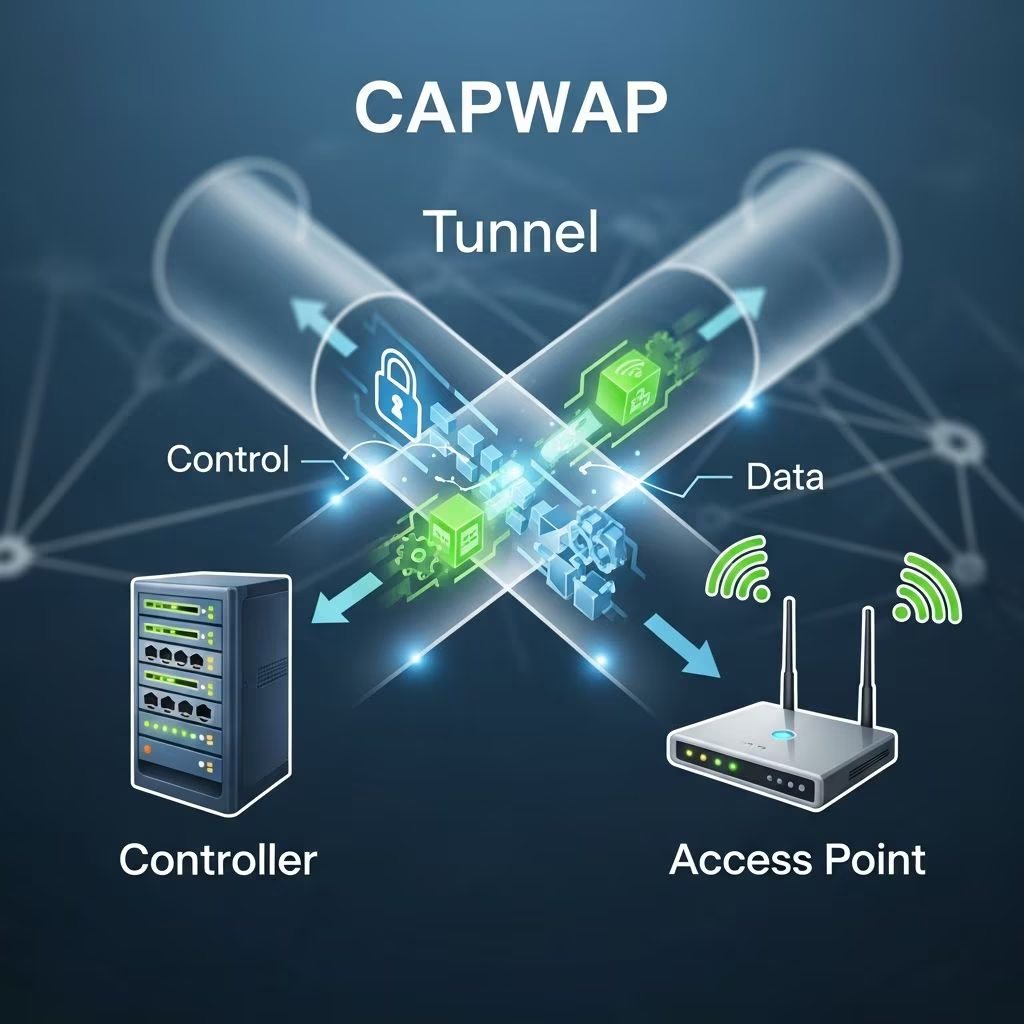
CAPWAP operates on a client-server model where the wireless LAN controller (WLC) acts as the server, overseeing a fleet of WTPs. These WTPs serve as remote radio interfaces, handling the physical layer transmission while relying on the controller for higher-level decisions. The protocol is engineered to be layer-2 agnostic, meaning it functions over IP networks regardless of the underlying Ethernet or other transport mechanisms.
Key components include:
- Wireless Termination Point (WTP): The AP that connects end-user devices to the network, processing radio signals and forwarding data.
- Access Controller (AC): The central brain that configures, monitors, and provisions WTPs.
- Control Channel: Handles configuration, management, and security exchanges using UDP port 5246.
- Data Channel: Tunnels user traffic and wireless frames via UDP port 5247.
This bifurcated channel design ensures management traffic does not interfere with high-volume data flows, optimizing performance in enterprise environments.
Discovery and Secure Association Process
Before any management can occur, WTPs must locate and join an AC. CAPWAP’s discovery mechanism begins with the WTP broadcasting discovery requests across the network. These UDP packets include details like the WTP’s identity, supported bindings, and hardware descriptors. The AC responds with its own details, such as IP address, capabilities, and available firmware images.
Once discovered, the devices negotiate a secure DTLS (Datagram Transport Layer Security) tunnel. This encrypted session protects all subsequent control messages from eavesdropping or tampering. The join process culminates in the WTP receiving a configuration update from the AC, which may include firmware upgrades, radio settings, and security policies. This automated onboarding is crucial for zero-touch provisioning in dynamic environments like campuses or stadiums.
| Phase | Action by WTP | Action by AC |
|---|---|---|
| Primary Discovery | Sends broadcast/multicast request | Monitors for requests |
| Response | Receives AC details | Sends unicast response |
| Join | Initiates DTLS handshake | Validates and configures |
| Run State | Operates under AC control | Monitors and provisions |
Split MAC vs. Local MAC Architectures
CAPWAP supports two primary operational modes, each suiting different network topologies. In Split MAC mode, the WTP handles only low-level 802.11 PHY and MAC functions, encapsulating all frames—including data, management, and control—into CAPWAP tunnels sent to the AC. The controller then performs higher-layer processing, such as encryption/decryption, QoS marking, and mobility handoffs. This mode excels in scenarios requiring tight central oversight, like high-security corporate networks.
Conversely, Local MAC mode allows the WTP to process most 802.11 functions locally. Data frames are bridged directly to the wired network as Ethernet, bypassing the data tunnel for efficiency. Management frames, however, still traverse the control channel to the AC. This hybrid approach reduces controller load, making it ideal for distributed deployments with abundant local switching capacity.
- Split MAC Benefits: Uniform policy enforcement, seamless roaming, reduced AP complexity.
- Local MAC Benefits: Lower latency, higher throughput, resilience to controller failures.
Bindings and Extensibility for Diverse Radios
One of CAPWAP’s strengths is its binding mechanism, which adapts the protocol to specific wireless technologies. The base CAPWAP spec (RFC 5415) provides the generic framework, while bindings like RFC 5416 tailor it for IEEE 802.11 WLANs. A binding defines how radio-specific frames are encapsulated, decrypted, and processed.
This extensibility future-proofs CAPWAP for emerging standards, such as Wi-Fi 6/6E or even non-802.11 technologies like private LTE. Vendors implement custom bindings, but adherence to IETF guidelines ensures interoperability across multi-vendor setups.
Security Mechanisms in CAPWAP Deployments
Security is paramount in wireless management. CAPWAP mandates DTLS for all control plane communications, employing certificate-based authentication to verify WTP identities against the AC’s trust store. Data channels can optionally use IPsec or rely on 802.11 encryption.
Additional protections include:
- Replay protection via sequence numbers.
- Message integrity checks with HMAC.
- Role-based access controls for provisioning tasks.
In practice, this fortifies against man-in-the-middle attacks and rogue AP insertions, a common threat vector in enterprise WLANs.
Advantages for Enterprise Wireless Management
Adopting CAPWAP yields transformative benefits:
- Centralized Oversight: Admins configure thousands of APs from one console, slashing operational overhead.
- Scalability: Supports massive deployments without proportional hardware increases.
- Consistency: Uniform RF policies prevent interference and optimize coverage.
- Mobility: Controllers handle fast roaming and session continuity.
- Over-the-Air Updates: Seamless firmware pushes minimize downtime.
Quantitative gains include up to 50% reduction in management time, per industry benchmarks, alongside improved spectral efficiency.
Real-World Implementations and Vendor Support
Major vendors like Cisco integrate CAPWAP natively in their WLC platforms, such as the Catalyst series. Cisco’s documentation highlights its use in outdoor/industrial APs, where rugged devices join controllers over WAN links. Forescout and other NAC solutions also leverage CAPWAP for visibility into AP behaviors.
In cloud-managed services like Cisco Meraki or Aruba Central, CAPWAP evolves into lightweight DTLS tunnels to virtual controllers, blending on-premises reliability with SaaS agility.
Challenges and Best Practices
Despite strengths, CAPWAP introduces hurdles like single-point-of-failure risks (mitigated by redundancy) and tunnel overhead (addressed via Local MAC). Best practices include:
- Deploying high-availability controller clusters.
- Monitoring DTLS session health.
- Segmenting control/data traffic on separate VLANs.
- Regularly validating bindings against firmware updates.
Future Directions for CAPWAP
As Wi-Fi 7 and beyond emerge, CAPWAP’s extensible design positions it well. Potential enhancements include native support for multi-link operations (MLO) and AI-driven radio optimization signaled via control messages. Integration with SDN controllers could further abstract wireless into unified fabric management.
Frequently Asked Questions
What ports does CAPWAP use?
CAPWAP employs UDP 5246 for control and 5247 for data channels.
Is CAPWAP compatible with autonomous APs?
No, it requires controller-capable ‘lightweight’ APs; autonomous modes use different protocols like SNMP.
Can CAPWAP span WAN links?
Yes, with proper NAT traversal and security configurations.
How does CAPWAP handle AP failures?
Controllers detect heartbeats; failed APs can rejoin automatically upon recovery.
Is CAPWAP vendor-specific?
The IETF standard promotes interoperability, though proprietary extensions exist.
References
- RFC 5415 – Control And Provisioning of Wireless Access Points (CAPWAP) Protocol Specification — IETF. 2009-03-18. https://datatracker.ietf.org/doc/html/rfc5415
- RFC 5416 – Control And Provisioning of Wireless Access Points (CAPWAP) Protocol Binding for IEEE 802.11 — IETF. 2009-03-18. https://datatracker.ietf.org/doc/html/rfc5416
- Control and Provisioning of Wireless Access Points – Cisco IW9165E Configuration Guide — Cisco Systems. 2023 (accessed 2026). https://www.cisco.com/c/en/us/td/docs/wireless/outdoor_industrial/iw9165e/software/configuration/b-iw9165e-scg-17-14/m-control-and-provisioning-of-wireless-access-points.pdf